 Dailysabah
France Accuses Musk of Election Meddling and Online Harassment
Article Content

- •Elon Musk is accused of leading online harassment campaigns against European leaders.
- •Foreign interference is a growing concern ahead of France's 2027 presidential election.
- •Fake social media accounts linked to an Israeli company are reportedly fueling tensions.
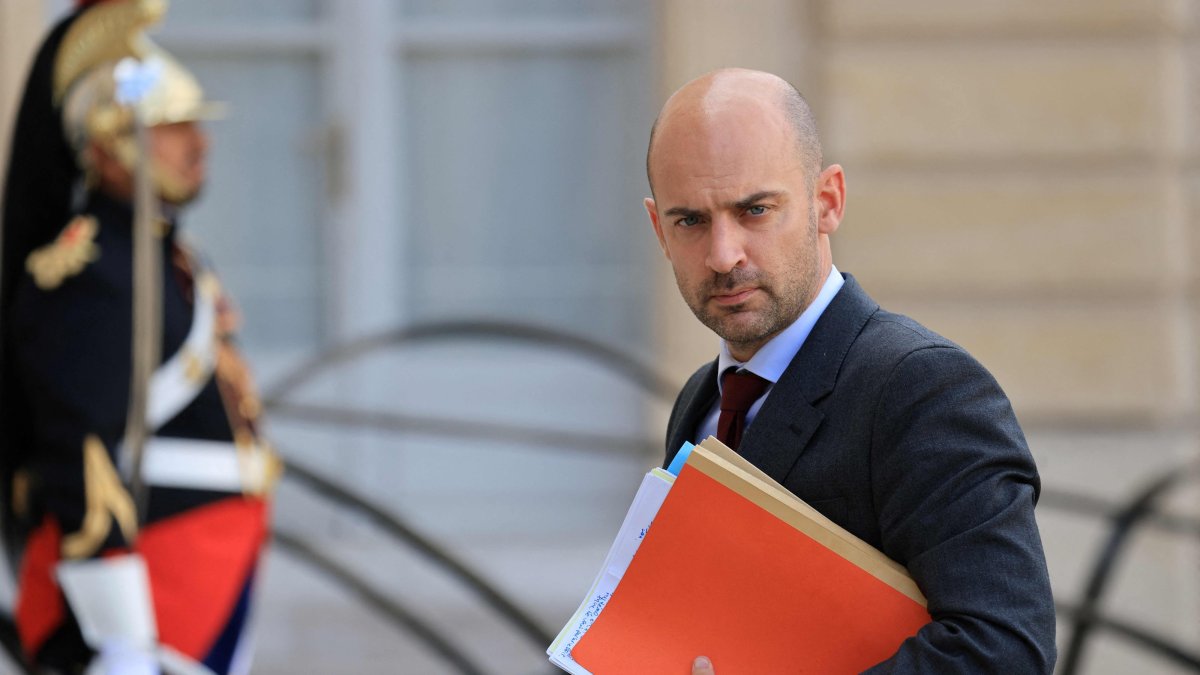
French Foreign Minister Jean-Noel Barrot accused Elon Musk of orchestrating online harassment campaigns against European leaders, warning of foreign interference ahead of France's 2027 presidential election. Barrot highlighted that foreign actors are exploiting divisive issues such as immigration and the Israeli-Palestinian conflict to influence public debate. He also mentioned fake social media accounts created by an Israeli company to provoke disputes. The minister linked hostile narratives to protests by French high school students, citing involvement from Russia, China, Iran, and supporters of Donald Trump's MAGA movement. Barrot emphasized that France will not tolerate any foreign interference, asserting it as a matter of sovereignty. The warnings come as the political landscape in France becomes increasingly polarized, with far-right politician Marine Le Pen expected to play a significant role in the upcoming election.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific actions is Musk accused of?
What are the implications for the 2027 election?
How is France responding to these allegations?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…