 Lemonde.Fr
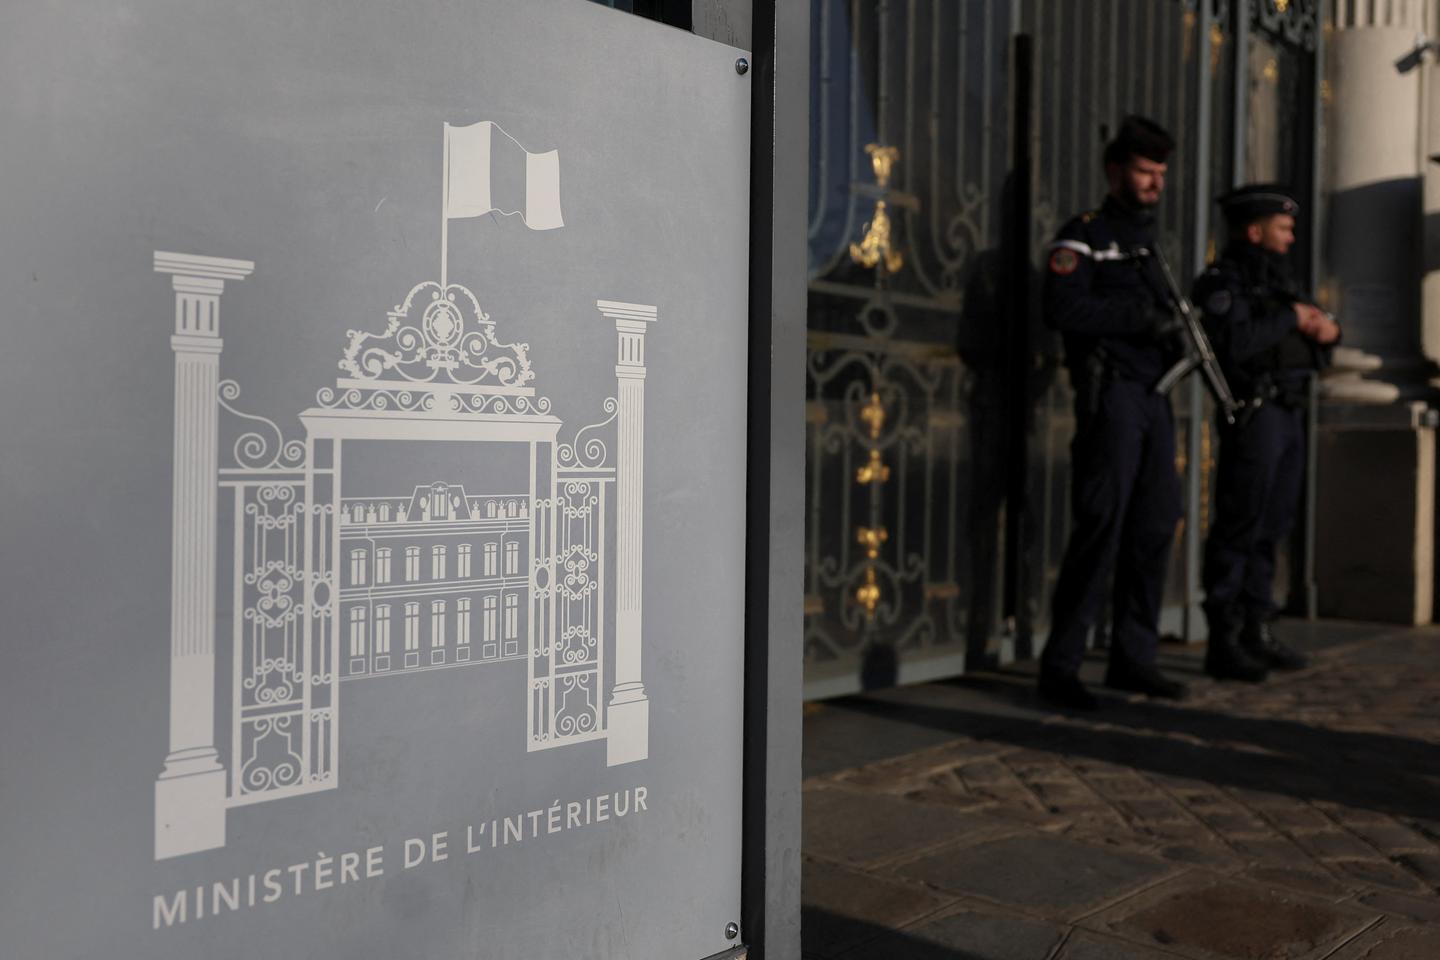
France Dismantles Nine Chinese Espionage Stations Targeting Dissidents
Article Content

- •France closed nine Chinese police stations used for espionage against dissidents.
- •Three Chinese nationals involved in the operations are facing expulsion from France.
- •The Chinese government denies wrongdoing, claiming the stations were for expatriate services.
France has shut down nine clandestine Chinese 'police stations' that were allegedly used to monitor and intimidate the Chinese diaspora and dissidents. The operations were dismantled following a year-long investigation by French counter-intelligence services. Three Chinese nationals accused of running these stations are facing expulsion, with two already removed from the country. The stations reportedly operated under the guise of community associations, gathering intelligence on regime opponents. The Chinese government claims these sites were merely 'overseas service centres' for expatriates. This incident highlights growing concerns about Chinese espionage activities in Western nations, particularly regarding the safety of dissidents. In a related case, four Chinese men were arrested in February for attempting to set up a satellite dish to intercept sensitive data. The situation reflects a broader trend of foreign interference in domestic affairs, particularly from China.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…