 Maritime-Executive
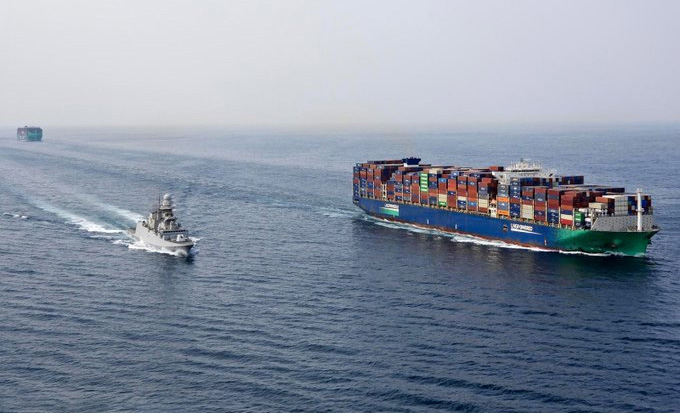
French Frigate Shoots Down Drone Threatening CMA CGM Ship
Article Content

- •A French frigate shot down a drone threatening a CMA CGM container ship.
- •The incident occurred on October 1 in the Bab el-Mandeb Strait amid heightened regional tensions.
- •CMA CGM crews are increasingly uneasy about sailing through the Red Sea due to Houthi threats.
On October 1, a French frigate, Languedoc, shot down a drone it deemed threatening to the CMA CGM container ship Champs Elysées while it was transiting the Bab el-Mandeb Strait. The incident occurred during heightened tensions in the region, with fears of Houthi attacks on vessels. The French Navy has been escorting commercial ships in the Red Sea since late 2023 due to threats from Houthi rebels. The CMA CGM vessel was on a scheduled route from Singapore to Le Havre, with a capacity of 23,000 containers. Following the incident, concerns have increased among CMA CGM crews, leading to some refusing to sail the route. The French government has pledged military support to protect shipping interests in the region. The situation remains tense, but recent reports indicate a stabilization in shipping activities after previous attacks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track CMA CGM in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the nature of the threat?
What actions is France taking in the region?
Are there ongoing threats to shipping in the Red Sea?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…