 edge.prnewswire.com
GEP Recognized as Leader in Supply Chain Platforms by Forrester
Article Content

- •GEP was named a Leader in Forrester's Supply Chain Platforms evaluation.
- •The company received a perfect score in the Innovation criterion.
- •GEP Quantum Intelligence enhances supply chain control through AI integration.
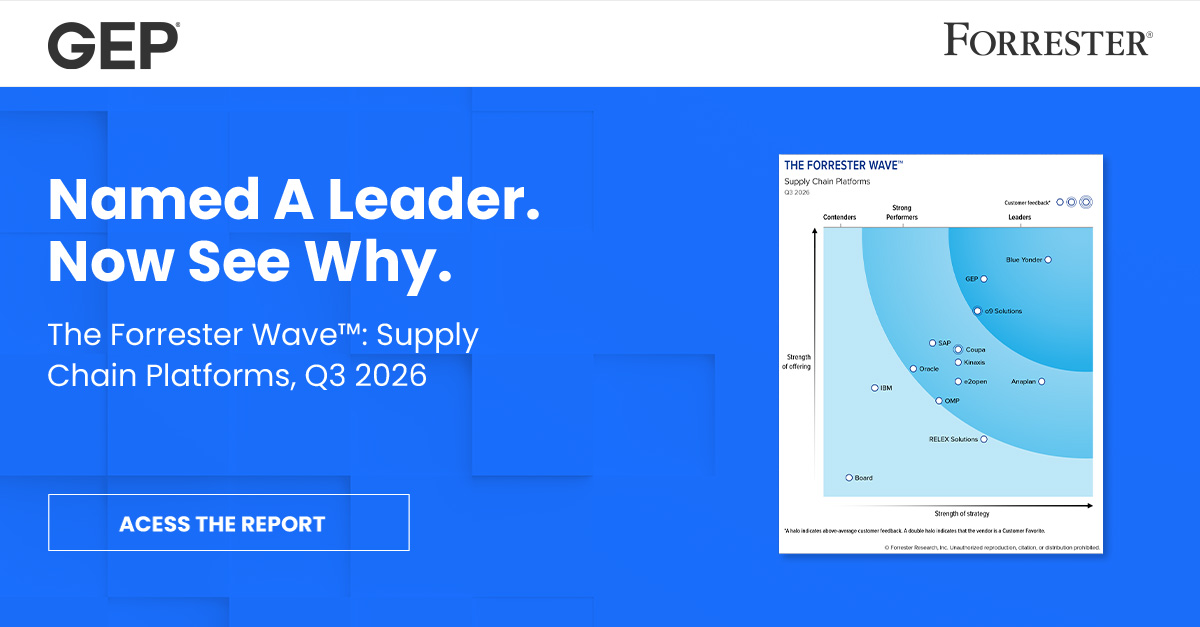
GEP has been named a Leader in The Forrester Wave™: Supply Chain Platforms, Q3 2026, receiving the highest score of 5 out of 5 in the Innovation criterion. This recognition highlights GEP's advancements in AI-native architecture, agentic AI, and autonomous decision-making. GEP Quantum Intelligence integrates sourcing, supplier intelligence, and risk management, providing enterprises with enhanced control over their supply chains. The evaluation included 13 significant supply chain platform providers, and GEP's capabilities were praised for their comprehensive source-to-pay functions and strong network collaboration. Customers reported high satisfaction with GEP's service and transparency. This accolade follows similar recognitions from Gartner, IDC, and The Hackett Group, reinforcing GEP's leadership in procurement and supply chain technology.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track GEP in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What criteria did Forrester evaluate?
What is GEP Quantum Intelligence?
How did customers respond to GEP's services?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…