 Gna.Gh
Ghana's Cybersecurity Framework Faces Exploitation Risks Amid Institutional Gaps
Article Content

- •Cyber attackers are exploiting institutional gaps in Ghana's cybersecurity framework.
- •Collaboration among financial institutions and regulators is essential for effective threat intelligence sharing.
- •The Bank of Ghana is establishing digital forensic laboratories to enhance cybersecurity efforts.
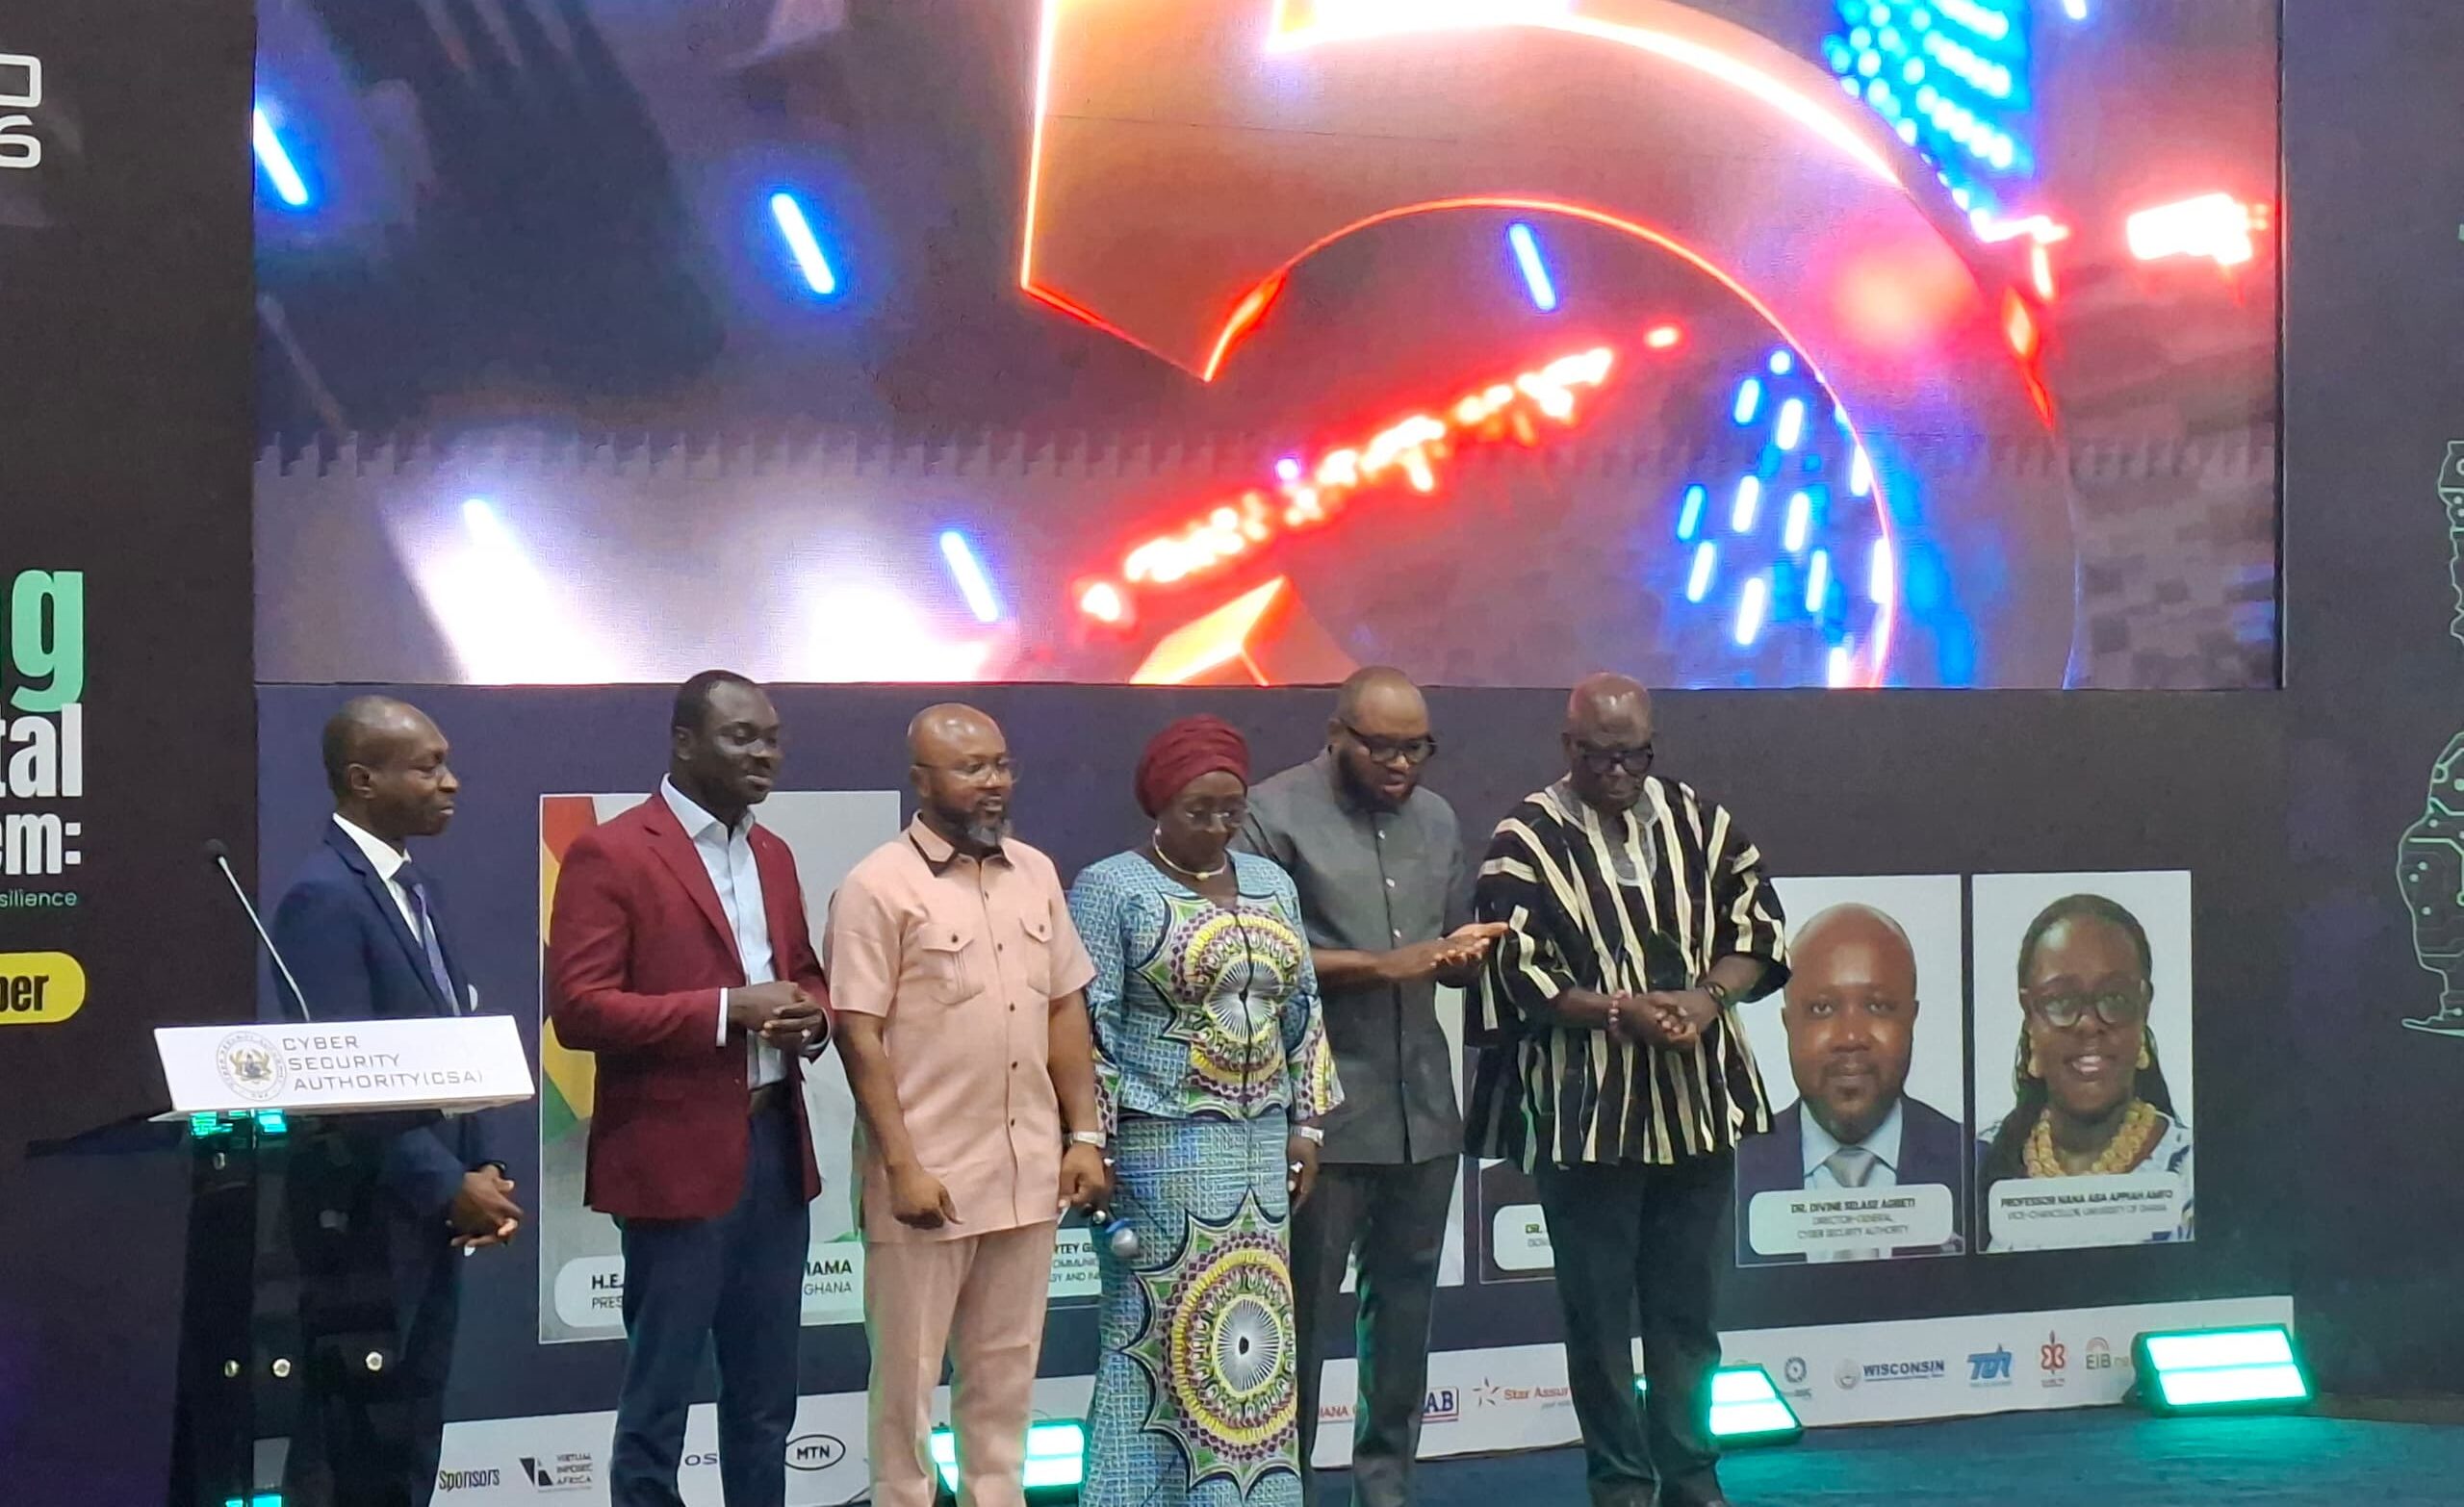
Ghana's Cyber Security Authority (CSA) has reported that cyber attackers are increasingly exploiting gaps in the country's cybersecurity framework. Dr. Divine Selase Agbeti emphasized the need for financial institutions to utilize actionable threat intelligence to proactively combat cyber threats. He highlighted the importance of collaboration among financial institutions, telecommunications companies, and regulators to improve information sharing and intelligence exchange. The recurring nature of cyberattacks suggests inadequate intelligence sharing among defenders. The Bank of Ghana is working with the CSA to establish digital forensic laboratories to enhance the analysis of digital evidence. This situation coincides with National Cybersecurity Awareness Month, which aims to promote cybersecurity best practices. The CSA's call for collaboration underscores the critical need for a unified response to strengthen Ghana's cyber resilience.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What are the institutional gaps mentioned?
What is being done to address these gaps?
How can financial institutions improve their cybersecurity posture?
Continue Reading
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…