 www.pcgamer.com
Gigabyte Control Center Software Vulnerabilities Expose Kernel to Local Attacks
Article Content

- •Multiple vulnerabilities in Gigabyte Control Center software allow local privilege escalation.
- •Affected drivers include GVCIDrv64.sys and gdrv3.sys, requiring immediate software updates.
- •The vulnerabilities are not exploitable remotely, limiting the risk to local attackers only.
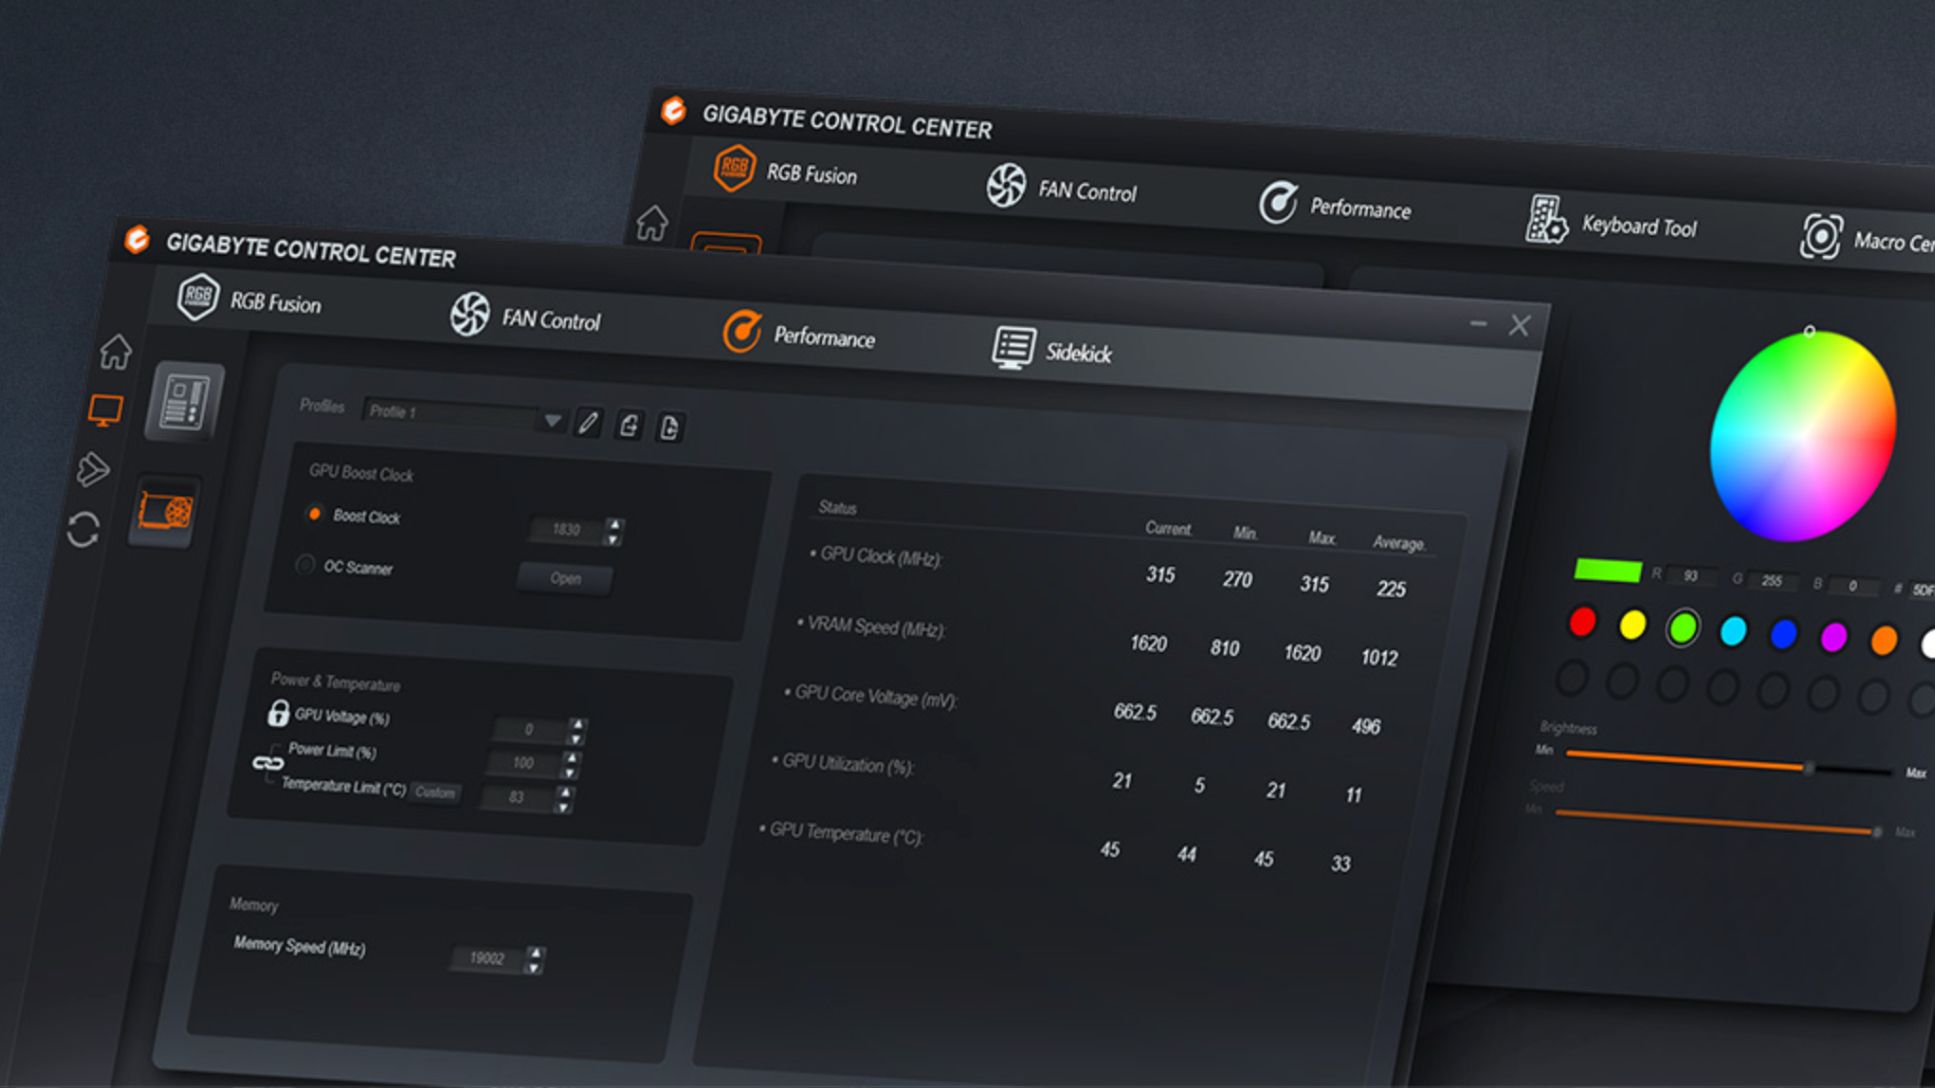
Gigabyte has acknowledged multiple vulnerabilities in its Control Center software affecting GIGABYTE motherboards. The vulnerabilities exist in the kernel drivers GVCIDrv64.sys and gdrv3.sys, allowing local attackers to elevate privileges to the kernel level, potentially leading to complete system compromise. The flaws arise from insufficient access control and improper validation of input parameters in the IOCTL interfaces. While the risk of exploitation is limited to local attackers, Gigabyte has released a patch in version 26.08.28.01 and later to mitigate these issues. Security researchers Mohamed Alzhrani (0xMaz) and Subhan Sultanov (me1n) were credited for their role in identifying and addressing the vulnerabilities. Users are strongly advised to update their software to the latest version to ensure protection against these vulnerabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Gigabyte in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…