 Github.Blog
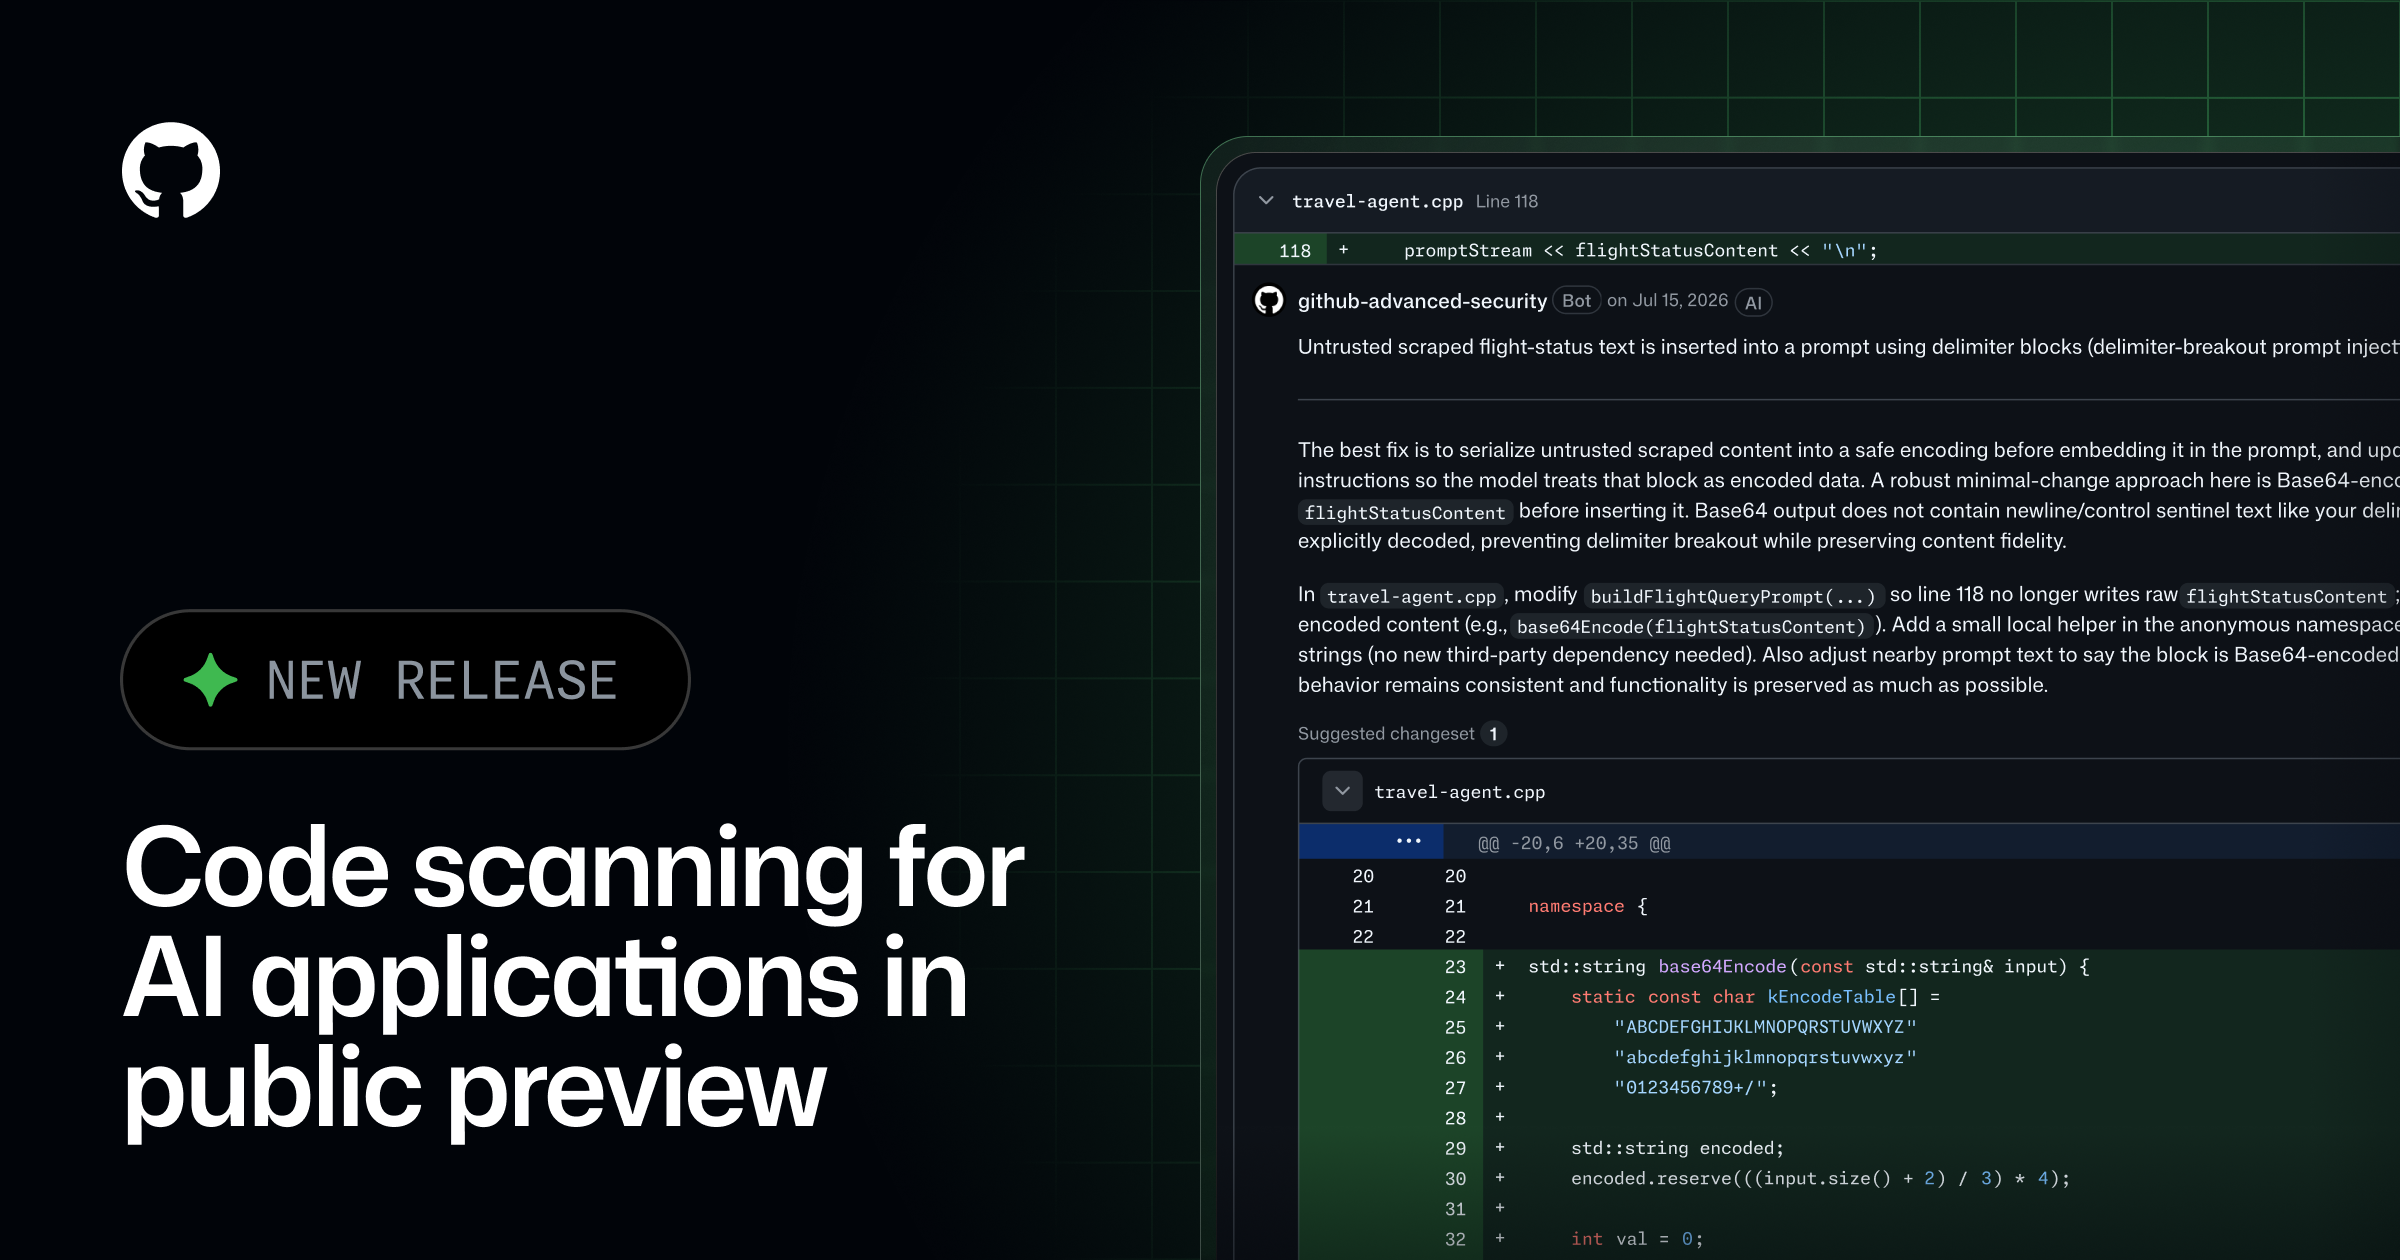
GitHub Launches AI Applications Code Scanning in Public Preview
Article Content

- •New AI applications code scanning feature launched in public preview.
- •Detects vulnerabilities like indirect prompt injection and excessive agency.
- •Available for GitHub Advanced Security users; not for GitHub Enterprise Server.
GitHub has introduced a new code scanning feature for AI applications, now in public preview, which detects vulnerabilities such as indirect prompt injection, sensitive information disclosure, and excessive agency. This feature is available for organizations using GitHub Advanced Security and scans pull requests automatically. Indirect prompt injection is highlighted as a risk, as it can manipulate AI agent behavior through untrusted content. The scanning tool flags code paths where untrusted content may reach AI models with access to sensitive systems. Organizations are encouraged to review alerts and apply mitigation guidance before merging code. The feature is currently not available for GitHub Enterprise Server. No specific CVEs or have been reported related to this feature.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What vulnerabilities does the scanning feature detect?
Who can use the AI applications scanning feature?
Is there any active exploitation related to this feature?
Continue Reading
 Brotli Decoder Vulnerability Patched Across Multiple Linux Distributions A vulnerability, CVE-2026-111497, affecting the Brotli decoder has been patched in various Linux distributions, including Fedora 44 and Oracle Linux 10. The flaw allows for an out-of-bounds write, which could potentially enable attackers to execute arbitrary code. The vulnerability was published on October 22, 2026…