 Grahamcluley
Google Fixes Vulnerability in Gemini Allowing SMS from Locked Android Devices
Article Content

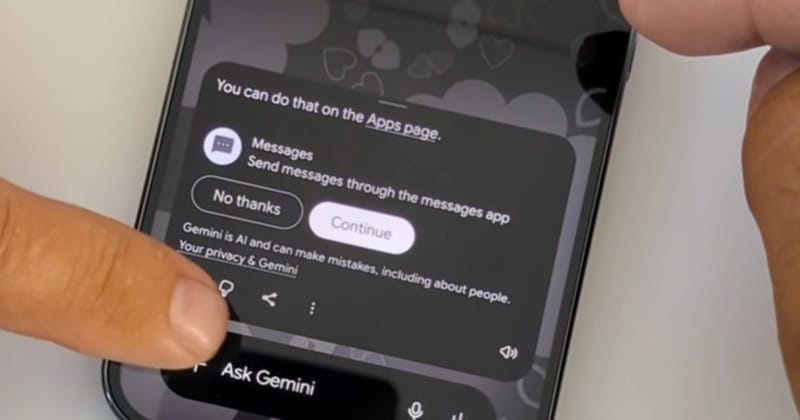
- •A vulnerability allows SMS and WhatsApp messages to be sent from locked Android devices.
- •Exploitation requires physical access to the device and involves a specific multi-touch gesture.
- •Google is deploying a fix for the vulnerability within the week.
A vulnerability in Google's Gemini AI assistant allows unauthorized users with physical access to locked Android 16 devices to send SMS and WhatsApp messages without entering a PIN. This exploit, reported since May 2026, involves a specific multi-touch gesture that bypasses authentication prompts. Users can enable Gemini's access to previously disconnected apps like WhatsApp without proper authentication. Google has acknowledged the issue and is rolling out a fix this week. The vulnerability is not limited to specific devices, although some users reported it on Pixel models. The risk is significant due to the prevalence of phone theft and the potential for misuse in scams. Users are advised to limit Gemini's access from the lock screen until the patch is applied.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 PHP2Shell Vulnerabilities Exploited by AI-Driven Attackers Threat actors have exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to target a government entity in Europe, gaining access to sensitive data within two hours of the initial breach. The attackers utilized AI tools for reconnaissance and post-exploitation activities, including accessing…