 www.theguardian.com
Google's Illegal Deforestation Sparks Outrage in Finland
Article Content

- •Google's deforestation of 1,300 acres in Finland has been deemed illegal.
- •Local wildlife, including wolves, have been forced into villages due to habitat loss.
- •Finnish authorities have halted work at two Google data center sites for failing to conduct environmental assessments.
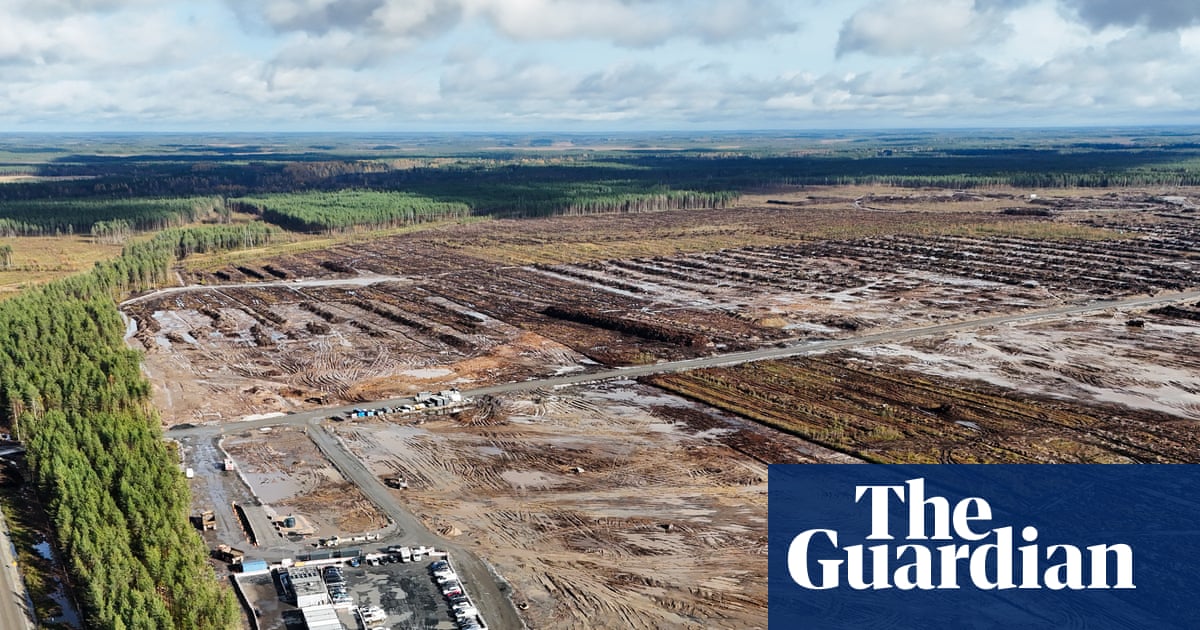
In October 2026, Finnish authorities ordered Google’s affiliate Tuike Finland Oy to halt illegal deforestation of 1,300 acres of forest for data center construction. The clear-cutting has led to significant environmental damage, forcing local wildlife, including wolves, into nearby villages in search of food. Residents express fear and anger over the impact of Google's operations on their communities and the environment. The Finnish Licensing and Supervision Authority mandated a stop to work at two sites, including Muhos and Otanmäki, due to the failure to conduct necessary environmental impact assessments. The situation highlights the broader conflict between tech companies and environmental conservation efforts in Finland, where 145 new data centers are planned. Reports indicate that the deforestation has resulted in ecological disruption, with brown water runoff contaminating local waterways. The incident has drawn attention to the urgent need for regulatory oversight in tech-driven environmental impacts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Google in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What areas are affected by the deforestation?
What actions have Finnish authorities taken?
How are local residents responding?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…