 Securityaffairs.Co
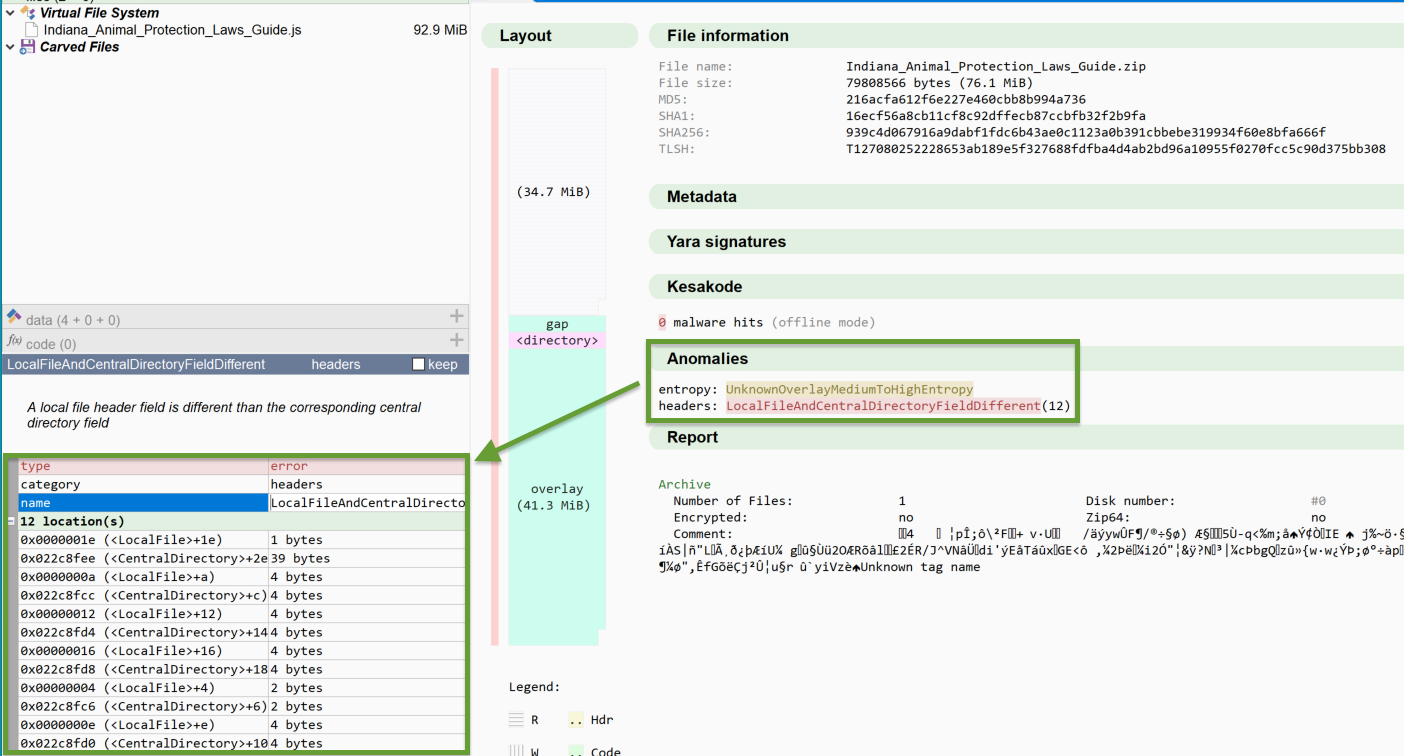
GootLoader Exploits Malformed ZIP Files to Evade Detection
Article Content
Browse articles 
GootLoader malware utilizes malformed ZIP files composed of concatenated archives to bypass security measures. This technique has been linked to ransomware operations, including Vanilla Tempest, and is designed to evade detection by most security tools while being processed correctly by Windows' default unarchiver. Early detection is crucial to mitigate its impact.
Ask AI about this cluster
Answers cite the sources they use
Updated 252d ago How this analysis works
More articles in this cluster (2)
Following this threat?
Track Vanilla Tempest and Gootloader in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
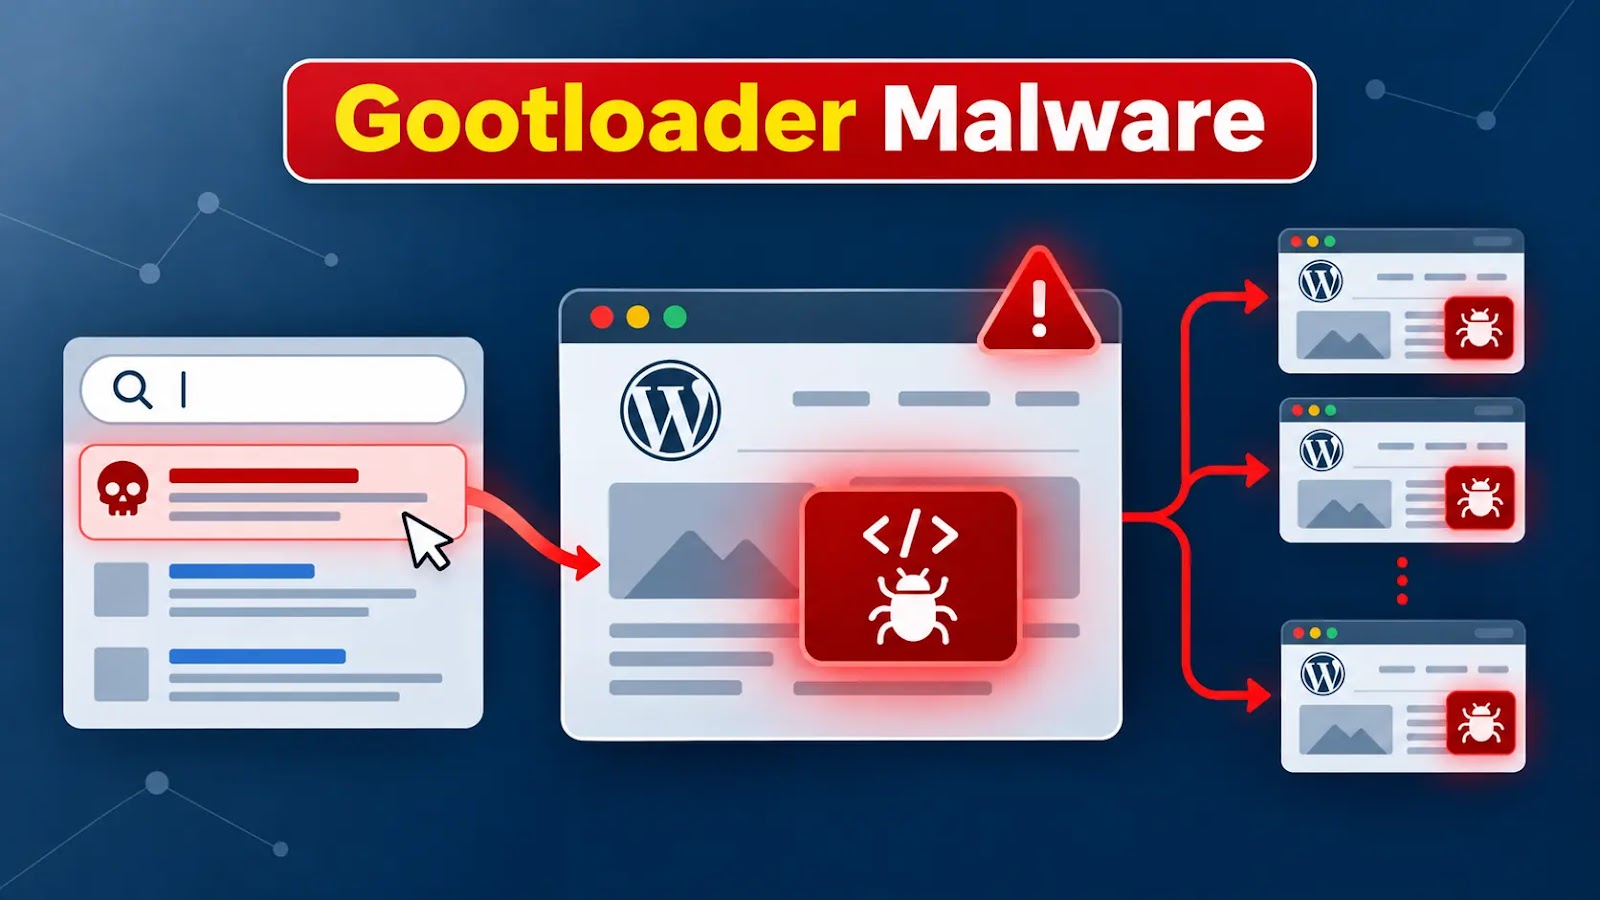 Gootloader Malware Infects 1,000+ WordPress Sites via SEO Poisoning Cybercriminals have compromised over 1,000 WordPress websites to distribute Gootloader malware, targeting legal professionals with manipulated search results. The FBI warns that these attacks exploit SEO poisoning to trick users into downloading malicious JavaScript files disguised as legal documents. The operation…
 Europol Disrupts Major Malware Networks, Seizes 6.4 Million Stolen Credentials In a significant operation, Europol and law enforcement from nine countries dismantled the infrastructure behind three major malware families: Gootloader, CastleRAT, and StealC. This operation, part of Operation Endgame, resulted in the seizure of 235 servers and 257 domains. Authorities identified approximately 6.4…