 Menatech
Group-IB Warns of Deepfake Investment Scams Targeting Gulf Investors
Article Content

- •Group-IB warns of deepfake scams targeting Gulf investors via WhatsApp.
- •Victims face significant losses from manipulated stock purchases and fake crypto platforms.
- •Group-IB recommends verifying investment leads through official regulatory channels.
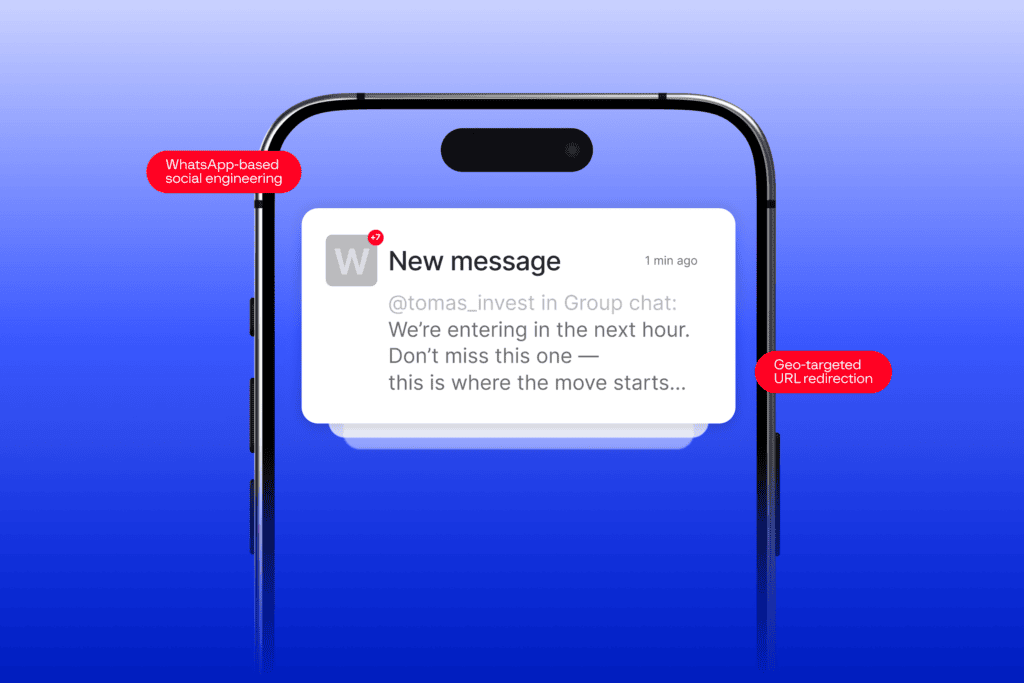
Group-IB has issued a warning to retail investors and financial institutions in the Gulf Cooperation Council (GCC) about two fraudulent investment schemes utilizing deepfake technology and private messaging apps. The first scheme involves victims being recruited into WhatsApp groups and manipulated into purchasing small-cap stocks, leading to significant financial losses. In one instance, a stock price surged by 12.4% before plummeting, resulting in a 42.4% loss for investors. The second scheme, linked to an entity named CoinLure, operates over 200 fake cryptocurrency platforms that promise fabricated returns and demand additional fees for withdrawals. These scams exploit the high adoption rates of cryptocurrency and the prevalent use of WhatsApp for financial communications in the region. Group-IB advises caution and recommends that all investment leads from messaging platforms be independently verified with regulatory authorities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…