 bitquery.io
Hacker Drains $1.47M from b14g Bitcoin Staking Platform
Article Content

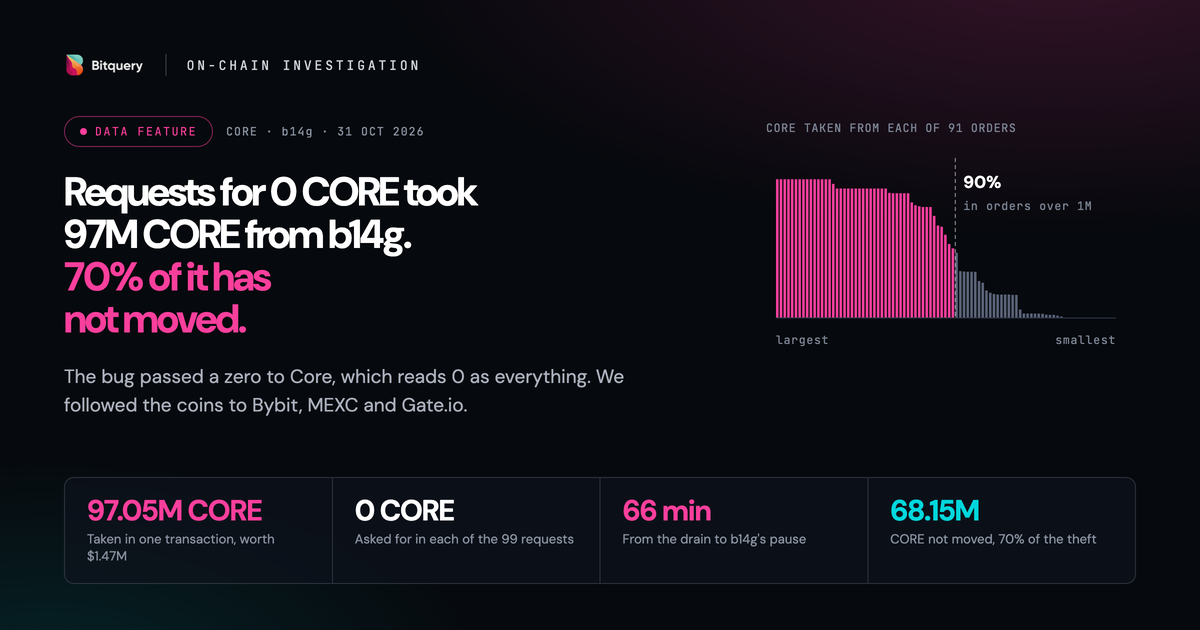
- •b14g lost approximately 97 million CORE tokens due to a contract logic flaw.
- •The attacker exploited zero-value withdrawal requests, draining funds from 91 staking positions.
- •b14g paused affected contracts and is coordinating recovery efforts with exchanges.
On October 31, 2026, the b14g Bitcoin staking platform was exploited, resulting in the loss of approximately 97 million CORE tokens, valued at $1.47 million. The attacker executed 99 zero-value withdrawal requests, which were incorrectly processed by the platform's contract logic, allowing the full balance of 91 staking positions to be drained in a single transaction. The exploit was confirmed by blockchain analytics firm Bitquery, which noted that the vulnerability had existed for 17 months. Following the attack, b14g paused the affected contracts and is working with security partners to recover the funds. As of October 31, 68 million CORE tokens remained in the attacker's wallets, while b14g's exchange partners froze 9 million CORE. The breach did not affect Bitcoin deposits, which remain secure on the BTC blockchain.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
How much was stolen?
What caused the exploit?
What is b14g doing to recover the funds?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…