 www.cyberagentur.de
HAL2027 Competition Launched for Cyber-Secure Administrative Workplaces
Article Content

- •HAL2027 competition launched to enhance cybersecurity in public administration.
- •Focus on creating integrated, cyber-secure workplaces for the future.
- •Open to diverse participants, including researchers and startups.
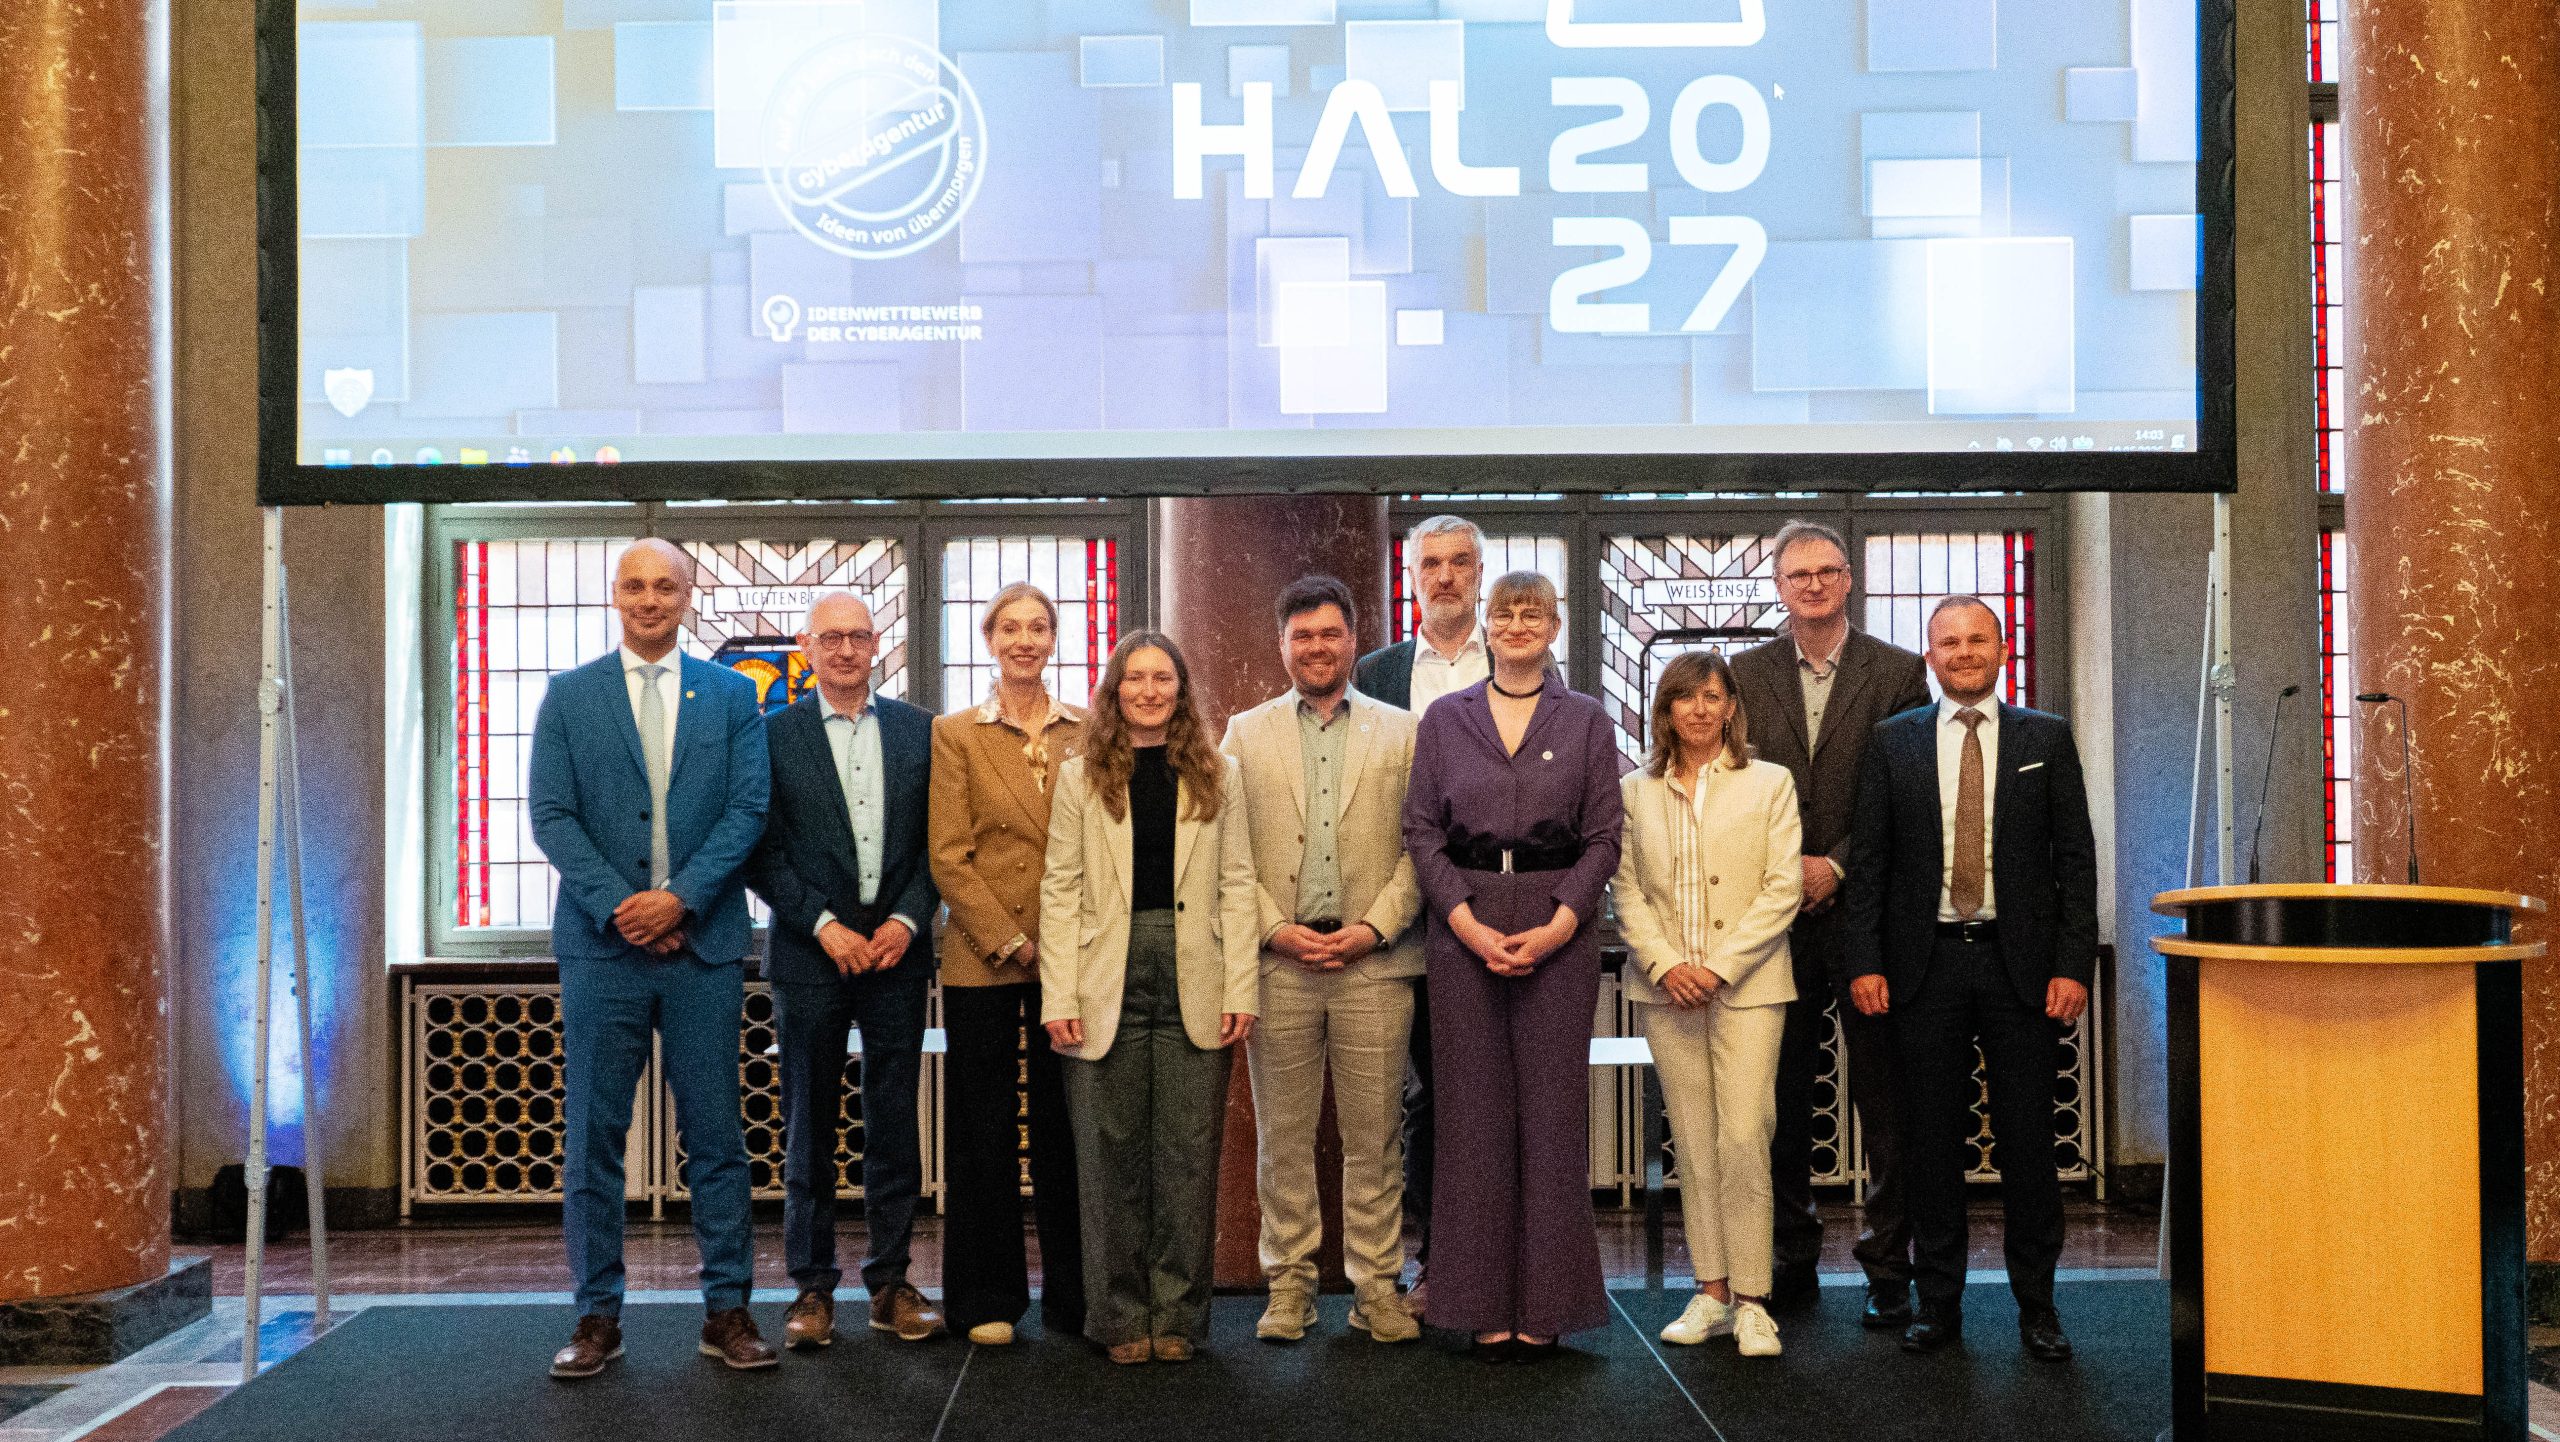
On May 19, 2026, the Cyberagentur launched the HAL2027 ideas competition in Berlin, seeking innovative concepts for a cyber-secure administrative workplace of the future. This initiative builds on the previous HAL2025 competition, which focused on autonomous intelligent systems. The competition invites participation from researchers, students, startups, and companies to address the growing security needs of digital administrative environments. Bettina Bubnys, Commercial Director of the Cyberagentur, emphasized the importance of integrating security into the digital transformation of public administration. The initiative aims to create work environments that are not only efficient but also resilient and sovereign. The HAL2027 competition highlights the increasing relevance of cybersecurity in public administration as digital processes evolve. The event was marked by speeches from key officials, including Thilo Cablitz from the Berlin Interior Administration, who stressed the link between innovation, governmental capability, and digital security.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…