 Gbhackers
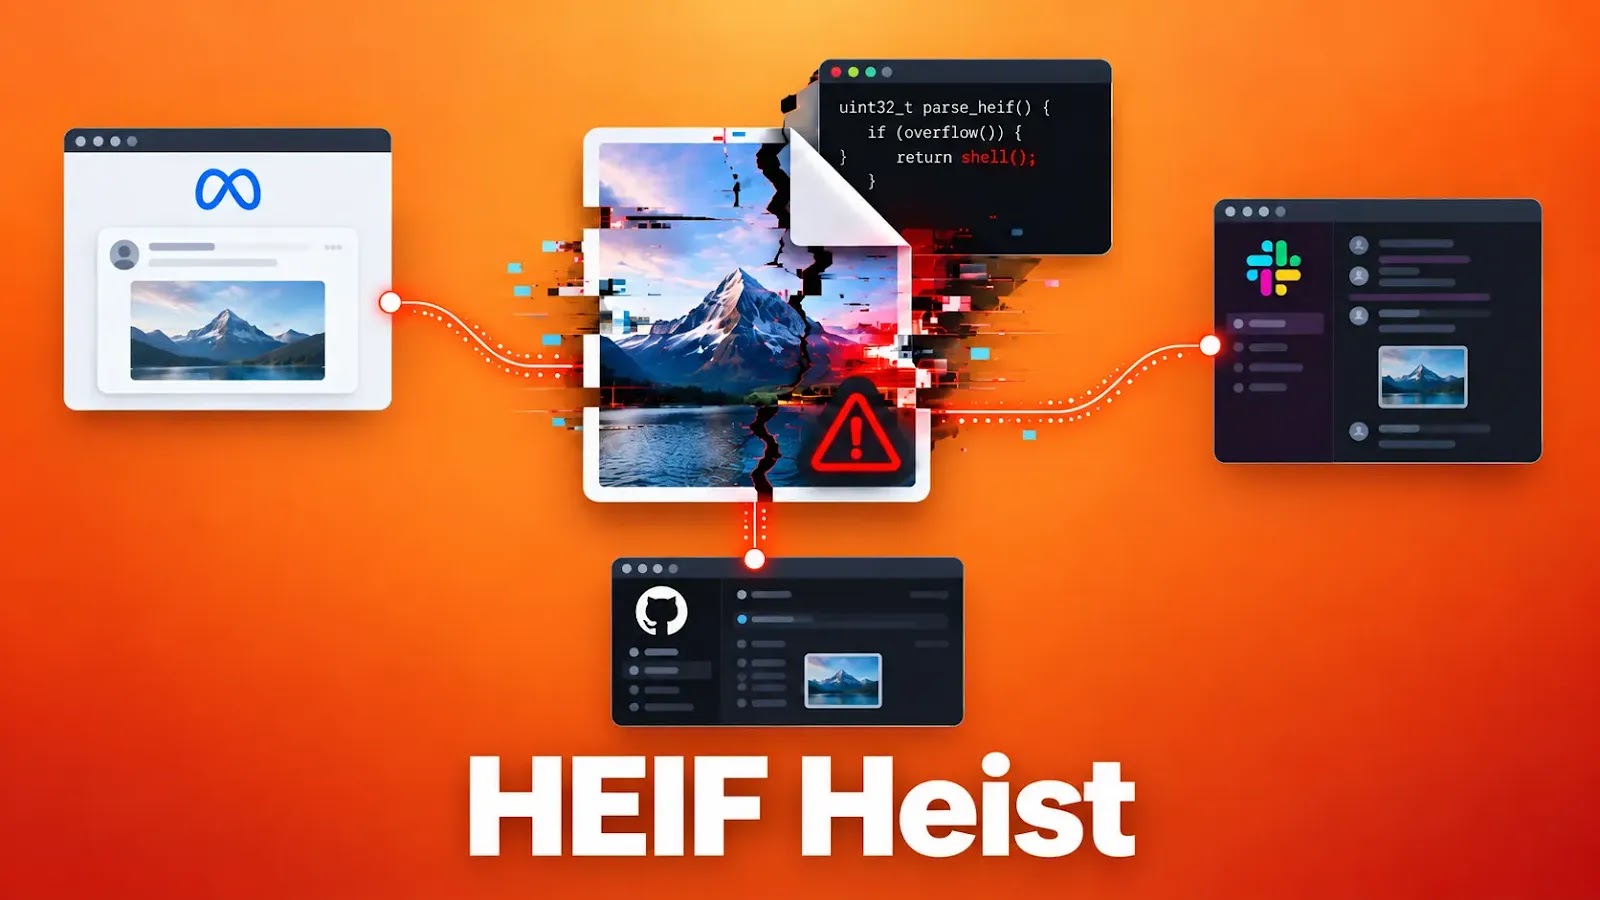
HEIF Heist: Remote Code Execution Vulnerabilities Exploited in Major Platforms
Article Content

- •HEIF Heist exploits vulnerabilities in image parsers libheif and libde265.
- •Major platforms like Meta, Slack, and GitHub Enterprise are affected.
- •CVE-2026-19118 allows authenticated remote code execution in GitHub Enterprise.
The HEIF Heist refers to a class of vulnerabilities affecting image-processing libraries like libheif and libde265, allowing attackers to execute remote code through malicious HEIF, HEIC, or AVIF files. Disclosed by Hacktron, this issue impacts major platforms including Meta, Slack, and GitHub Enterprise, highlighting a significant supply chain risk in applications that rely on native image decoders. The vulnerabilities can lead to heap disclosure, sensitive data exposure, and account compromise. Notable CVEs include CVE-2026-19118, which allows authenticated RCE in GitHub Enterprise, and CVE-2026-84383, a critical heap-buffer overflow in libheif. Hacktron's research began with an investigation into OpenAI's Discourse platform, revealing a chain of vulnerabilities that could compromise user accounts. The attack surface is extensive, as many applications unknowingly utilize these vulnerable libraries through higher-level frameworks. Current recommendations include upgrading to the latest versions of affected libraries to mitigate risks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Payload, Rapuncel Infostealer and Meta in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Payload Ransomware Targets German State Development Company SALEG The Payload ransomware group has listed SALEG (Sachsen-Anhaltische Landesentwicklungsgesellschaft mbH) on its leak site, claiming to have stolen data from the state-owned land development company in Saxony-Anhalt, Germany. The extent of the data claimed to be taken has not been independently verified, and SALEG has…
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…