 Dvidshub
High-Fidelity Cyber Training Conducted by 33rd RGS and 392nd CTS
Article Content

- •Magenta Stars exercise tested 69th Cyberspace Squadron's defensive capabilities.
- •The training involved realistic threat scenarios and simulated adversarial intrusions.
- •Collaboration with aggressors allowed operators to enhance detection and remediation skills.
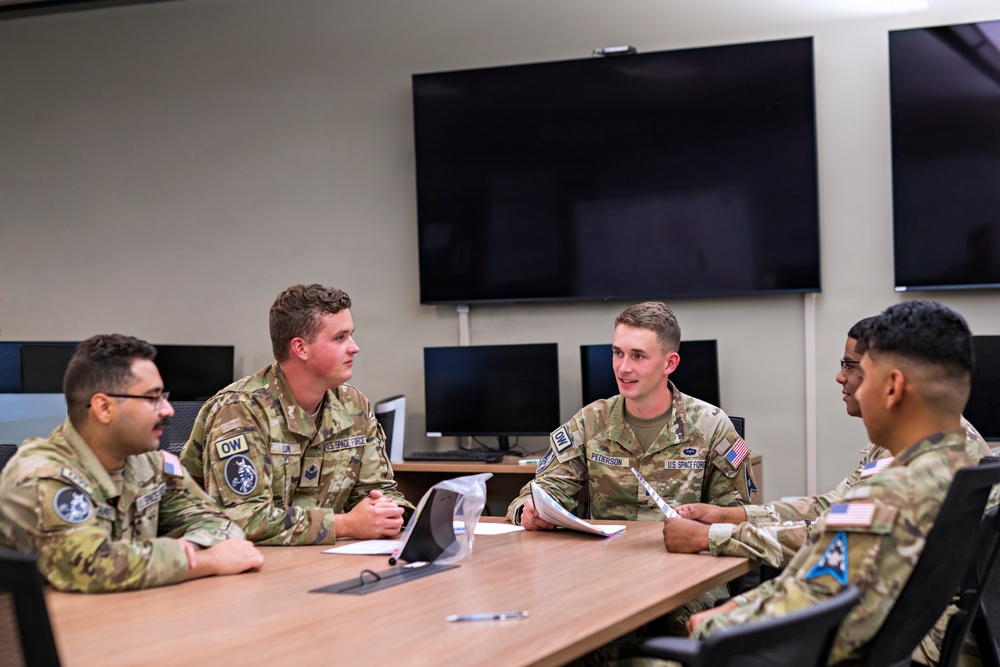
In late September 2026, the 33rd Range and Aggressor Squadron, in partnership with the 392nd Combat Training Squadron, conducted the Magenta Stars exercise. This event involved 69th Cyberspace Squadron operators who faced high-fidelity threat scenarios designed to test their ability to protect operational space networks. The exercise simulated adversarial intrusions over three days, with two defensive cyber crews responding to persistent threats. The training aimed to enhance operational readiness and involved realistic tactics based on real-world advanced persistent threats. The exercise provided operators with opportunities to improve their threat detection and remediation skills through collaboration with aggressors. The event was part of the Space Force Generation readiness validation cycle for the 69th CYS, emphasizing the importance of adaptability in rapidly evolving operational demands.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What was the purpose of the Magenta Stars exercise?
Who participated in the exercise?
What types of threats were simulated during the exercise?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…