 www.cnnbrasil.com.br
Investigation Launched into AI-Generated Pornography in Brazil
Article Content

- •Two ex-employees are investigated for creating deepfake pornography of colleagues.
- •The operation was executed by the PCDF on July 10, 2026, following multiple complaints.
- •The crime carries a potential prison sentence of four to ten years.
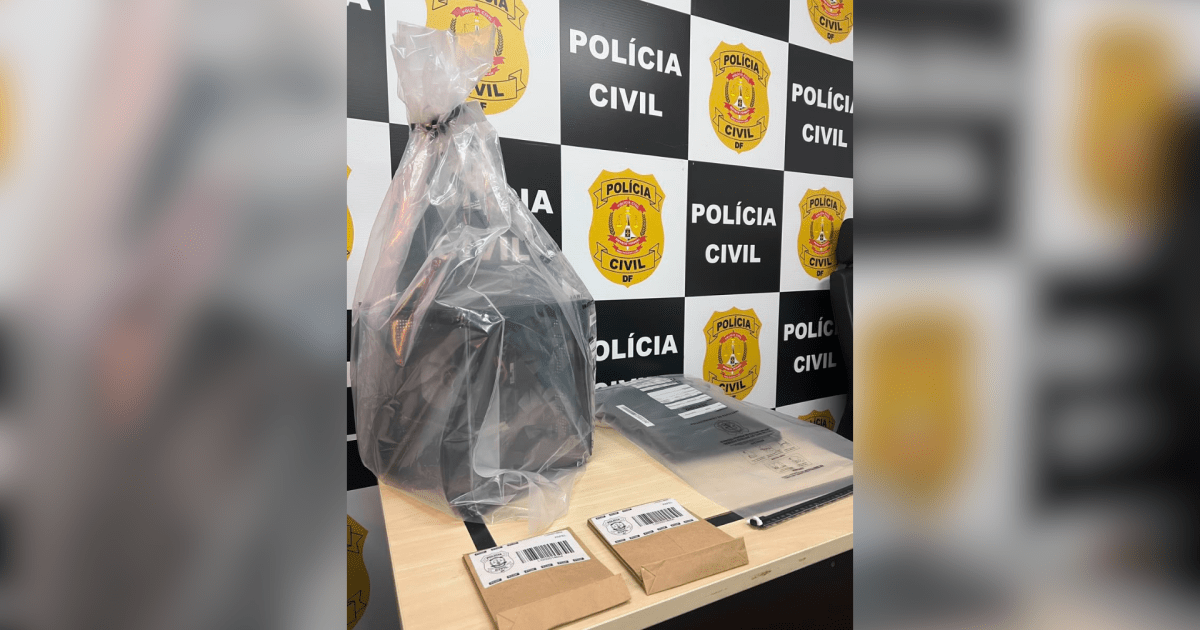
Two ex-employees of a private company in the Federal District of Brazil are under investigation for creating and distributing fake pornographic content using deepfake technology. The Police Civil of the Federal District (PCDF) conducted an operation on July 10, 2026, to execute search and seizure warrants against the suspects. The investigation began following reports that images of female employees were manipulated to produce illicit videos and photographs. These materials were shared via corporate emails and posted on adult content platforms, leading to significant distress for the victims. The PCDF has indicated that this crime is severe, with potential penalties ranging from four to ten years of imprisonment. Evidence gathered from company-provided hard drives and data analysis has pointed to the involvement of the two former employees. The investigation is ongoing as authorities seek to clarify all aspects of the case.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and… Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…