 www.honeywellaerospace.com
Honeywell Aerospace Secures $1.5 Billion C-UAS Contract
Article Content
Browse articles 
- •Honeywell Aerospace awarded a $1.5 billion C-UAS contract by DHS.
- •The contract enables the delivery of advanced technologies for drone threat mitigation.
- •Collaboration with Odys Aviation enhances Honeywell's airborne defense capabilities.
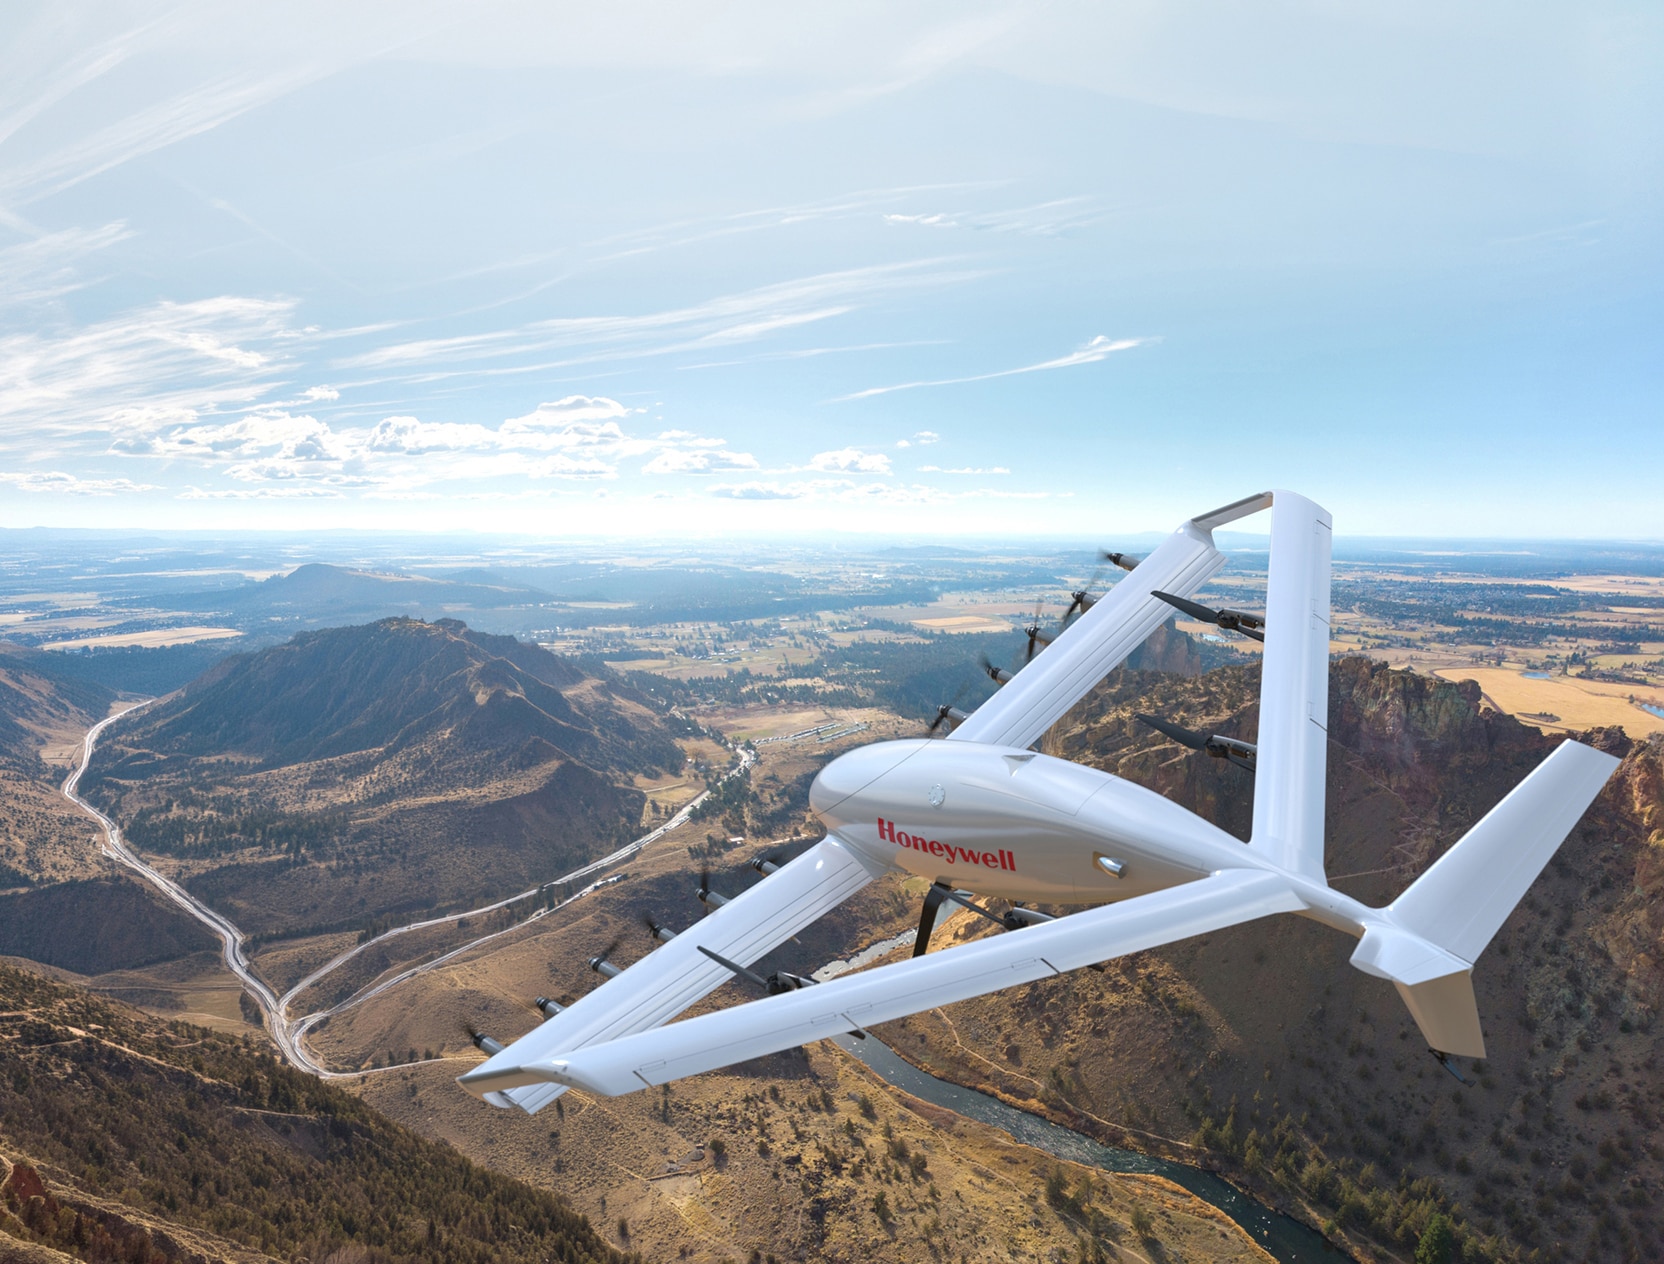
Honeywell Aerospace's subsidiary, EMS Defense Technologies, was awarded a contract under the U.S. Department of Homeland Security’s Counter-Unmanned Aircraft Systems (C-UAS) program, with a total ceiling value of $1.5 billion. This contract allows Honeywell to deliver advanced technologies aimed at countering threats from unmanned aerial systems. The award highlights Honeywell's commitment to enhancing national security and protecting critical infrastructure. The technologies will support government customers in addressing emerging security challenges. The collaboration builds on previous developments with Odys Aviation to create an airborne defense solution against drone threats.
Ask AI about this cluster
Answers cite the sources they use
Updated just now How this analysis works
Timeline
2026-03-31
Collaboration with Odys Aviation announced
Honeywell Aerospace and Odys Aviation announced a partnership to develop a C-UAS defense solution using the Laila UAV.
Honeywell Aerospace2026-10-12
Honeywell awarded C-UAS contract
Honeywell Aerospace's EMS Defense Technologies was selected for the DHS C-UAS program, valued at $1.5 billion.
Honeywell AerospaceMore articles in this cluster (2)
Common questions
What does the C-UAS contract entail?
The contract allows Honeywell to provide advanced hardware, software, and services to counter drone threats.
Who are the key partners in this initiative?
Honeywell Aerospace is collaborating with Odys Aviation to develop airborne counter-UAS solutions.
What is the significance of this contract?
The contract is valued at $1.5 billion and aims to enhance national security and critical infrastructure protection.
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…