 Itsecurityguru
Huntress Analyzes Akira Ransomware Attack After EDR Failure
Article Content

- •Huntress reconstructed an Akira ransomware attack without EDR telemetry.
- •The attack involved RDP access from an external workstation and the use of GOST for tunneling.
- •Volume shadow copies were deleted to prevent recovery, a common tactic used by Akira.
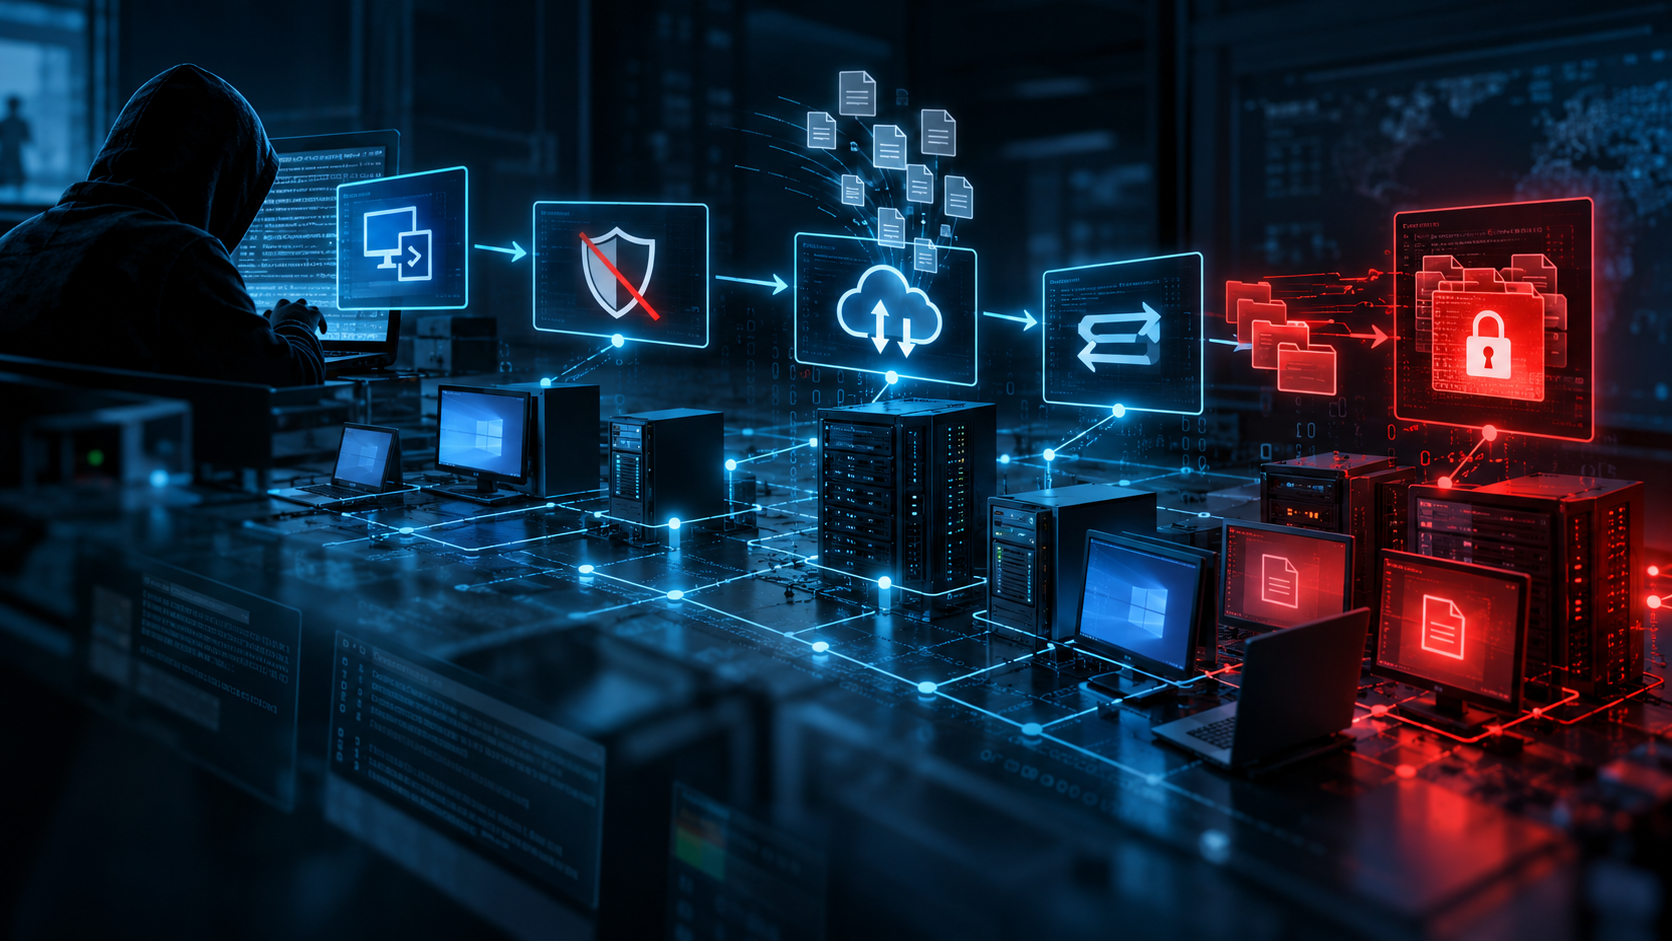
In September 2026, Huntress deployed its agent at an organization already compromised by Akira ransomware. The post-compromise installation meant crucial EDR telemetry was missing, hindering initial access insights. Researchers reconstructed the attack using Windows Event Logs, Registry artifacts, and Akira log files. The attack began with the execution of svchost.exe from a suspicious directory, followed by unauthorized access via RDP from an external workstation. The attacker accessed the BitDefender console and executed commands to delete volume shadow copies, a typical Akira tactic. The analysis revealed the use of GOST, an open-source tunneling tool, and Rclone for data exfiltration. The ransomware subsequently encrypted the organization's file shares. Huntress emphasized the importance of maintaining accurate system inventories and reducing attack surfaces.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Akira in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What systems were affected?
How did the attacker gain access?
What should organizations do to prevent similar attacks?
Continue Reading
 Chinese Smishing Gang Targets Ireland and Four Other EU Countries Ireland is identified as one of five EU countries targeted by the Chinese text-scam group known as Smishing Triad, as reported by the EU cyber security agency Enisa. This group conducts large-scale smishing operations, which involve sending fraudulent text messages that impersonate legitimate organizations to steal…
 Network Segmentation Failures Heighten Cyberattack Risks in 2026 Forescout's analysis of 47,700 network segments across 209 organizations reveals significant network segmentation failures, particularly involving IT, OT, IoT, and IoMT devices. The study found that 62% of segments contained only one device category, while 29% had two and 9% had three or more. Notably, only 13% of…