 News.Sbs.Co.Kr
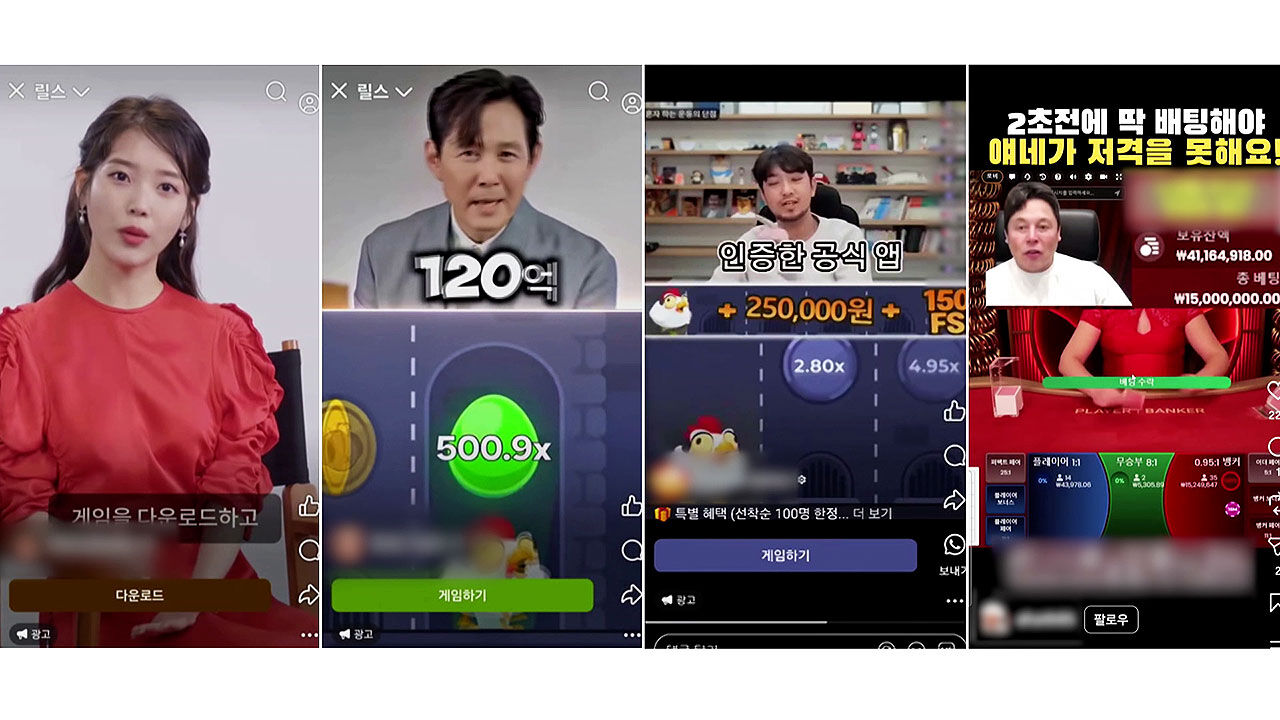
Illegal Deepfake Ads Exploit Celebrity Identities, Enforcement Lags
Article Content

- •Illegal deepfake ads misuse celebrity identities for gambling promotions.
- •No enforcement actions have been taken against deepfake video creators.
- •Proposals to strengthen investigation powers are currently in the National Assembly.
A surge in illegal deepfake gambling ads using celebrities' likenesses has been reported, with no enforcement actions taken against such activities. These ads misappropriate the names, faces, and voices of well-known figures without consent, violating their right of publicity. Victims can file complaints under civil and criminal laws, but the Korean Intellectual Property Office has yet to act against deepfake videos, with previous actions limited to merchandise companies. The lack of cooperation from online platforms hinders administrative investigations, as they often refuse to provide personal information about the posters. Recent proposals in the National Assembly aim to enhance the powers of special judicial police to investigate these cases. Despite the legal framework established in 2022, the current situation remains unaddressed, leaving victims vulnerable.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What legal actions can victims take?
Why are there no enforcement actions?
What changes are being proposed?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…