 Bignewsnetwork
India and Estonia Strengthen Cybersecurity Cooperation Amid Growing Bilateral Ties
Article Content

- •India's exports to Estonia increased by nearly 150% in the past year.
- •The India-Estonia Cyber Security Dialogue has held its first meeting, with more discussions planned.
- •Approximately 2,000 Indians live in Estonia, mainly contributing to the IT and digital sectors.
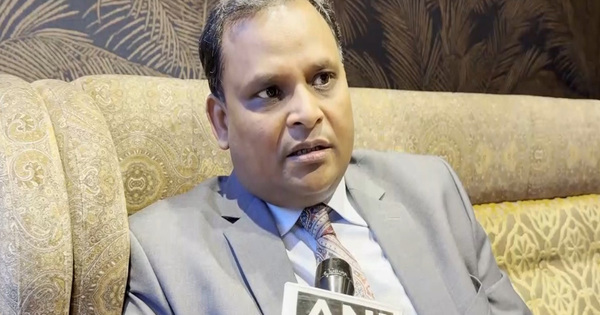
India and Estonia are enhancing their bilateral relations, particularly in trade, digital cooperation, and cybersecurity, as stated by India's Ambassador to Estonia, Ashish Sinha. The ambassador noted a significant increase in India's exports to Estonia, which rose by nearly 150% over the past year. The India-Estonia Cyber Security Dialogue, established last year, has already held its first meeting, with further discussions anticipated soon. Approximately 2,000 Indians reside in Estonia, primarily in IT and digital sectors, contributing to cultural and economic exchanges. The ambassador emphasized the importance of collaboration in technology ecosystems, with India offering strengths in Digital Public Infrastructure and Estonia specializing in digital public services. The potential impact of the India-EU Free Trade Agreement was also discussed, highlighting opportunities for both nations. Estonia's reliance on external markets for its agricultural products underscores the importance of this growing partnership.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…