 Aninews.In
India and Netherlands Establish Strategic Partnership Focused on Cybersecurity and Defence
Article Content

- •India and the Netherlands have elevated their relationship to a Strategic Partnership.
- •The partnership will focus on cybersecurity, defence, and critical technologies like semiconductors.
- •Both nations agreed to enhance cooperation in counterterrorism and maritime security.
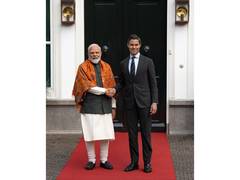
On May 17, 2026, India and the Netherlands announced a Strategic Partnership aimed at enhancing cooperation in various sectors, including cybersecurity, defence, and technology. Prime Ministers Narendra Modi and Rob Jetten adopted a five-year roadmap that includes joint initiatives in maritime security and counterterrorism. The partnership emphasizes collaboration in critical technologies such as semiconductors and artificial intelligence, alongside a commitment to counter cyber threats through capacity building and knowledge exchange. Both nations aim to strengthen bilateral cyber dialogue engagements and develop a Defence Industrial Roadmap for joint production of defence systems. The roadmap also includes measures for enhancing maritime cooperation and sharing best practices in cybersecurity. This strategic alliance reflects the growing geopolitical dynamics and mutual interests in the Indo-Pacific region.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track Education in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…