 defencesecurityasia.com
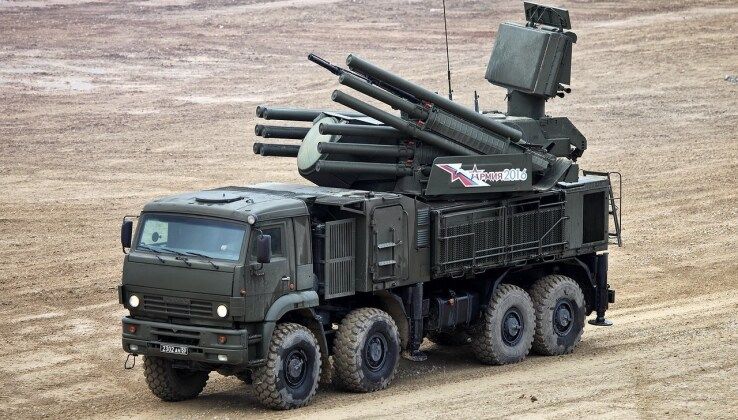
India Considers Purchase of Russian Pantsir Systems Amid Drone Defense Concerns
Article Content

- •India is considering acquiring 13 Pantsir air defense systems from Russia.
- •The Pantsir systems are intended to protect India's S-400 units against drone attacks.
- •The effectiveness of Pantsir systems has been criticized due to poor performance in Ukraine.
India is reportedly evaluating the acquisition of 13 Russian Pantsir air defense systems to enhance the protection of its S-400 units against drone threats. The proposed distribution includes 10 systems for the Air Force and three for the Army, focusing on safeguarding critical military infrastructure. Despite this, the Pantsir systems have shown poor performance in Ukraine, often failing to defend themselves against drone attacks. The Indian Ministry of Defence is currently assessing the proposal, with no confirmed contract details or specific variants disclosed. The strategic implications of this acquisition extend beyond mere procurement, as effective defense against cheaper aerial threats is crucial for the operational viability of India's long-range air defense systems. The S-400 program in India currently comprises four operational batteries, with a fifth expected by year-end. The effectiveness of the Pantsir systems in this context remains questionable, given their historical performance issues.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is the purpose of acquiring Pantsir systems?
What are the concerns regarding Pantsir systems?
Is there a confirmed contract for the Pantsir systems?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Record Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a massive security breach resulting in the theft of approximately $6.3 billion across ten blockchains. The attack is attributed to North Korea's TraderTraitor hacking group, which gained access via a compromised DevOps engineer's…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…