 Inp.Polri.Go.Id
Indonesian Police Focus on Digital Space Management to Combat Disinformation
Article Content

- •INP is enhancing strategies to manage public expression and counter disinformation.
- •A humanistic approach prioritizes communication and negotiation during public demonstrations.
- •Collaboration with the Ministry of Communication aims to improve information accuracy.
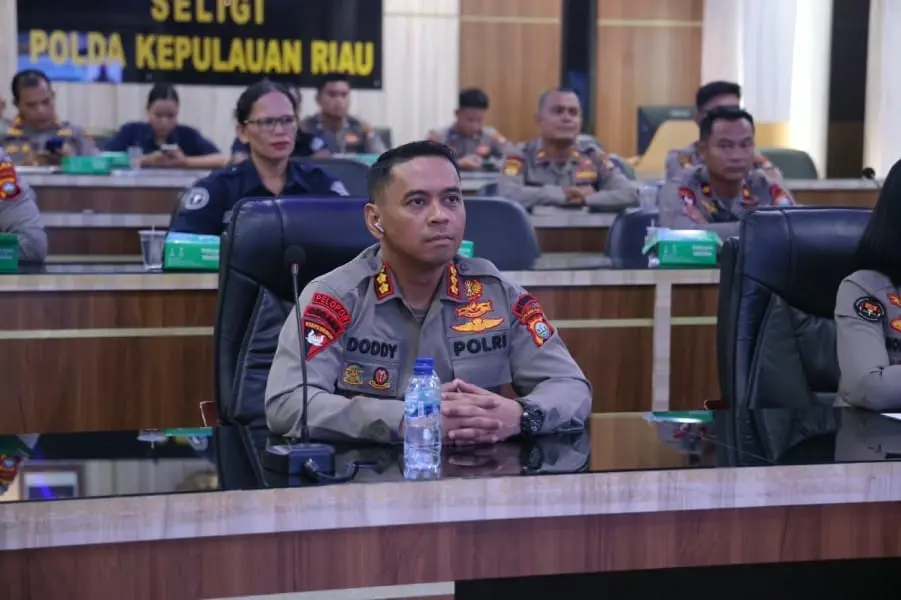
The Indonesian National Police (INP) is enhancing its strategies to manage public expression and prevent disinformation in the digital space. This initiative was discussed during the 3rd Internal Police Strengthening Dialogue held on September 29, 2026. The INP aims to ensure that public aspirations are respected while monitoring for potential disinformation that could incite unrest. Emphasizing a humanistic approach, the police are focusing on communication, negotiation, and early detection to manage public demonstrations effectively. The INP's Public Relations Division highlighted the need for accurate and timely information to maintain public trust and prevent misunderstandings. The police are also collaborating with the Ministry of Communication and Digital to strengthen their communication strategies. The situation during protests is noted to be dynamic, requiring adaptable security measures based on situational analysis.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What strategies is the INP implementing?
How is the INP addressing disinformation?
What is the role of the Ministry of Communication?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…