 Guardian.Ng
INEC Enhances Cybersecurity for 2027 Elections with AI Tools
Article Content

- •INEC partners with Google and Microsoft for enhanced election cybersecurity.
- •AI tools will detect anomalies and combat disinformation during the elections.
- •Electoral officials face immediate dismissal for partisanship or ethical breaches.
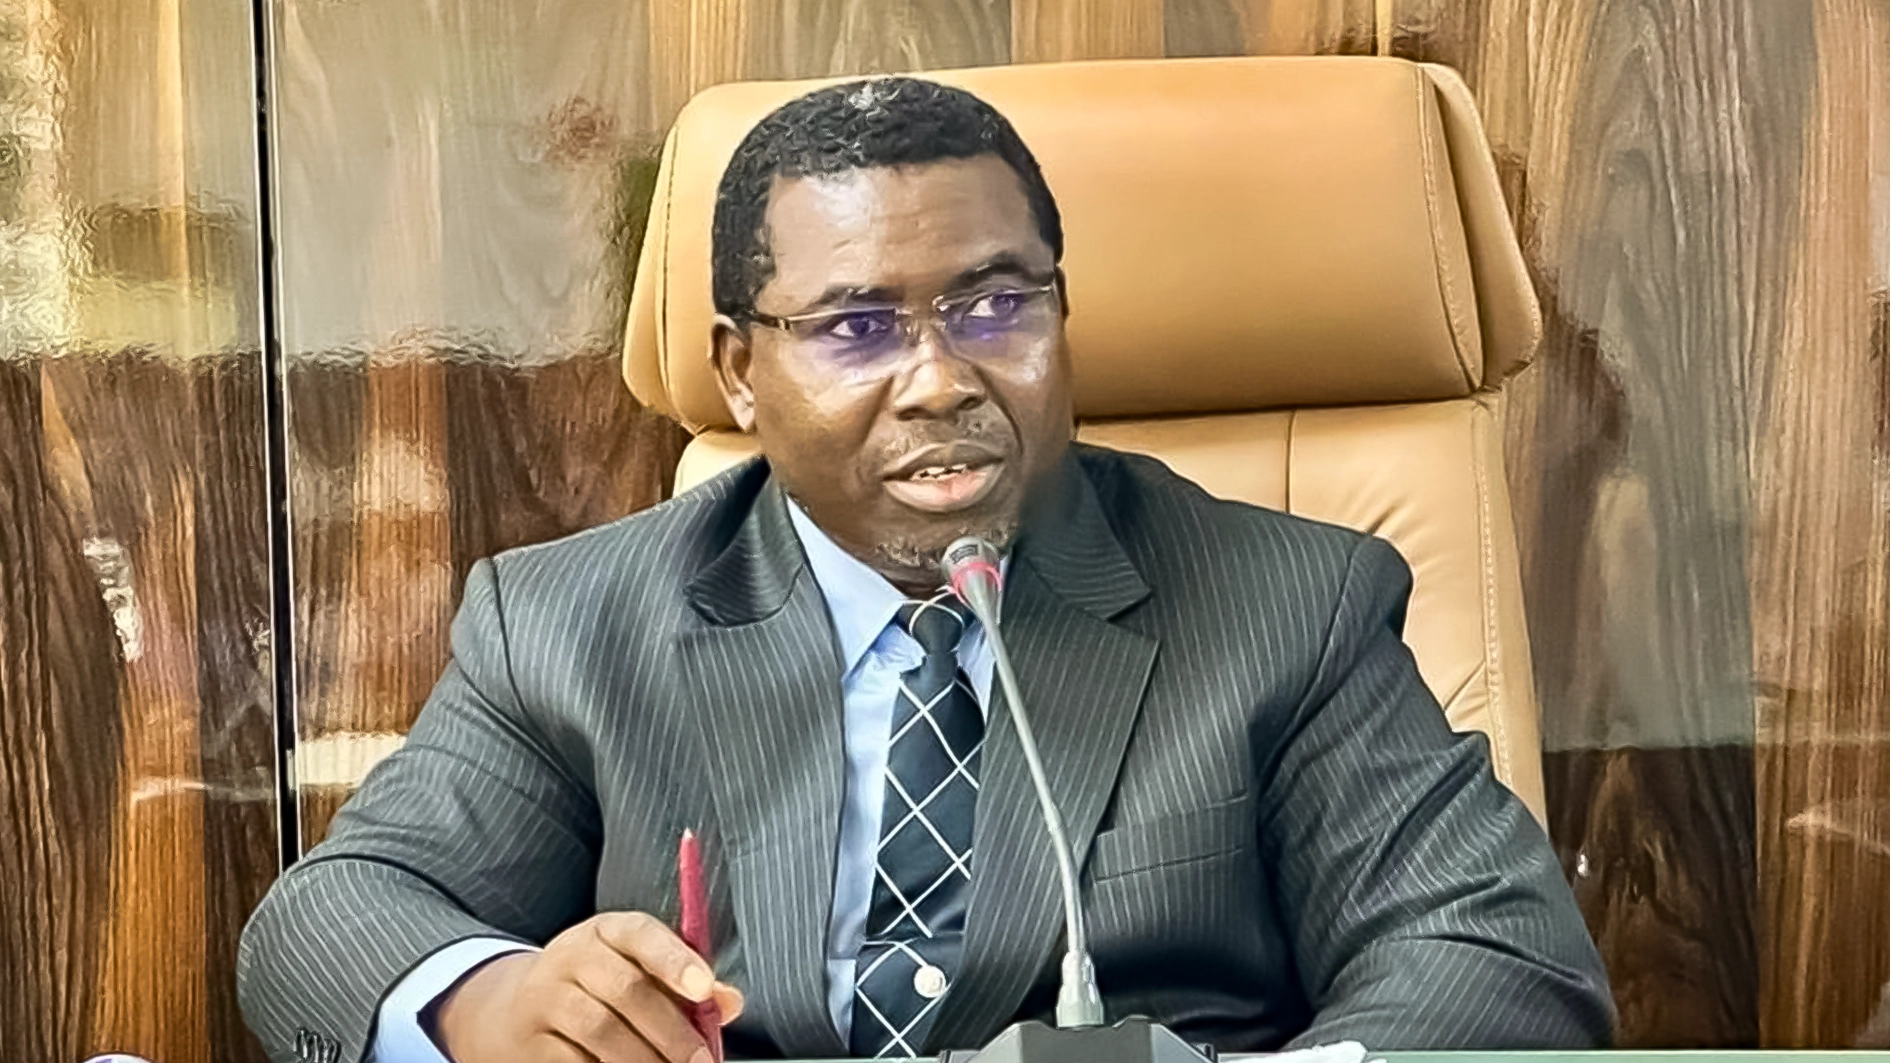
The Independent National Electoral Commission (INEC) of Nigeria is implementing advanced cybersecurity measures in collaboration with Google and Microsoft to safeguard its electoral database ahead of the 2027 elections. INEC Chairman, Prof. Joash Amupitan, announced the deployment of AI data-auditing tools and a dedicated AI division to combat disinformation and detect election anomalies. The commission is also upgrading its Bimodal Voter Accreditation System (BVAS) and conducting nationwide audits to ensure readiness. Amupitan emphasized the importance of public trust in the electoral process, stating that electoral officials must adhere to a binding oath of neutrality. The initiative aims to protect against cyber intrusions, distributed denial-of-service (DDoS) attacks, and unauthorized data injection. INEC is also finalizing an AI governance framework to guide the use of these technologies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What technologies is INEC implementing?
How will INEC ensure election integrity?
What are the consequences for partisan officials?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…