 Theguardian
Iran's Alleged Role in RAF Fairford Incident Raises Security Concerns
Article Content

- •UK PM Burnham confirmed strong indications of Iranian involvement in the RAF Fairford incident.
- •Five British men were arrested and later released on bail, raising concerns about security protocols.
- •The incident is under investigation for potential terrorism or state-sponsored actions.
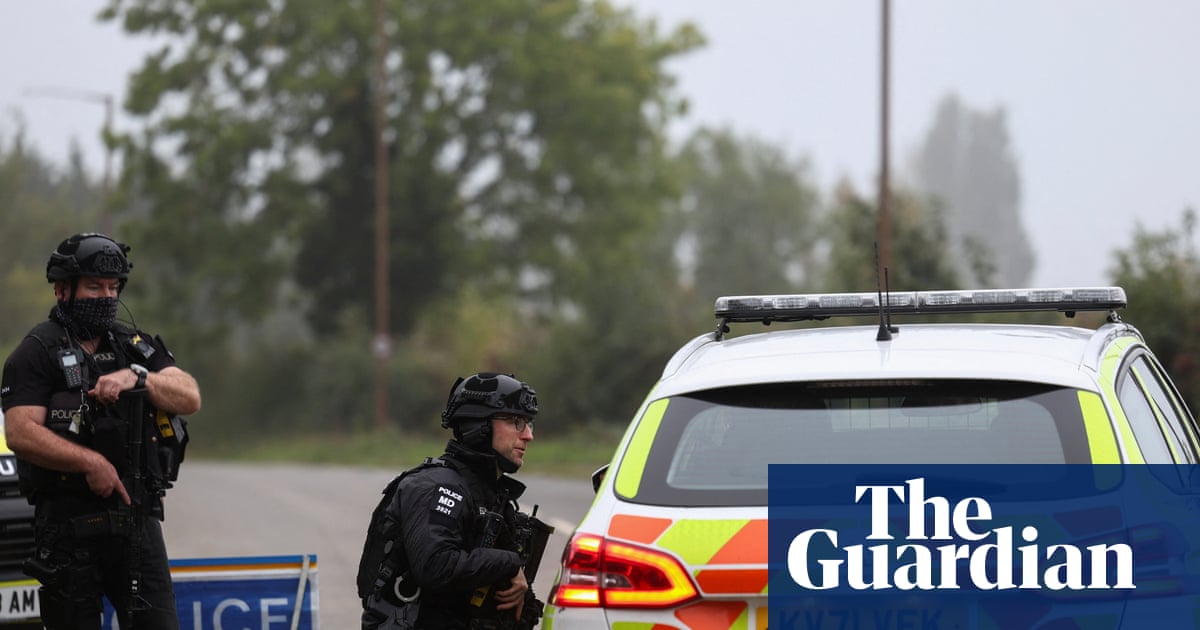
UK Prime Minister Andy Burnham announced strong indications of Iranian involvement in a recent incident at RAF Fairford, where five British men were arrested and later released on bail. The incident, which occurred over the weekend, is being investigated as a potential act of terrorism, state sabotage, or reconnaissance. One suspect reportedly called emergency services before the police were alerted by a local farmer. Burnham emphasized that the investigation remains ongoing and complex, with UK security forces collaborating closely with US counterparts. Tehran has denied any involvement, while US officials, including Secretary of State Marco Rubio, have suggested foreign actor involvement. The suspects, aged 23 to 25, were arrested near the airbase used by US bombers in the Iran conflict, raising geopolitical tensions. The decision to release them on bail has drawn criticism from US officials, including President Trump, who questioned the safety of this decision.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Common questions
What are the implications of Iran's involvement?
What security measures are being taken?
Why were the suspects released on bail?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…