 Calcalistech
Israel's Power Grid Strained by Data Center Demand Amid Nuclear Fusion Exploration
Article Content

- •Data centers may consume 20% of Israel's electricity by 2030, straining the power grid.
- •The Electricity Authority plans new regulations to manage data center connections amid peak demand.
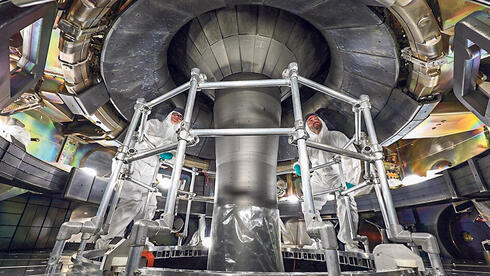
- •Israel's Energy Ministry proposes a NIS 500 million to NIS 1 billion investment in nuclear fusion research.
Israel's Electricity Authority is preparing new regulations for connecting energy-intensive data centers, which could account for 20% of national electricity consumption by 2030. The current electricity generation capacity is approximately 18,800 megawatts, and recent demand peaks have strained the grid. The Electricity Authority halted approvals for new data centers in July 2026 but is expected to publish a regulatory framework to allow construction while managing infrastructure strain. Concurrently, the Israeli Energy Ministry is proposing a long-term investment program in nuclear fusion, with a recommended budget of NIS 500 million to NIS 1 billion over five to seven years, aiming to develop expertise in this emerging energy source. However, the fusion proposal is still a policy recommendation and has not yet received funding. The incoming government will decide on prioritization and funding allocation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Microsoft in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the new regulations for data centers?
How much electricity will data centers consume by 2030?
What is the status of the nuclear fusion proposal?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 KeyDrift Malware Exploits Cisco SD-WAN Flaw CVE-2026-20127 Cisco Talos reported that the advanced persistent threat group UAT-11473 exploited a critical authentication bypass vulnerability (CVE-2026-20127) in Cisco SD-WAN Catalyst Controllers. This flaw, which has a CVSS score of 10.0, allows unauthorized remote access to administrative privileges. The group deployed a custom…