 www.chinadailyhk.com
Jimmy Lai Convicted Under National Security Law in Hong Kong
Article Content

- •Jimmy Lai was sentenced to 20 years for violating the National Security Law.
- •The trial lasted 156 days, involving over 2,220 exhibits and 14 witnesses.
- •Lai's actions were deemed treasonous, aimed at inciting foreign intervention against China.
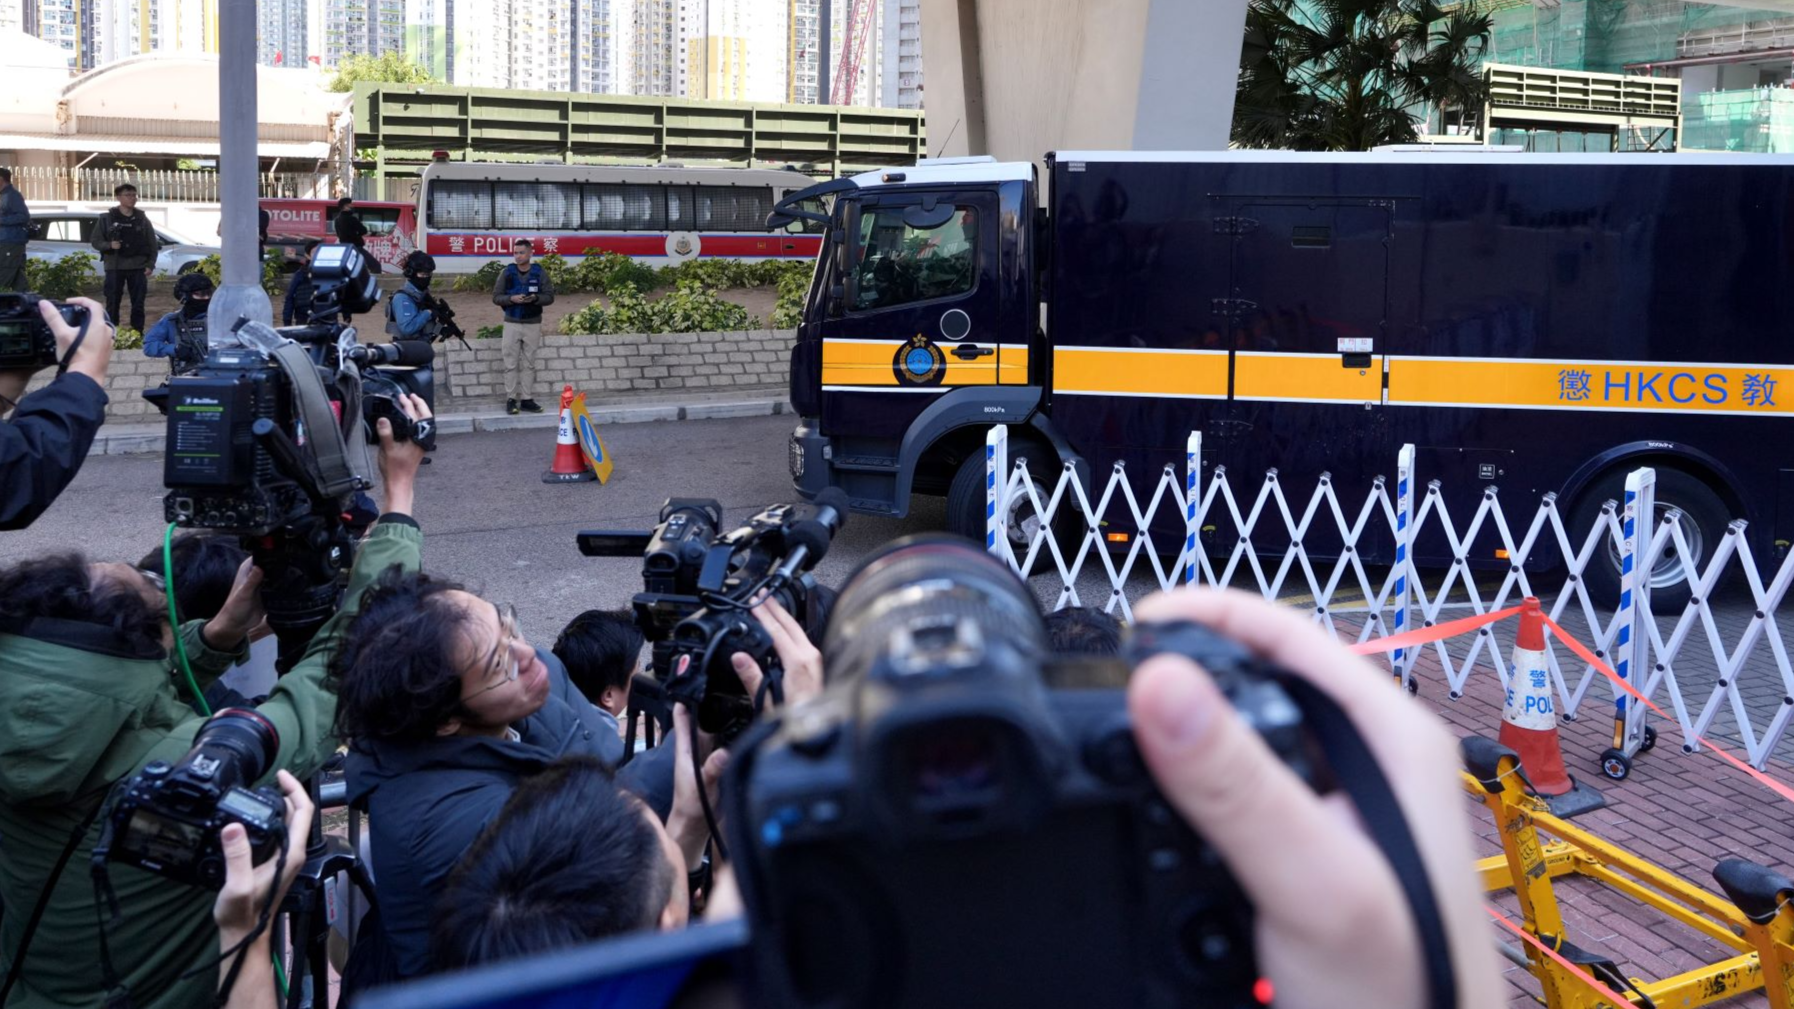
On May 1, 2026, Hong Kong's High Court found Jimmy Lai Chee-ying, founder of Apple Daily, guilty of violating the National Security Law. Lai was convicted on two counts of conspiracy to collude with foreign forces and one count of conspiracy to publish seditious materials. The court sentenced him to 20 years in prison, citing overwhelming evidence of his actions to incite public disaffection and seek foreign sanctions against China. The trial lasted 156 days, with extensive documentation and witness testimonies presented. Three companies associated with Lai were also fined for their involvement in the offenses. The verdict was welcomed by Hong Kong authorities and the central government, who emphasized the importance of upholding national security. Lai's actions were characterized as treasonous, aimed at undermining China's stability. This case marks a significant enforcement of the National Security Law in Hong Kong.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…