 Theguardian
Jingye Steel Seeks Over £1bn Compensation from UK for British Steel Nationalisation
Article Content

- •Jingye Steel is seeking over £1bn in compensation from the UK government.
- •The UK government took control of British Steel in April 2025 for national security reasons.
- •The dispute may escalate to international arbitration under the UK-China investment treaty.
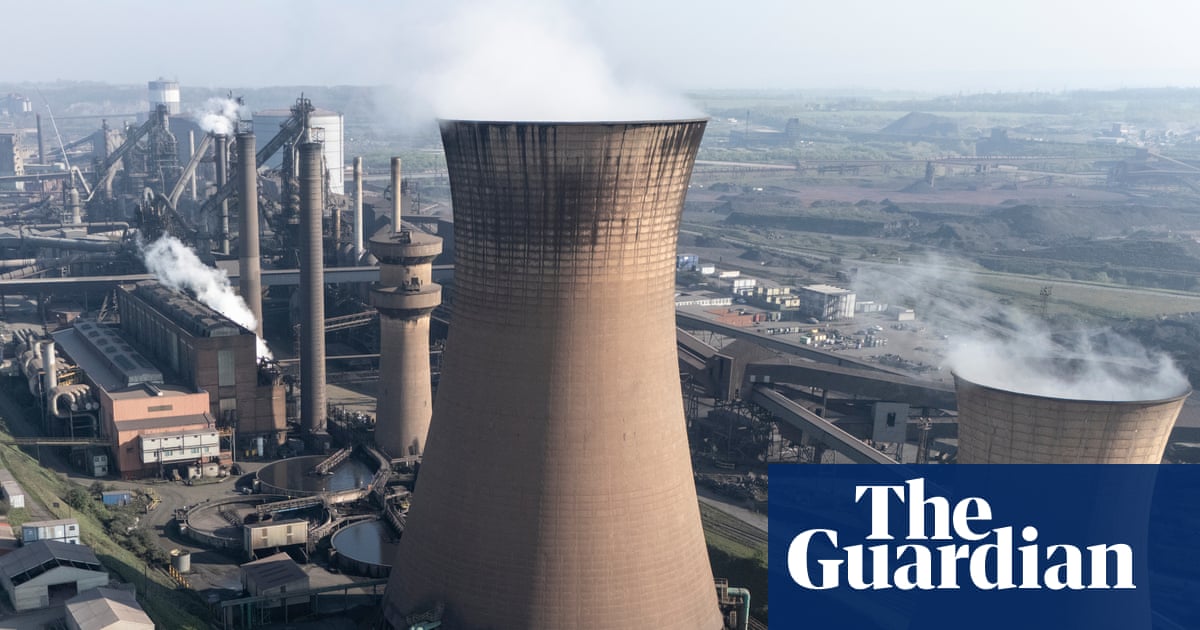
Jingye Steel has initiated a formal process to seek compensation from the UK government exceeding £1bn due to the nationalisation of British Steel. This action follows the UK government's decision to take operational control of British Steel in April 2025, citing national security concerns. Jingye, which acquired British Steel in 2020, claims losses from the investment and is pursuing recovery of debts owed by the company. The dispute is framed under the UK-China bilateral investment treaty, potentially allowing for arbitration if unresolved in six months. The UK government plans to lower tariff-free steel imports, which may enhance British Steel's attractiveness to future investors. The ongoing negotiations could strain UK-China relations as Jingye seeks to safeguard its interests. The situation remains fluid as both parties navigate the complexities of international investment treaties.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…