 Onmanorama
Judges Recuse from 2017 Actress Assault Case Memory Card Access Petition
Article Content

- •Two Kerala High Court judges have recused themselves from the actress assault case petition.
- •The survivor seeks a new investigation into unauthorized access to critical evidence.
- •The case involves serious allegations of digital evidence tampering related to a 2017 assault.
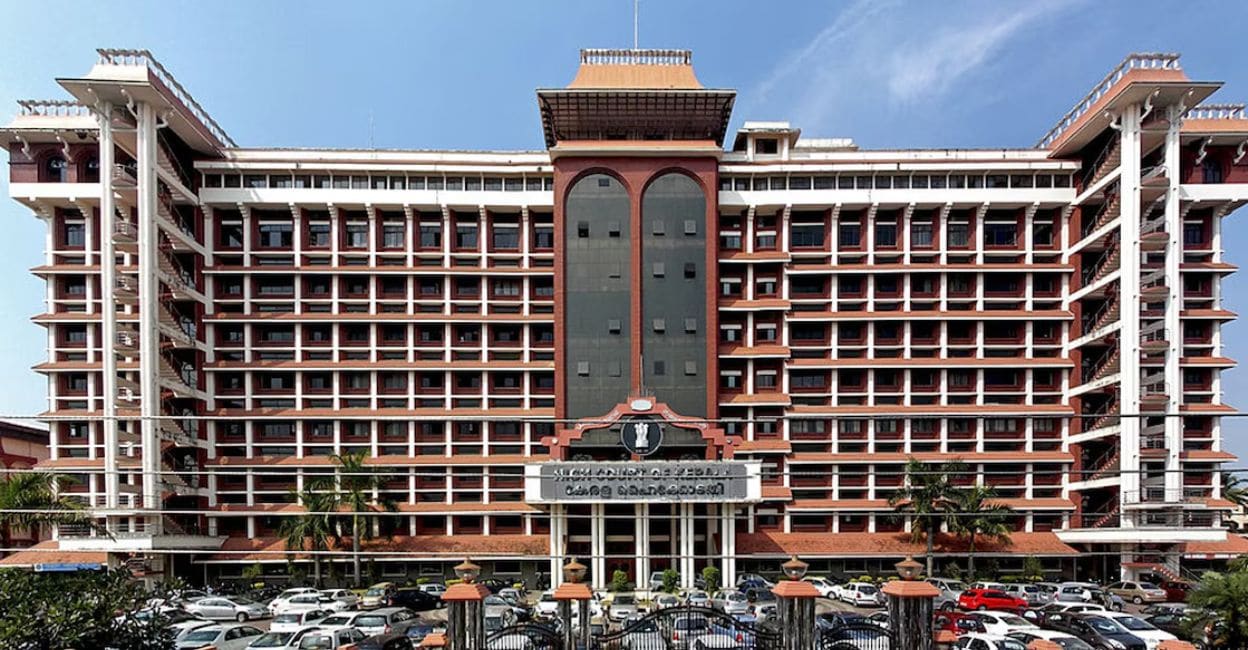
The Kerala High Court is facing complications in the 2017 actress assault case as two judges have recused themselves from hearing a petition filed by the survivor. The petition seeks a comprehensive investigation into unauthorized access to a memory card containing evidence of the assault. Justice Jobin Sebastian recused himself on June 9, 2026, citing prior involvement as Registrar General. Following this, Dr. Justice Kauser Edappagath also recused himself on June 10, 2026. The survivor's petition calls for the formation of a Special Investigation Team (SIT) with cyber forensics expertise to investigate the alleged illegal access. The case involves the abduction and sexual assault of an actress in 2017, with recorded footage that has become a focal point in the ongoing legal proceedings. The trial court previously acquitted one accused while convicting six others. The survivor had previously approached the court in 2022, resulting in a fact-finding inquiry that is now being challenged.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…