 Qazinform
Kazakhstan and Azerbaijan Launch Trans-Caspian Fiber-Optic Line
Article Content

- •Kazakhstan and Azerbaijan launched a 380-kilometer fiber-optic line on October 15, 2026.
- •The project aims to connect Central Asia and China with Europe, enhancing digital infrastructure.
- •The initiative includes an agreement to improve the Trans-Caspian International Transport Route.
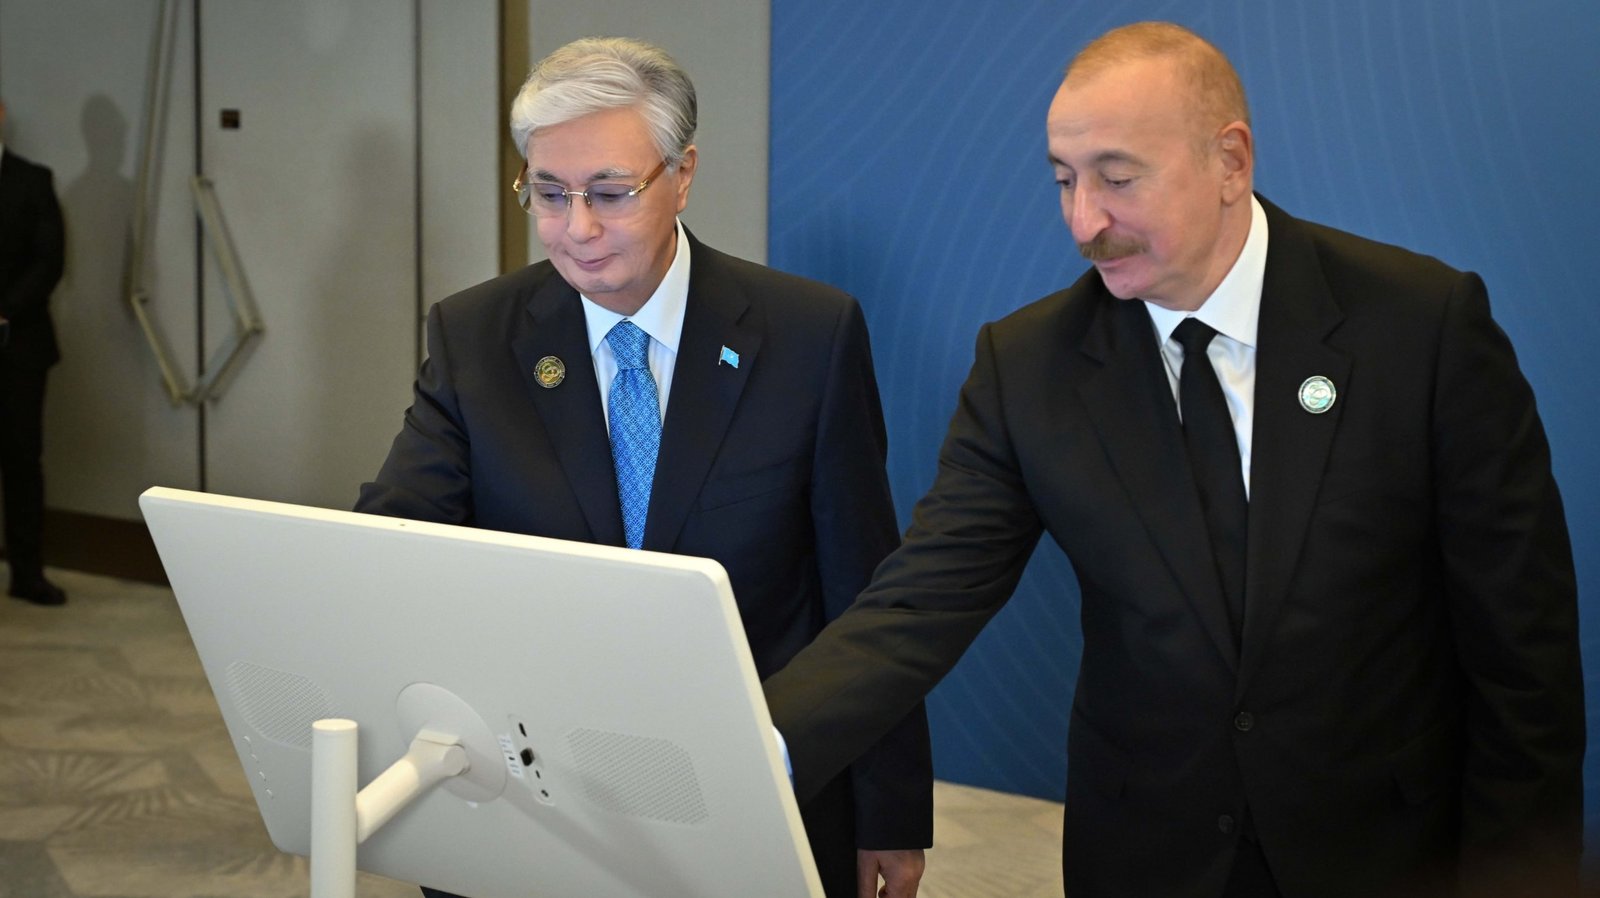
On October 15, 2026, Kazakhstan and Azerbaijan launched a 380-kilometer fiber-optic communication line across the Caspian Sea. This project, implemented by Kazakhtelecom and AzerTelecom, aims to enhance digital connectivity between Central Asia, China, and Europe. President Tokayev emphasized its significance as a new type of corridor for the digital age, while President Aliyev noted its role in strengthening regional cooperation. The fiber-optic line is expected to facilitate the development of cloud services and artificial intelligence infrastructure in Kazakhstan. The launch coincided with an agreement on the Trans-Caspian International Transport Route, focusing on digitalizing transportation and logistics. This initiative is part of broader efforts to improve international data transmission options and attract global technology companies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Common questions
What is the significance of the fiber-optic line?
Who implemented the project?
What does the agreement on the Middle Corridor entail?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…