 kde.org
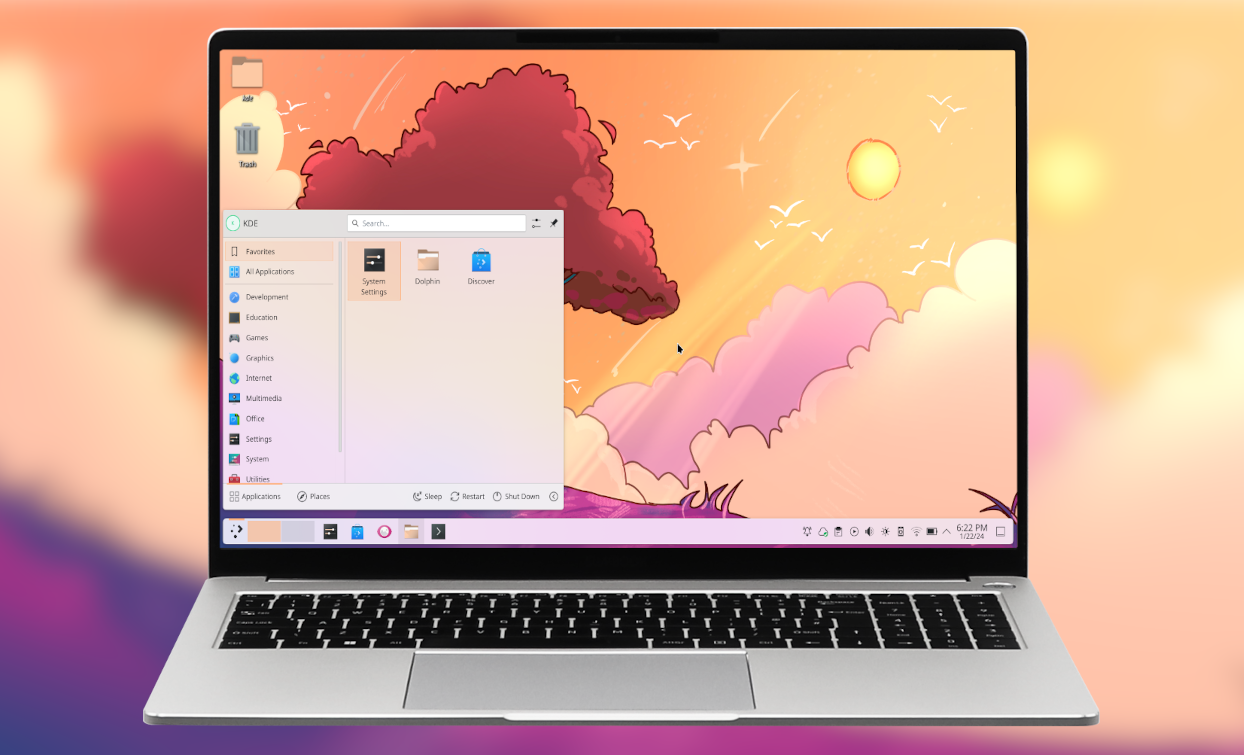
KDE Plasma 6.6.6 Release Signals End of X11 Support
Article Content
Browse articles 
- •KDE Plasma 6.6.6 focuses on bug fixes and is the last in the 6.6 series.
- •Future versions, starting with Plasma 6.8, will be exclusively Wayland, dropping X11 support.
- •No critical vulnerabilities or active exploits reported in this release.
KDE Plasma 6.6.6 was released on July 9, 2026, primarily featuring bug fixes. This version is notable as it marks the last update for the Plasma 6.6 series, with future developments focusing on Plasma 6.7 and 6.8, which will be Wayland-only. The transition to Wayland is significant as it will eliminate support for X11 sessions, affecting users who rely on X11 compatibility. KDE has indicated that the Plasma X11 session will be supported until early 2027, but users are encouraged to transition to Wayland. The release does not contain any vulnerabilities or active exploits, making it a routine update rather than an urgent security concern.
Ask AI about this cluster
Answers cite the sources they use
Updated 10d ago How this analysis works
Timeline
2026-06-15
KDE Plasma 6.7 released
KDE Plasma 6.7 was released, which will be the last version to support X11 sessions.
Theregister2026-07-09
KDE Plasma 6.6.6 released
The release includes numerous bug fixes but no new features, marking the end of the Plasma 6.6 series.
Theregister2026-10-01
KDE Plasma 6.8 scheduled for release
KDE Plasma 6.8 is scheduled for mid-October 2026, coinciding with the 30th anniversary of KDE.
TheregisterMore articles in this cluster (6)
Common questions
What is the significance of Plasma 6.6.6?
It is the last update in the Plasma 6.6 series, focusing solely on bug fixes.
When will support for X11 end?
Support for the Plasma X11 session will continue until early 2027.
What should users do regarding the transition to Wayland?
Users are encouraged to transition to Wayland as future versions will not support X11.
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…