 Securitybrief.Asia
Keeper Security and Williams F1 Launch Identity-First Cybersecurity Campaign
Article Content

- •Keeper Security launches a global campaign promoting identity-first cybersecurity.
- •The campaign targets credential-based threats, emphasizing phishing and social engineering.
- •Williams F1 employs KeeperPAM for managing privileged access and passwords.
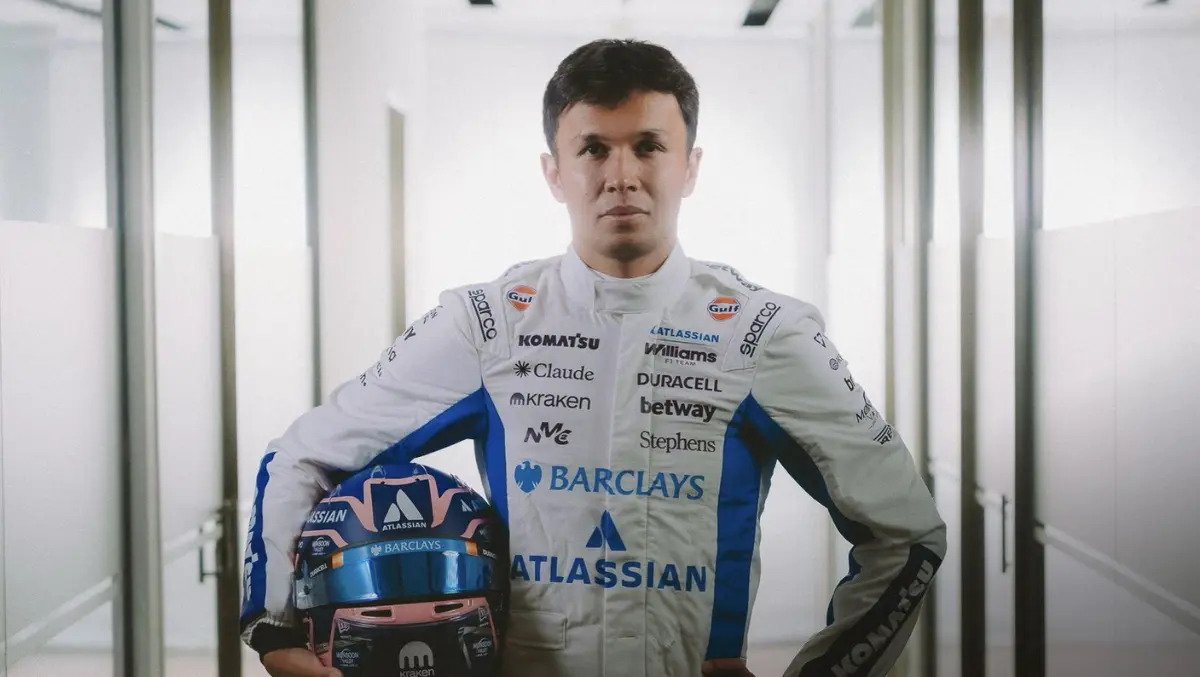
Keeper Security has initiated a global marketing campaign emphasizing an identity-first approach to cybersecurity, coinciding with the start of its third season as the official cybersecurity partner of the Atlassian Williams F1 Team. This campaign features driver Alex Albon and includes multiple television commercials and social media content filmed during pre-season testing in Bahrain. The campaign highlights the increasing threat of credential-based attacks, particularly through phishing and social engineering, which target privileged access rather than exploiting software vulnerabilities. Williams F1 utilizes Keeper's KeeperPAM platform to manage passwords, passkeys, and privileged accounts at both trackside and its UK headquarters. The partnership aims to enhance security while maintaining operational efficiency during race weekends. As the 2026 Formula 1 season approaches, the focus on identity security is critical for protecting sensitive telemetry and engineering data generated during races. The campaign underscores the importance of continuous verification of users and devices in high-performance environments.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…