 Railway.Supply
LA Metro Restricts Internal Systems After Cybersecurity Incident
Article Content

- •Unauthorized activity led LA Metro to restrict access to internal systems.
- •Fare payment disruptions occurred, affecting TAP card loading and digital arrival boards.
- •Train and bus operations remained unaffected, and no data breaches were reported.
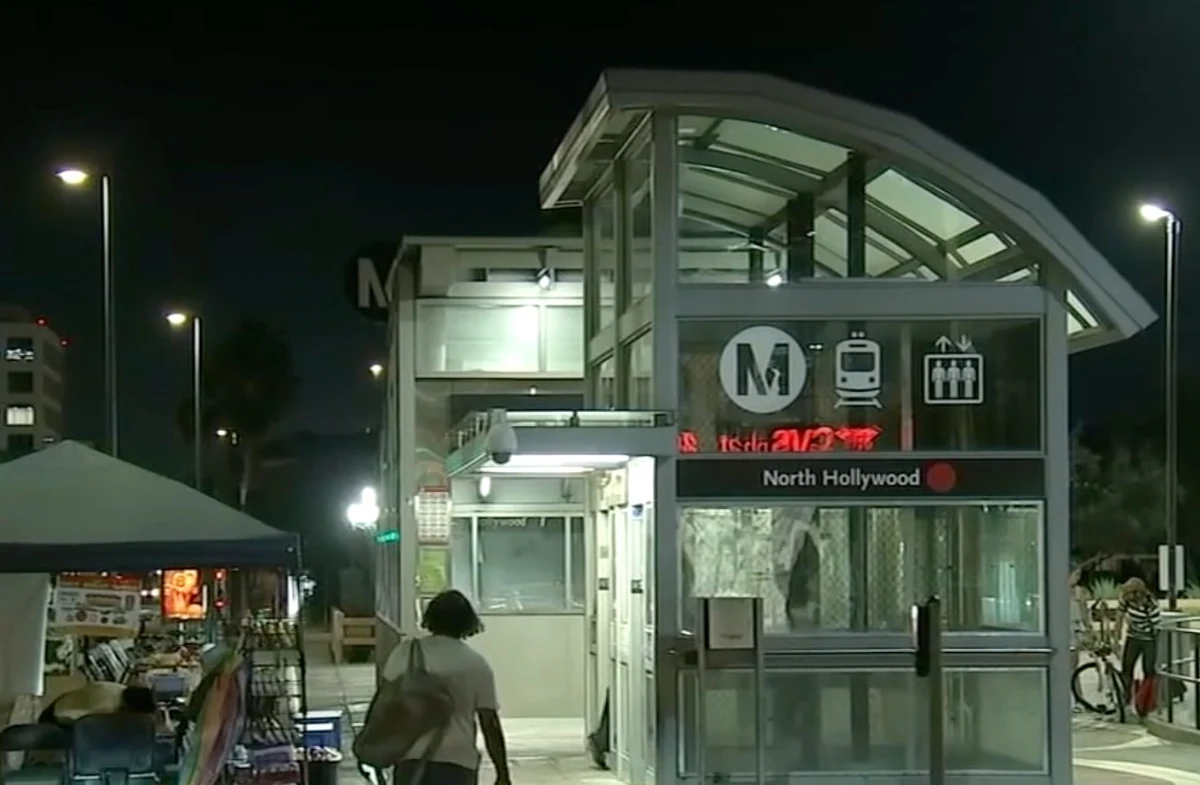
On March 21, 2026, Los Angeles Metro limited access to its internal administrative systems due to unauthorized activity detected on its network. This security incident disrupted fare payments and caused digital arrival boards to go blank, affecting riders' ability to load funds onto TAP cards. Despite these issues, train and bus operations continued normally, and officials confirmed that customer and employee data had not been compromised. Metro advised riders to use station ticket vending machines for fare loading while internal systems underwent security checks. The agency emphasized that the restrictions were precautionary and aimed at containing the unknown activity. Metro is working to restore affected systems and will keep riders updated on progress. The incident highlights the importance of cybersecurity measures in public transportation systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Los Angeles Metro in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…