 Indianewsnetwork
Leaked Cable Reveals US Pressure in Imran Khan's Ouster
Article Content

- •A leaked US diplomatic cable suggests pressure was applied for Imran Khan's ouster.
- •The cable indicates that a successful no-confidence vote was linked to US reconciliation efforts.
- •The leak raises significant concerns about foreign interference in Pakistan's political processes.
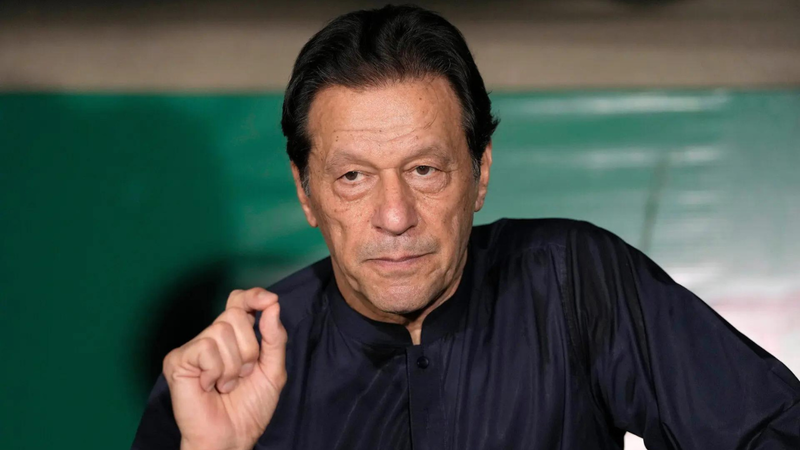
A leaked diplomatic cable has surfaced, suggesting that the United States pressured Pakistan to remove former Prime Minister Imran Khan. The cable, released by Drop Site, documents a conversation between Pakistan's envoy to the US and a senior US official, indicating that a successful no-confidence vote against Khan would lead to reconciliation. This has reignited debates over foreign interference in Pakistan's politics, as Khan has long claimed that his ouster was influenced by external forces due to his independent foreign policy. The cable's contents, particularly the phrase 'all will be forgiven,' have intensified scrutiny over the legitimacy of the current Pakistani government. Khan's supporters argue that the leak substantiates their claims of foreign meddling. The political implications of this revelation could affect Pakistan's internal stability and international relations. The current government has not confirmed the cable's authenticity, leaving the situation fluid.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…