 Infostealers
LiteLLM Supply Chain Attack Exposes Thousands of Companies to Cyber Threats
Article Content

- •LiteLLM attack compromised trusted AI software, affecting 2,500 companies.
- •Malicious uploads were available for only 40 minutes, yet posed significant risks.
- •The breach highlights vulnerabilities in software supply chains and developer tooling.
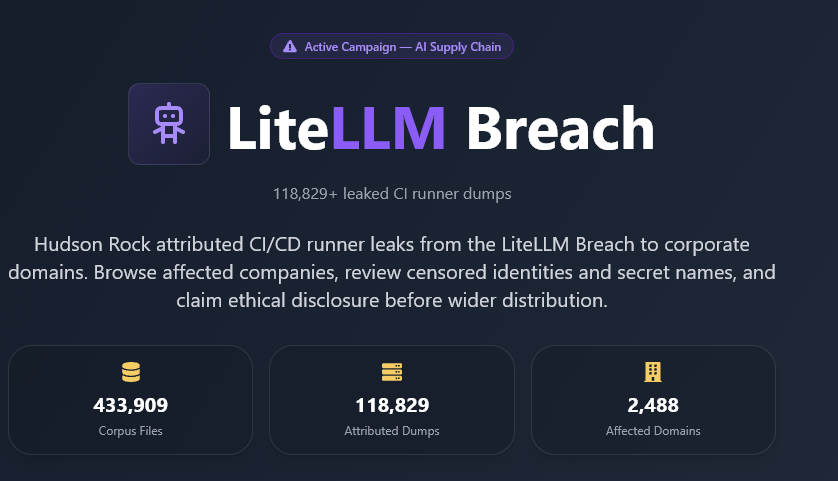
In March 2026, the LiteLLM AI software was compromised through a malicious upload to PyPI, lasting approximately 40 minutes. This breach allowed attackers to target 2,500 companies and 434,000 CI/CD pipelines, risking build systems, cloud accounts, and source code. The attack exploited vulnerabilities in the release process of trusted software components, highlighting the growing threat to AI infrastructure as a strategic target for credential theft and software supply chain abuse. The incident underscores the need for enhanced security measures in developer tooling and supply chain management. As of today, the attack's full impact is still being assessed, and organizations are urged to review their security protocols.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (26)
Continue Reading
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…
 Critical Code Injection Vulnerability in Staggs Plugin for WordPress A critical code injection vulnerability, CVE-2026-78287, has been identified in the Staggs plugin for WordPress, affecting versions up to 3.3.0. This flaw allows unauthenticated attackers to execute arbitrary code remotely, posing severe risks to affected sites. The vulnerability stems from improper control over code…