 www.lrt.lt
Lithuania Acquires US Merops Interceptors Amid Rising Drone Threats
Article Content

- •Lithuania purchased 48 Merops interceptors to strengthen air defense against drones.
- •The acquisition bypassed standard procurement to address urgent national security needs.
- •Merops interceptors have been successfully tested in combat, particularly against Iranian drones.
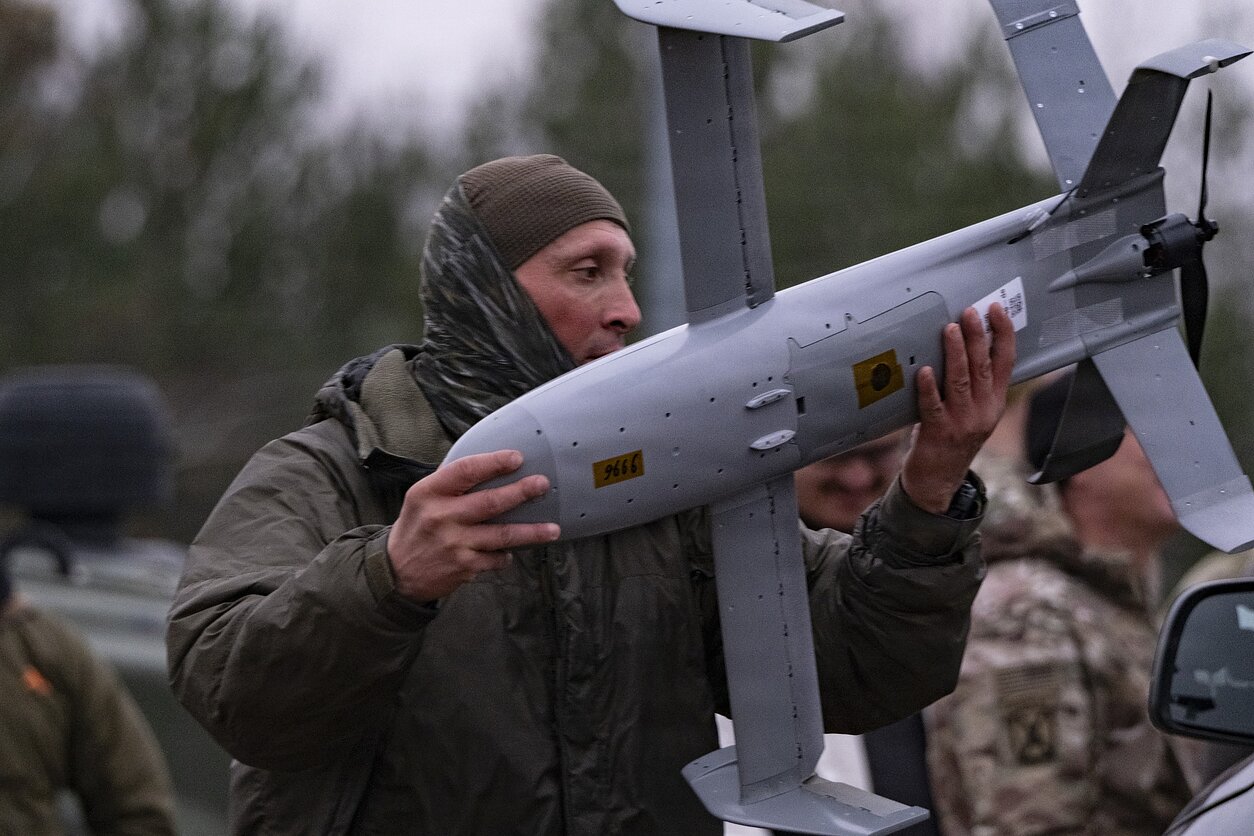
On April 22, 2026, Lithuania purchased 48 Merops interceptors from Perennial Autonomy to enhance its air defense capabilities against drone threats. The decision to bypass standard procurement procedures was made to expedite the acquisition, citing urgent national security needs due to recent incursions by Russian and Ukrainian drones. The Merops system, which includes non-lethal UAVs, has been tested in combat and is designed to intercept aerial threats like the Iranian Shahed drones. This pilot batch includes 24 units with thermal seekers and 24 with radio-frequency seekers, along with training and integration services. The Lithuanian Defense Minister emphasized that the system's proven effectiveness in Ukraine justified the purchase without competitive bidding. The acquisition aims to rapidly assess the technology's integration into Lithuania's airspace defense system. The move reflects a broader trend among NATO countries to bolster defenses against low-cost drone threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…