 www.splunk.com
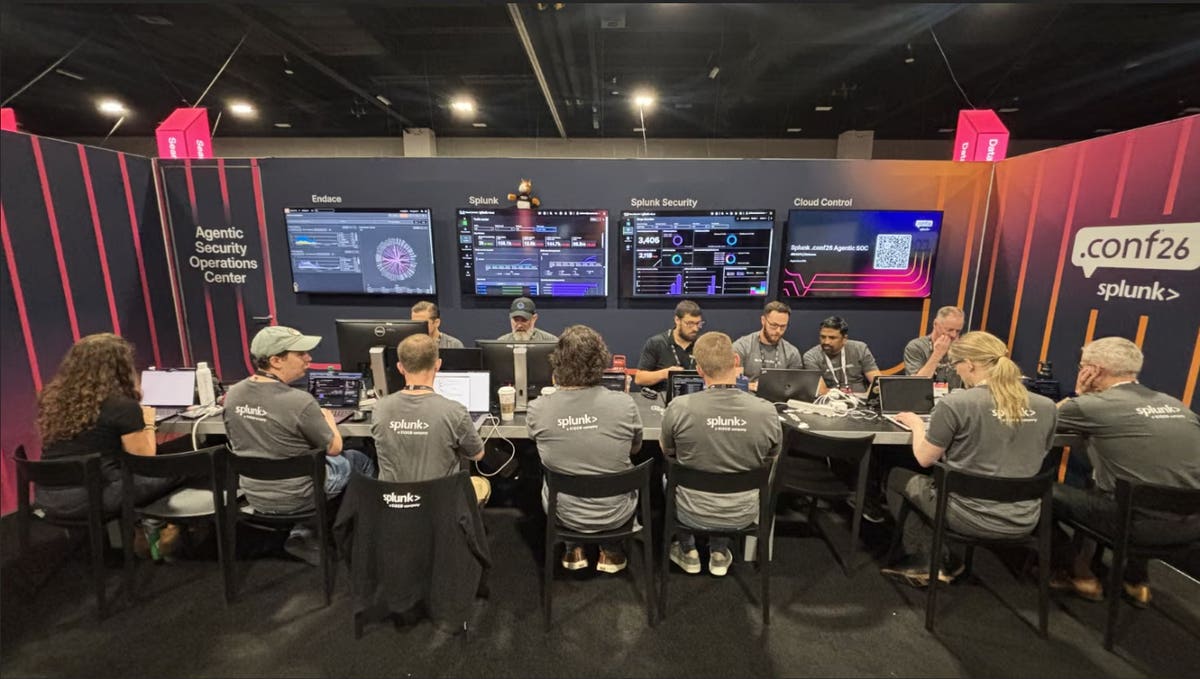
Live Agentic SOC at .conf26 Protects Attendees Amid Dynamic Threats
Article Content

- •The Agentic SOC protected over 5,145 attendees at .conf26 using advanced security technologies.
- •AI agents assisted human analysts in triaging alerts and gathering evidence without replacing their judgment.
- •The event demonstrated the challenges of cybersecurity in dynamic environments with high traffic and unmanaged devices.
During Splunk.conf26 in Denver, a live Agentic Security Operations Center (SOC) was established to protect over 5,145 attendees from various cybersecurity threats. The SOC utilized Cisco and Splunk technologies to monitor multi-gigabit traffic and respond to security incidents in real-time. Analysts faced the challenge of distinguishing benign anomalies from malicious activity in a high-throughput environment filled with unmanaged devices. The SOC architecture included autonomous triage agents, which assisted human analysts in evidence gathering and decision-making. The event highlighted the importance of maintaining a secure network while ensuring a seamless attendee experience. No specific CVEs or were reported, but the event served as a proving ground for innovative security operations. The SOC's mission was to protect first and innovate later, emphasizing the role of human analysts in validating AI-generated insights.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Following this threat?
Track Corepack and Cisco in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What technologies were used in the SOC?
How did the SOC handle false positives?
What was the main goal of the SOC at .conf26?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…