 Cybersecuritydive
Manufacturing Industry Faces Surge in Cyberattacks
Article Content

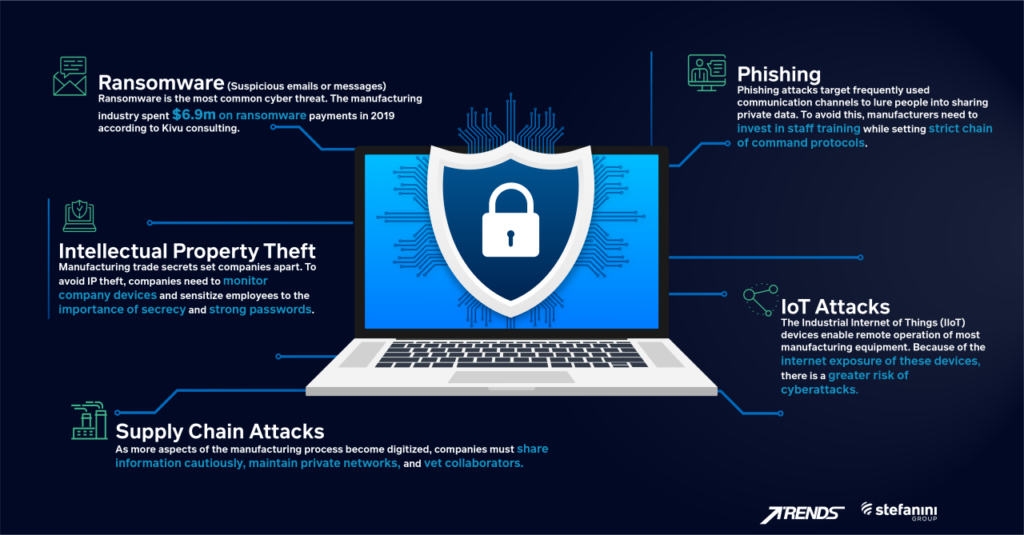
- •Manufacturing was the most attacked sector in 2025, indicating a critical vulnerability.
- •Experts recommend prioritizing cybersecurity measures based on real-world threats.
- •Common attack vectors include phishing and ransomware, necessitating immediate action.
In 2025, the manufacturing sector experienced the highest number of cyberattacks of any industry. Experts emphasize the need for manufacturers to prioritize vulnerabilities based on real-world threat activity. Common attack methods include phishing and ransomware, which have been particularly damaging. The scope of these attacks has led to significant operational disruptions and financial losses, prompting a call for enhanced cybersecurity measures. Recommendations include hardening networks and avoiding frequent mistakes that lead to breaches. The urgency of the situation is underscored by the increasing sophistication of attackers targeting manufacturing systems. Currently, manufacturers are advised to implement best practices to mitigate these risks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…