 www.twz.com
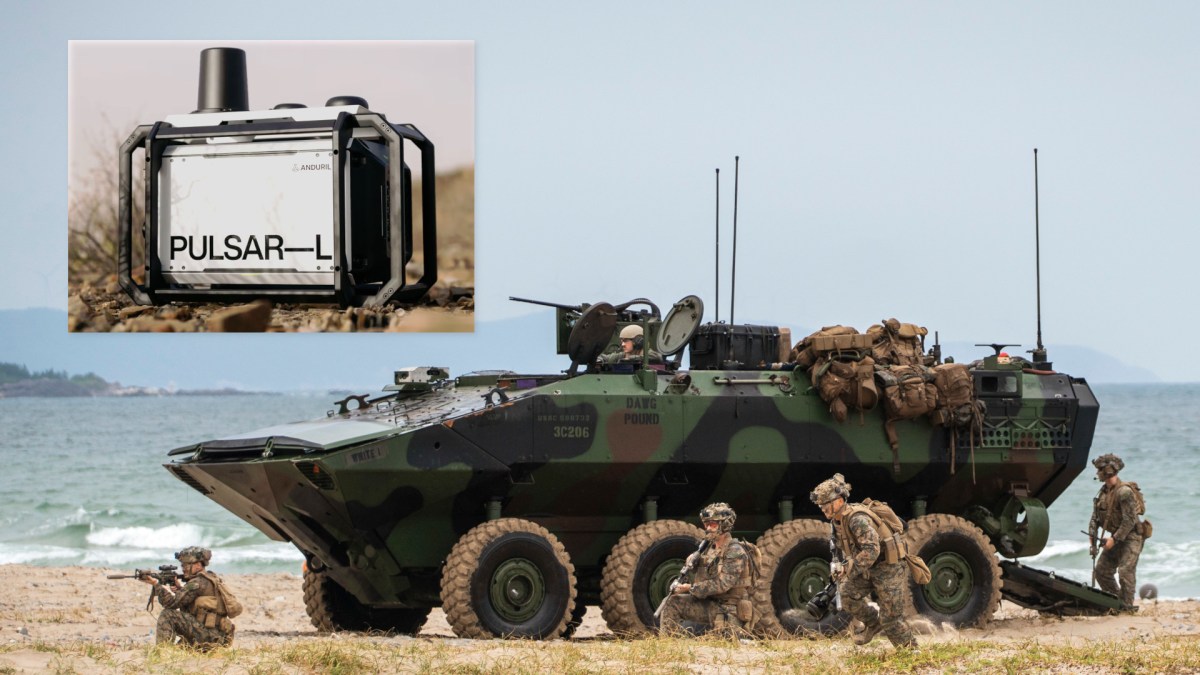
Marine Corps Acquires Pulsar-L Jammers to Combat Drone Threats
Article Content

- •Marine Corps awarded $15.7 million for Pulsar-L jammers to enhance ACV defenses.
- •Pulsar-L targets Group 1 and Group 2 drones, crucial for modern battlefield survivability.
- •Integration of jammers aims to counter increasing drone threats observed in conflicts like Ukraine.
The U.S. Marine Corps has awarded a $15.7 million contract to Anduril for the Pulsar-L electronic warfare jammers to enhance the defense of its Amphibious Combat Vehicles (ACVs) against drone attacks. This urgent acquisition follows the recognition of the vulnerability of armored vehicles to drone threats, particularly highlighted by the ongoing conflict in Ukraine. The Pulsar-L system is designed to detect, track, and defeat Group 1 and Group 2 unmanned aerial systems (UASs), which have been increasingly used in modern warfare. The Marine Corps plans to integrate an unspecified number of these systems into its fleet, which includes 150 ACV personnel carriers and various other variants. The Pulsar-L is noted as the only solution that meets the ACV's space, weight, and power constraints while providing essential defensive capabilities. Deliveries of the Pulsar-L systems are expected to begin in January 2027.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…