 Pasqualepillitteri.It
Mass Credential Theft Targets AI Developer Platforms
Article Content

- •At least nine AI developer platforms were compromised in October 2026.
- •Attacks focused on environment variables storing sensitive access keys.
- •Unauthorized charges reported, with losses reaching $1,700 for some users.
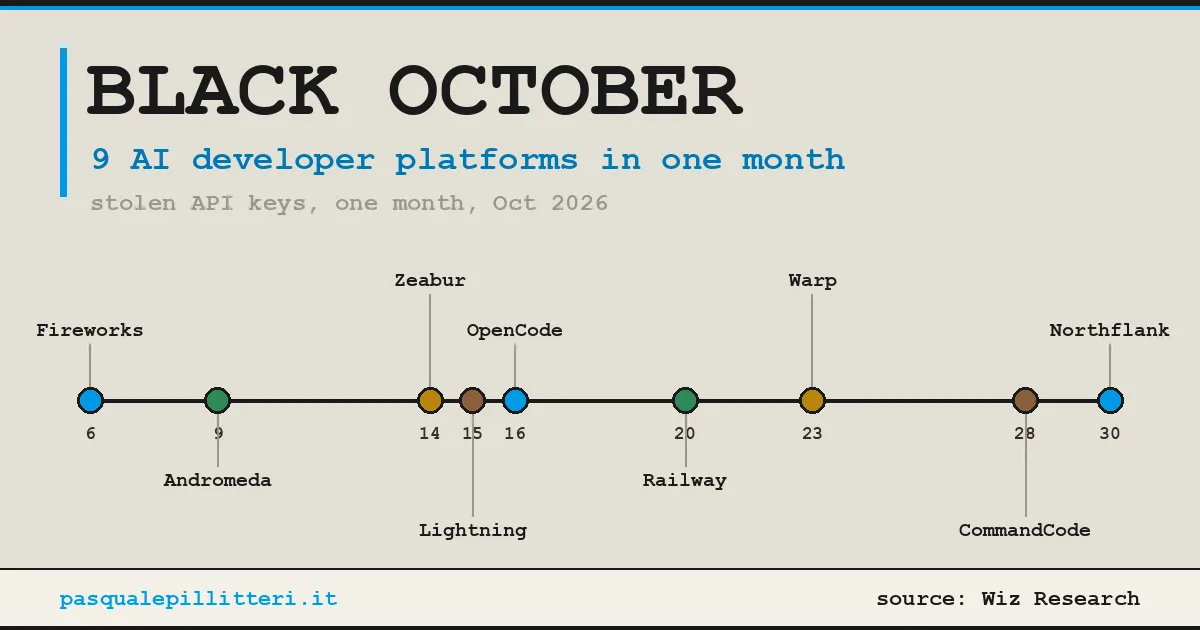
In October 2026, at least nine AI developer platforms, including Fireworks AI and Railway, reported security incidents attributed to credential access attacks. These attacks primarily targeted environment variables storing access keys to AI models, with indications of an 'agent swarm' attack methodology. Wiz, a cloud security firm, noted that the incidents began with Fireworks AI on October 6 and continued through the month, culminating in reports from Northflank on October 30. The root causes varied, with some platforms citing privilege escalation and others linking breaches to legacy systems or third-party dependencies. The overall impact includes significant unauthorized charges for users, with reports of losses amounting to $1,700 from OpenCode alone. Despite the widespread nature of these incidents, no single vulnerability has been identified as a common factor among the affected platforms. The attacks highlight a growing trend in credential exploitation within the AI sector.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Andromeda and Anthropic in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which platforms were affected?
What is the primary attack vector?
What should affected users do?
Continue Reading
 Northflank Security Incident: Major Breach Reported on October 30, 2026 On October 30, 2026, Northflank reported a significant security incident affecting its platform. Users were advised to assume that all environment variables had been decrypted and to rotate all secrets immediately. Reports indicate that some users experienced unauthorized use of their AI API keys. Northflank's status…
 North Korean Hackers Steal $6.3 Billion from Binance in Record Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a massive security breach resulting in the theft of approximately $6.3 billion across ten blockchains. The attack is attributed to North Korea's TraderTraitor hacking group, which gained access via a compromised DevOps engineer's…