 ransomnews.com
Massive Ticketmaster Data Leak Exposes 412,000 Festival Buyers
Article Content

- •Over 412,000 records from The Town 2025 festival are being sold on the dark web.
- •The leaked data includes sensitive personal information, particularly Brazilian CPF numbers.
- •Ransomnews confirmed the authenticity of the data, indicating a significant risk of identity theft.
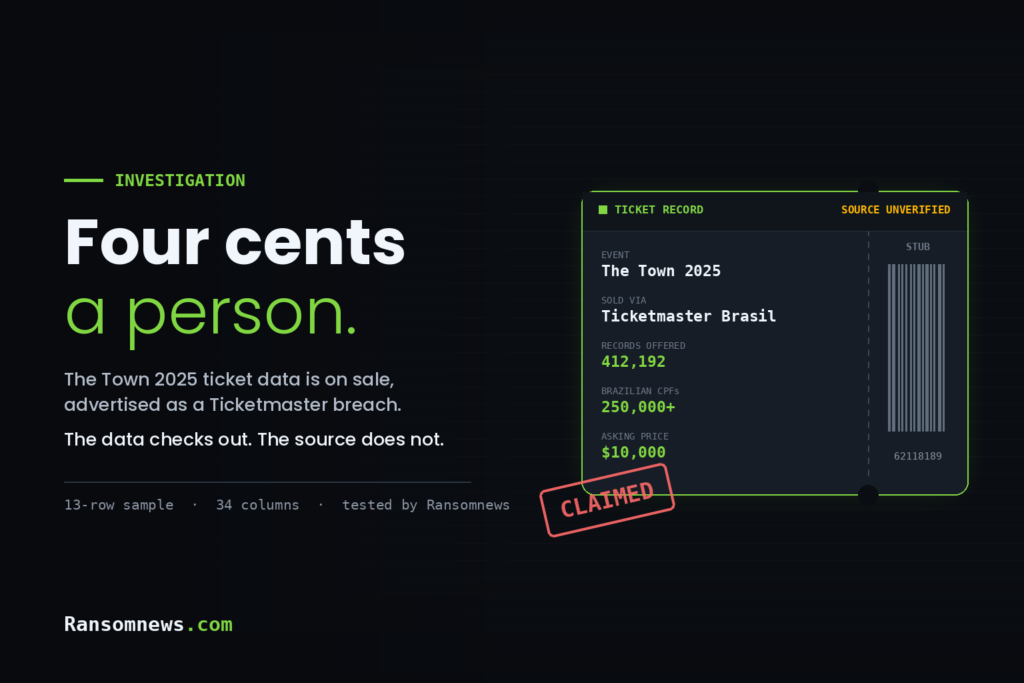
On September 2, 2026, a seller on a Russian-language data-trading forum listed what they claimed to be an internal Ticketmaster database containing 412,192 purchase records from The Town 2025 festival, primarily affecting Brazilian buyers. The leaked data includes sensitive information such as names, email addresses, CPF numbers, and payment details, with a breach date noted as August 28, 2026. Ransomnews confirmed the authenticity of the data sample, which shows a significant concentration of Brazilian records, comprising 61% of the total. The seller is offering the full database for $10,000 or $80 per thousand records, explicitly stating that the CPF numbers can be used for bank fraud and SIM registration. The data breach's source remains unverified, raising concerns about identity theft and fraud risks for the affected individuals. The listing's details and the validation of the data indicate a serious threat to personal security for those involved.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 PHP2Shell Vulnerabilities Exploited by AI-Driven Attackers Threat actors have exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to target a government entity in Europe, gaining access to sensitive data within two hours of the initial breach. The attackers utilized AI tools for reconnaissance and post-exploitation activities, including accessing…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…