 Futurism
Meta Exploits Tax Breaks Through AI Data Centers
Article Content

- •Meta saved nearly $4 billion in taxes by exploiting a tax break for research.
- •The IRS is investigating Meta's use of dubious tax credit claims.
- •Public backlash against Meta's tax strategies could impact midterm elections.
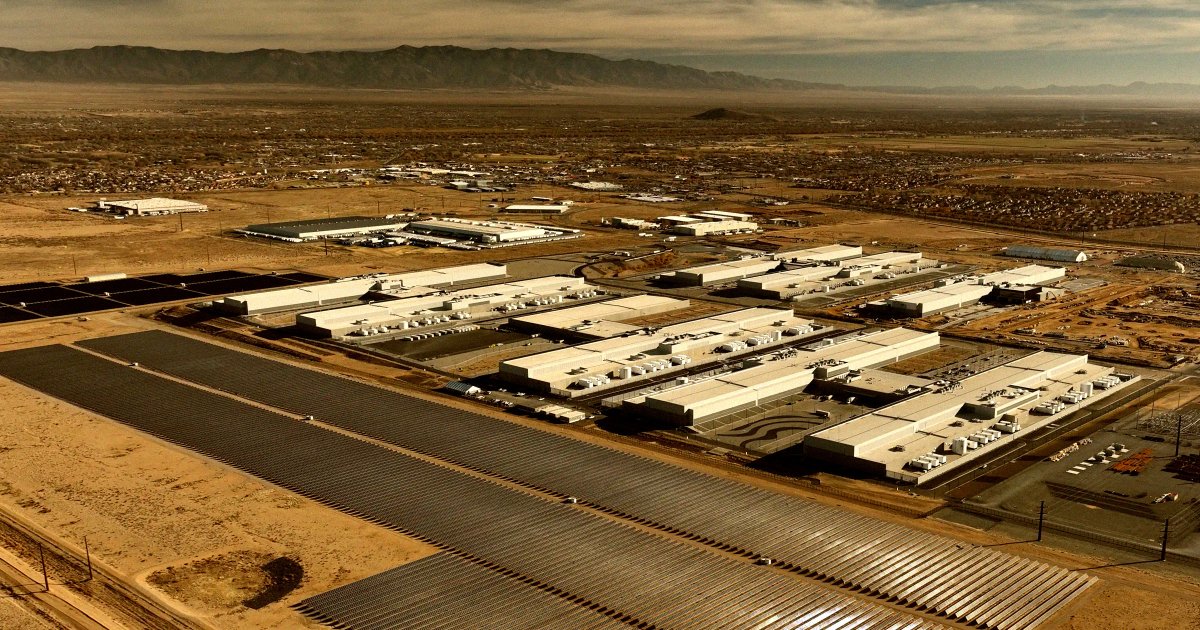
Meta is reportedly using its AI data centers to exploit a tax break intended for research and experimentation, saving billions in taxes. The company claims these data centers are 'pilot models' under a Reagan-era tax credit, a claim that its own accountants consider legally dubious. In 2024, Meta saved $2 billion, and in 2025, it saved nearly $4 billion, making it the largest beneficiary of this tax credit among public companies. The IRS is currently attempting to recover $355 million that Meta saved through another tax loophole. This situation has sparked public backlash and could influence upcoming midterm elections. The IRS has previously called out many companies for abusing similar tax credits. Meta's spokesperson stated that the company is investing heavily in research and development to support American jobs, but the legitimacy of its claims remains uncertain.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
How much has Meta saved in taxes?
What is the IRS doing about this?
What are the implications of this for Meta?
Continue Reading
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…