 Recordedfuture
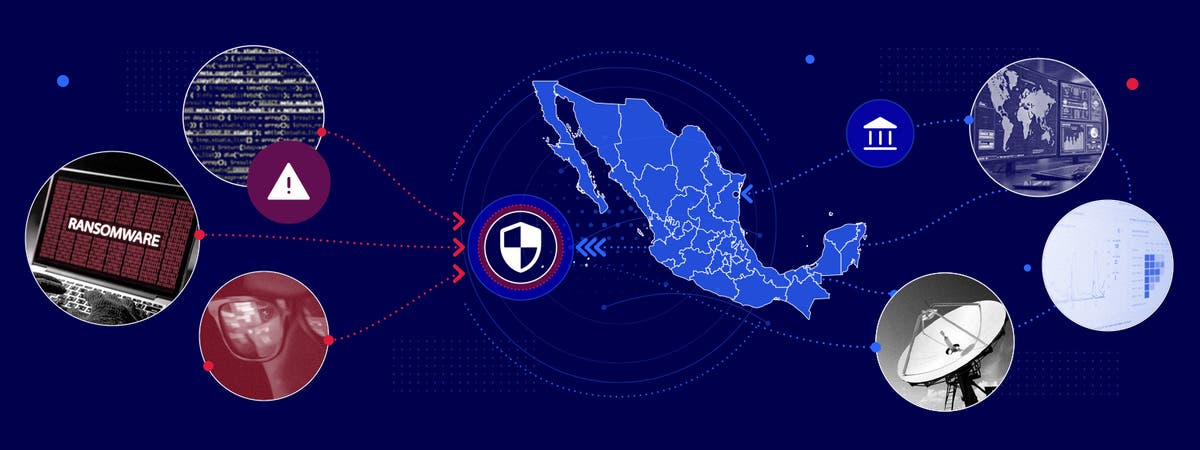
Mexico's Cybersecurity Plan Addresses Rising Ransomware Threats
Article Content

- •Mexico's National Cybersecurity Plan aims to enhance defenses against rising ransomware threats.
- •223 ransomware incidents were reported in Mexico from 2020 to 2026, affecting multiple sectors.
- •The plan includes a six-phase roadmap for improving cybersecurity capabilities by 2030.
Mexico's National Cybersecurity Plan, introduced in December 2025, aims to tackle increasing cyber threats, particularly ransomware, which has seen 223 incidents involving 64 groups from 2020 to 2026. The plan is a response to the urgent need for improved cyber defenses following the FIFA World Cup 2026, which stressed the country's digital infrastructure. Mexico is ranked as a 'Tier 2' nation in the ITU's 2024 Global Cybersecurity Index, indicating a need for enhanced institutional capacity and international cooperation. The plan outlines a six-phase roadmap to build cybersecurity capabilities by 2030, with a focus on sectors like government, manufacturing, and IT. Key ransomware groups targeting Mexico include LockBit and Qilin, with significant impacts on critical infrastructure. The government, led by President Claudia Sheinbaum, is committed to full implementation, supported by a congressional majority. However, experts express skepticism about the government's ability to establish necessary institutions effectively.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Alphv, FamousSparrow and Casabaneiro in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Malware Analysis Reveals 30% of Dark Web Executables Are Malicious A recent study analyzed over 20,000 executable files harvested from the Dark Web, revealing that 30% are classified as malicious by various malware analysis tools. The research utilized a crawler that scanned over 15 million web pages to collect these files. The analysis employed services like VirusTotal, Hybrid…
 FamousSparrow Deploys SparroWocky Backdoor in Latin America The China-aligned cyberespionage group FamousSparrow has replaced its previous backdoor, SparrowDoor, with a new malware called SparroWocky, targeting governmental organizations in Latin America since August 2025. ESET Research attributes this campaign to a likely response to increased U.S. interests in the region.…