 blog.orange.tw
Microsoft Edge Sandbox Exploit Revealed: Logic Bugs Lead to $175,000 Win
Article Content

- •Orange Tsai exploited logic flaws in Microsoft Edge to escape its sandbox.
- •The exploit earned $175,000 at Pwn2Own Berlin and was confirmed by multiple sources.
- •Microsoft patched the vulnerabilities in May 2026, making updated Edge versions secure.
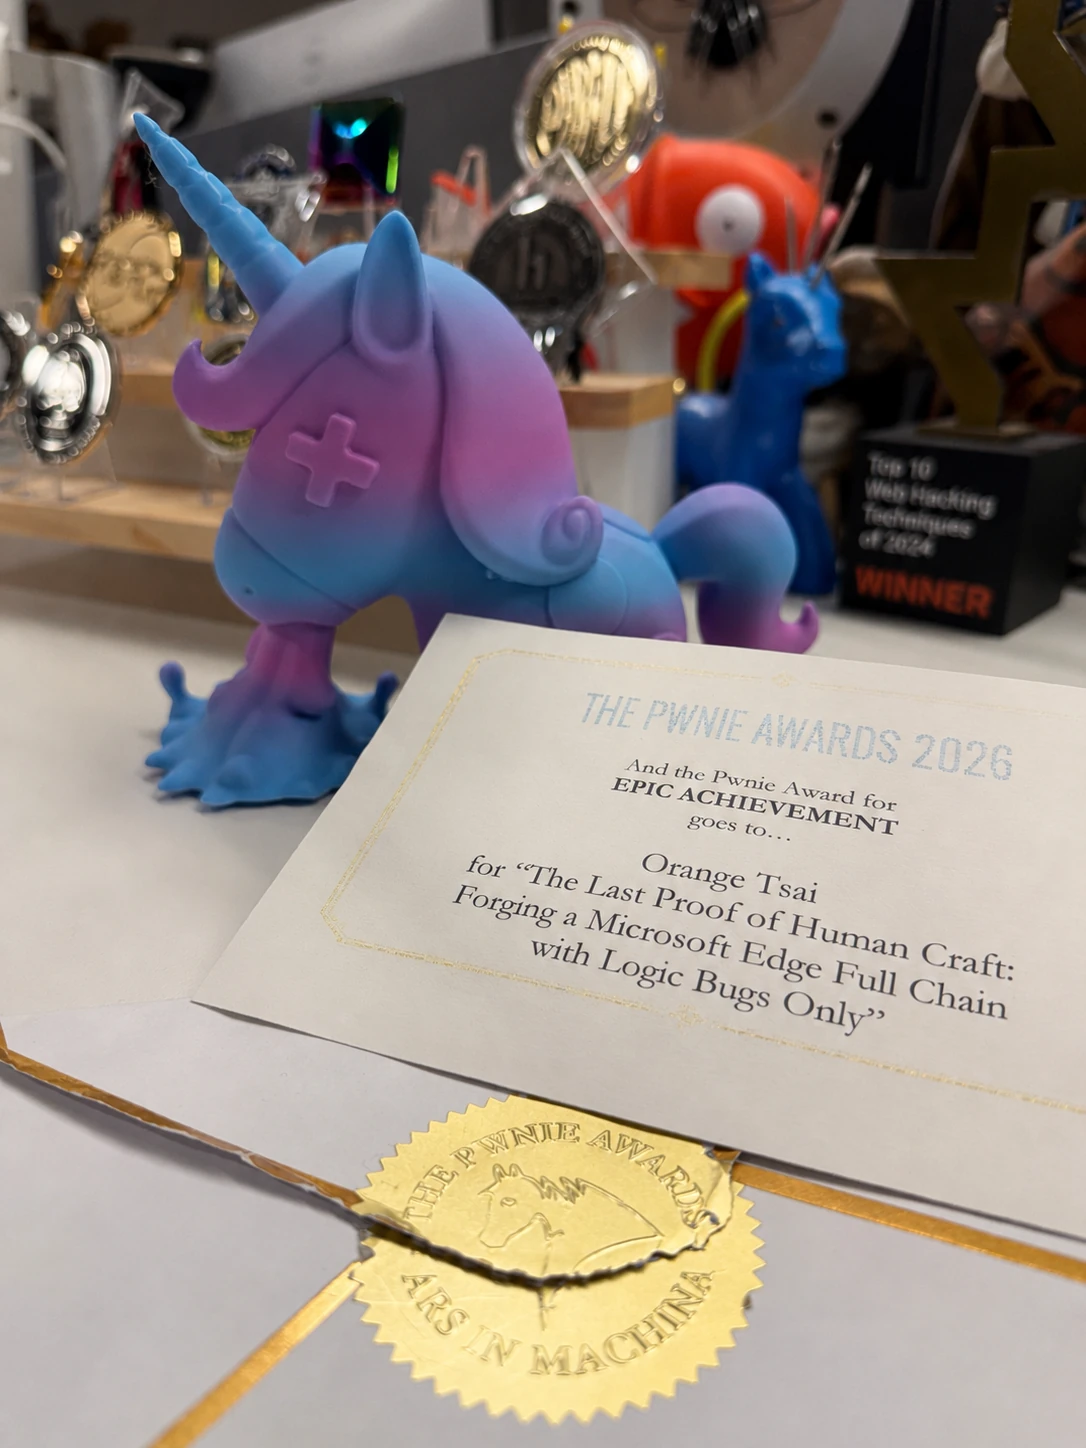
On October 28, 2026, Orange Tsai of DEVCORE disclosed a full exploit chain that escaped the Microsoft Edge sandbox using only logic flaws, earning $175,000 at Pwn2Own Berlin. The exploit involved chaining four logic bugs, with no memory corruption or AI used. Microsoft patched the vulnerabilities in May 2026, and updated versions of Edge are no longer vulnerable. The exploit was confirmed to be a significant achievement, nominated for a Pwnie Award for Epic Achievement. The full chain included five bugs and two Windows features, showcasing the effectiveness of manual bug hunting in an era dominated by AI solutions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Microsoft in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What vulnerabilities were exploited?
Are the vulnerabilities still a threat?
How was the exploit achieved?
Continue Reading
 Brotli Decoder Vulnerability Patched Across Multiple Linux Distributions A vulnerability, CVE-2026-111497, affecting the Brotli decoder has been patched in various Linux distributions, including Fedora 44 and Oracle Linux 10. The flaw allows for an out-of-bounds write, which could potentially enable attackers to execute arbitrary code. The vulnerability was published on October 22, 2026…