 Pressreleasehub.Pa.Media
Midmarket Cybersecurity Leaders Struggle with Inadequate Solutions, Revealed in New Report
Article Content

- •46% of midmarket cybersecurity leaders lack suitable technology solutions.
- •42% of teams report feeling overwhelmed despite increased budgets.
- •51% estimate a week to assess exposure to critical vulnerabilities.
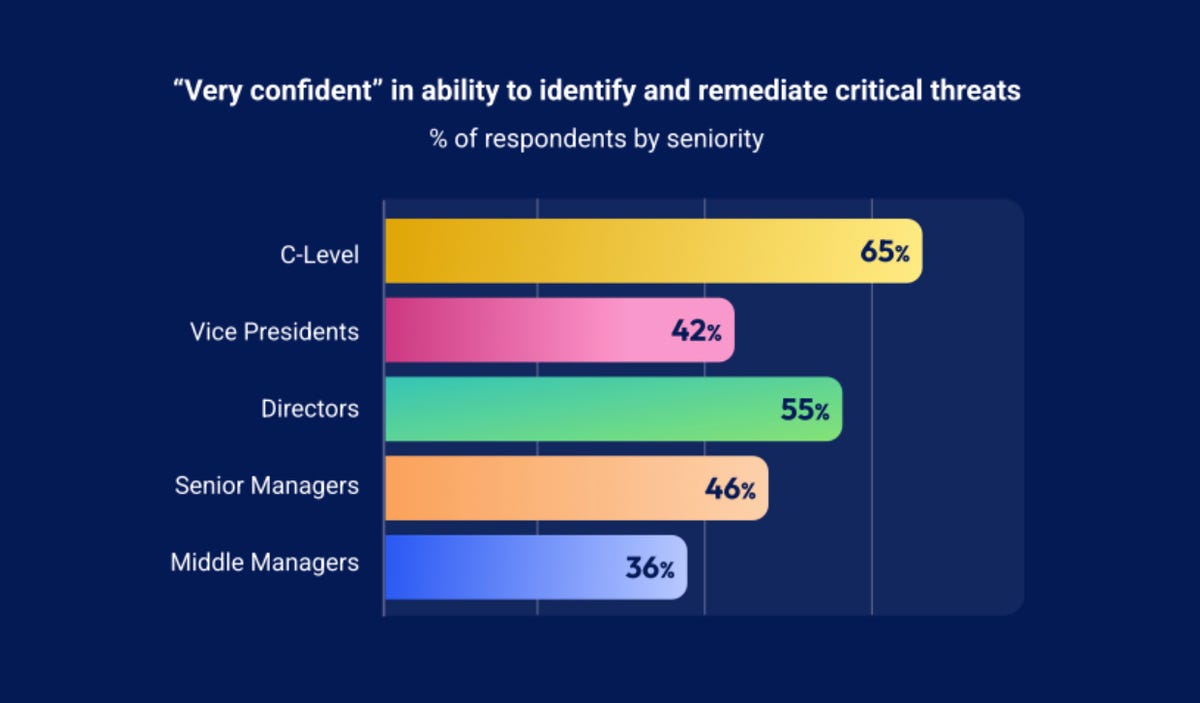
Intruder released its Security Middle Child Report on March 12, 2026, highlighting the challenges faced by midmarket cybersecurity leaders in the US and UK. The report indicates that nearly half of these leaders feel they lack appropriate technology solutions, contributing to what is termed the 'security middle child problem.' Specifically, 46% of respondents believe enterprise platforms are too complex for their needs, while 29% find SME tools inadequate. Despite a reported increase in budgets and headcount, 42% of teams describe themselves as overwhelmed. The report reveals a significant confidence gap, with 94% of leaders confident in identifying threats, but only 35% of middle managers sharing that confidence. A critical concern is that 51% of respondents estimate it would take about a week to assess exposure to a zero-day vulnerability, which is too long given the rapid exploitation timelines in the current threat landscape.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…