 www.miggo.io
CISA Directs Shift to SSVC Scoring for Vulnerability Management
Article Content

- •CISA's BOD 26-04 mandates federal agencies to use SSVC for vulnerability prioritization.
- •Miggo Security has added SSVC scoring to its platform to enhance vulnerability management.
- •The new framework focuses on exploitability and business impact rather than just severity.
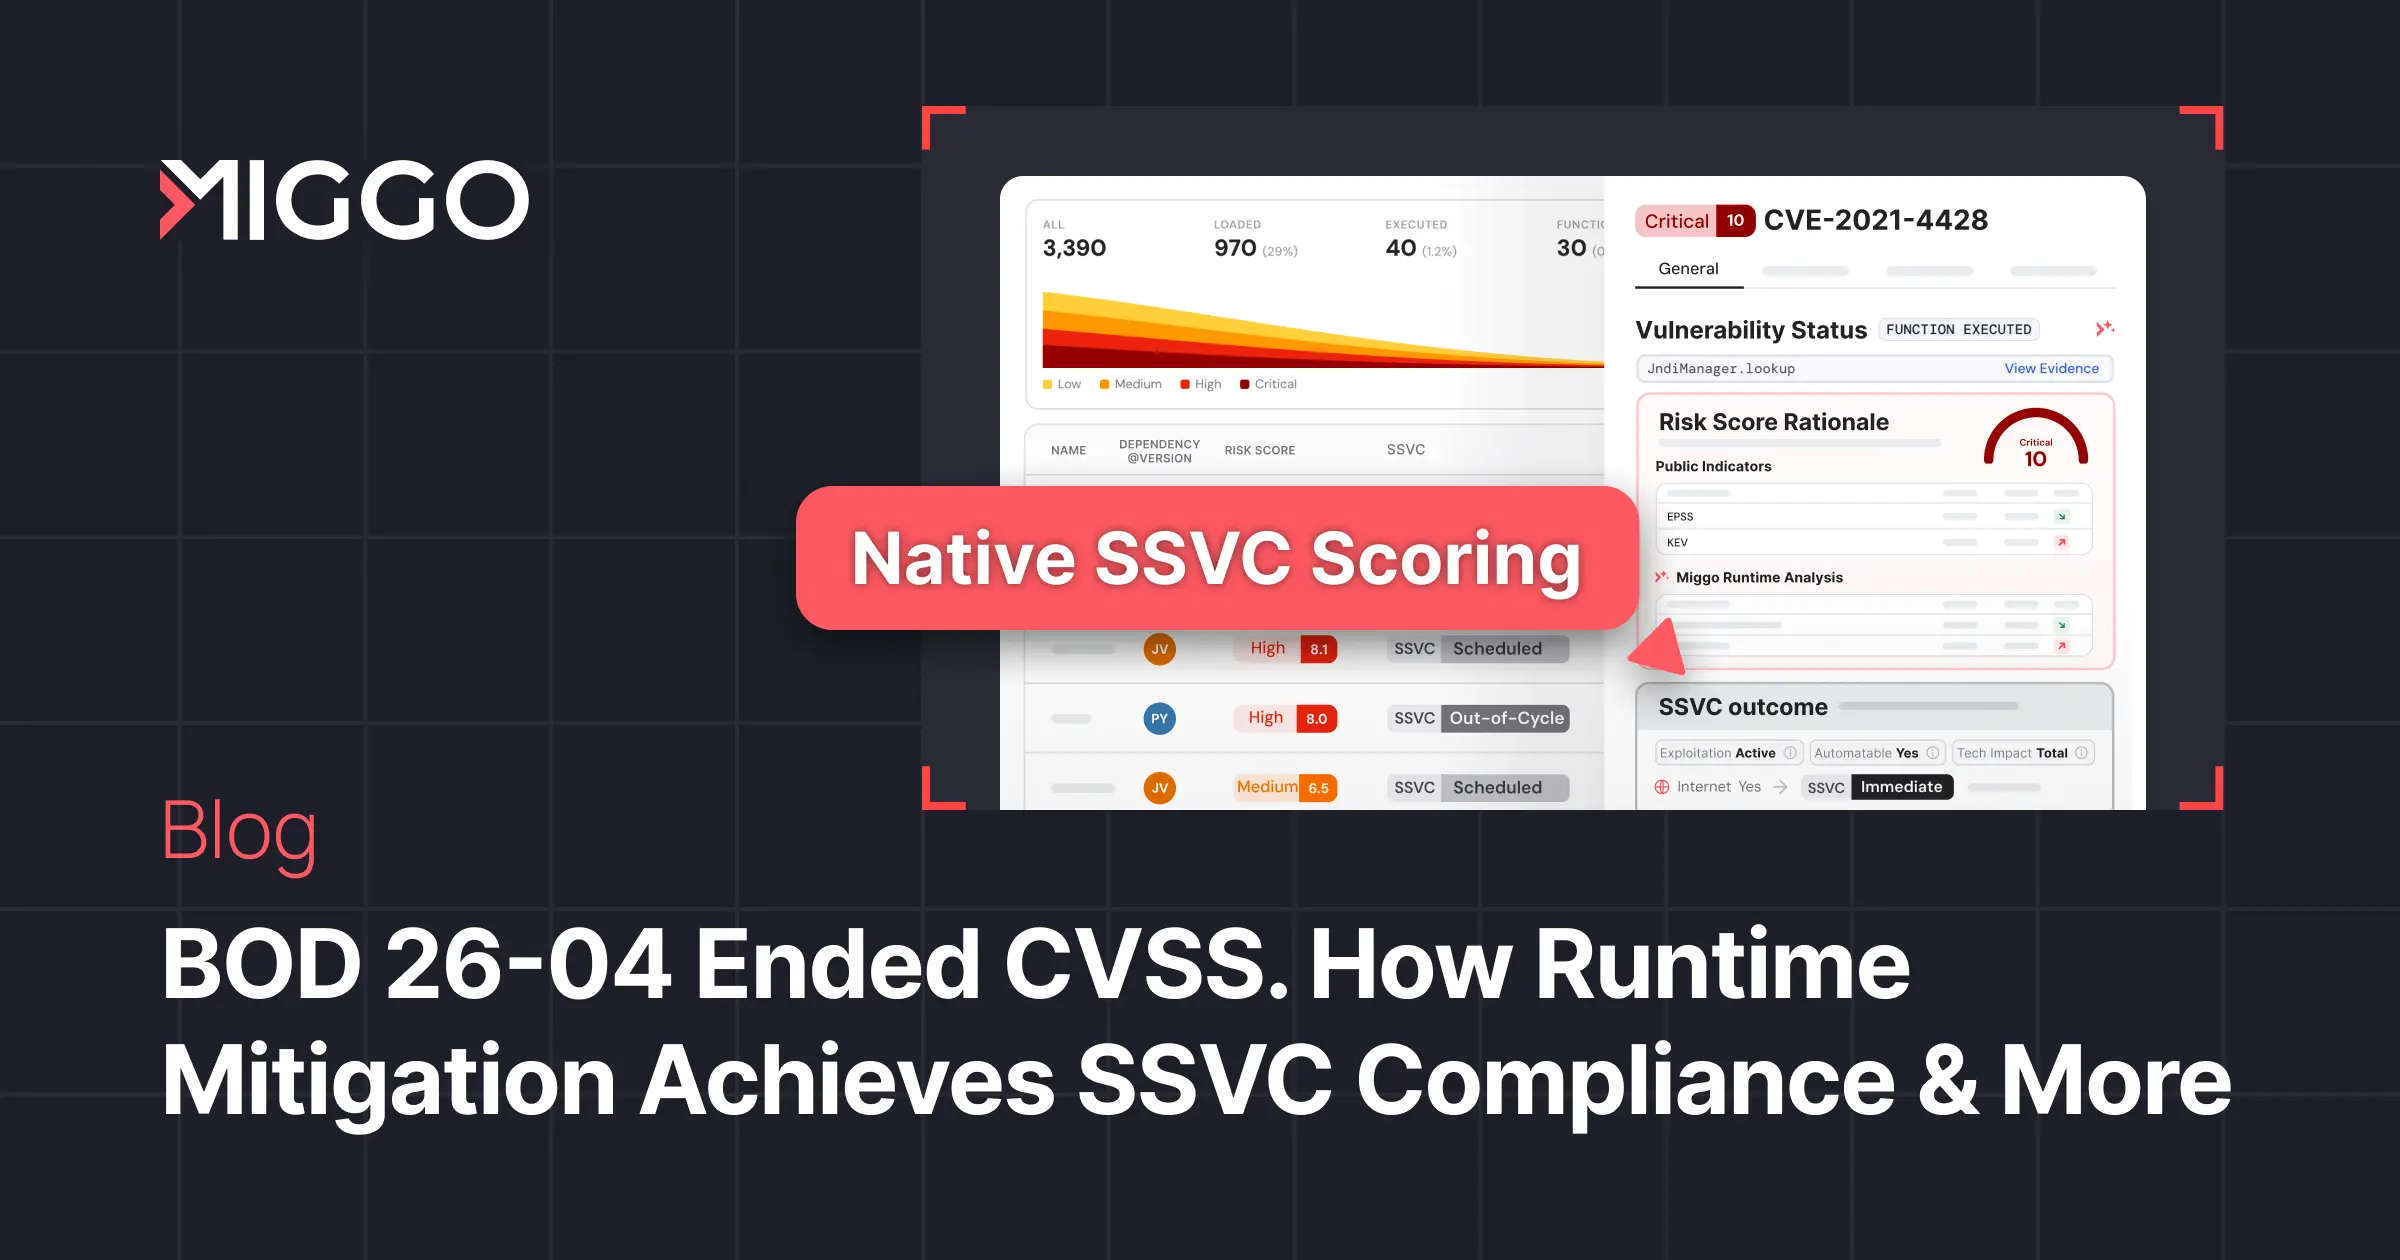
CISA has mandated U.S. federal agencies to adopt Stakeholder-Specific Vulnerability Categorization (SSVC) through BOD 26-04, moving away from CVSS scores. This new framework emphasizes assessing vulnerabilities based on their exploitability and impact rather than severity alone. Miggo Security has integrated native SSVC scoring into its platform to align with this directive. The platform will now provide insights on which vulnerabilities are reachable and exploitable in real-time, enhancing decision-making for security teams. This shift aims to reduce the backlog of vulnerabilities and improve the prioritization of remediation efforts. The integration allows users to see SSVC outcomes alongside existing CVSS scores, offering a clearer picture of risk in their specific environments. The runtime approach of Miggo's platform tracks application behavior to identify active vulnerabilities, providing actionable insights during the patching process.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…