 thesun.ng
Military Denounces AI-Generated Video Misrepresenting Defense Leaders
Article Content

- •The DHQ confirmed a manipulated video misrepresenting military leaders is circulating online.
- •The video is a deliberate attempt to misinform the public and create confusion about military leadership.
- •The DHQ urges the public and media to verify military-related information through official channels.
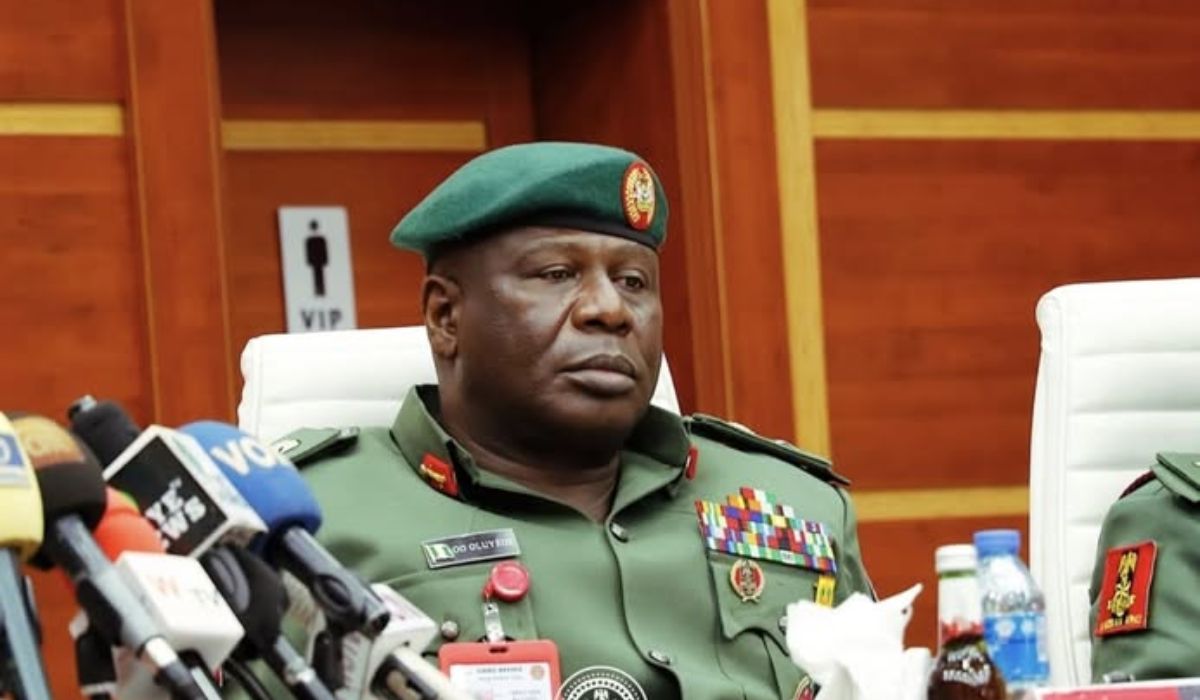
The Defence Headquarters (DHQ) of Nigeria has condemned a video circulating on social media that falsely portrays the Chief of Defence Staff, General Christopher Musa, and the Chief of Army Staff, Lieutenant General Olufemi Oluyede. The DHQ stated that the video is digitally manipulated and does not represent any official military communication. They urged the public to disregard the video, emphasizing that it is a deliberate attempt to misinform and create confusion regarding military leadership. The DHQ expressed concern over the misuse of digital technologies to fabricate content involving senior military officers, warning that such misinformation could undermine public trust and national security. The military has called on social media influencers and the public to verify information through official channels before dissemination. The situation highlights the growing trend of misinformation in the digital age, particularly concerning military matters.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…