 Dailysabah
MIT Operation Uncovers Cyber Espionage in Ankara
Article Content

- •Five suspects detained in Ankara for cyber espionage linked to Aydo Yazılım.
- •Unauthorized access to personal data through union software query interface discovered.
- •Investigation ongoing to assess the extent of data misuse and involved unions.
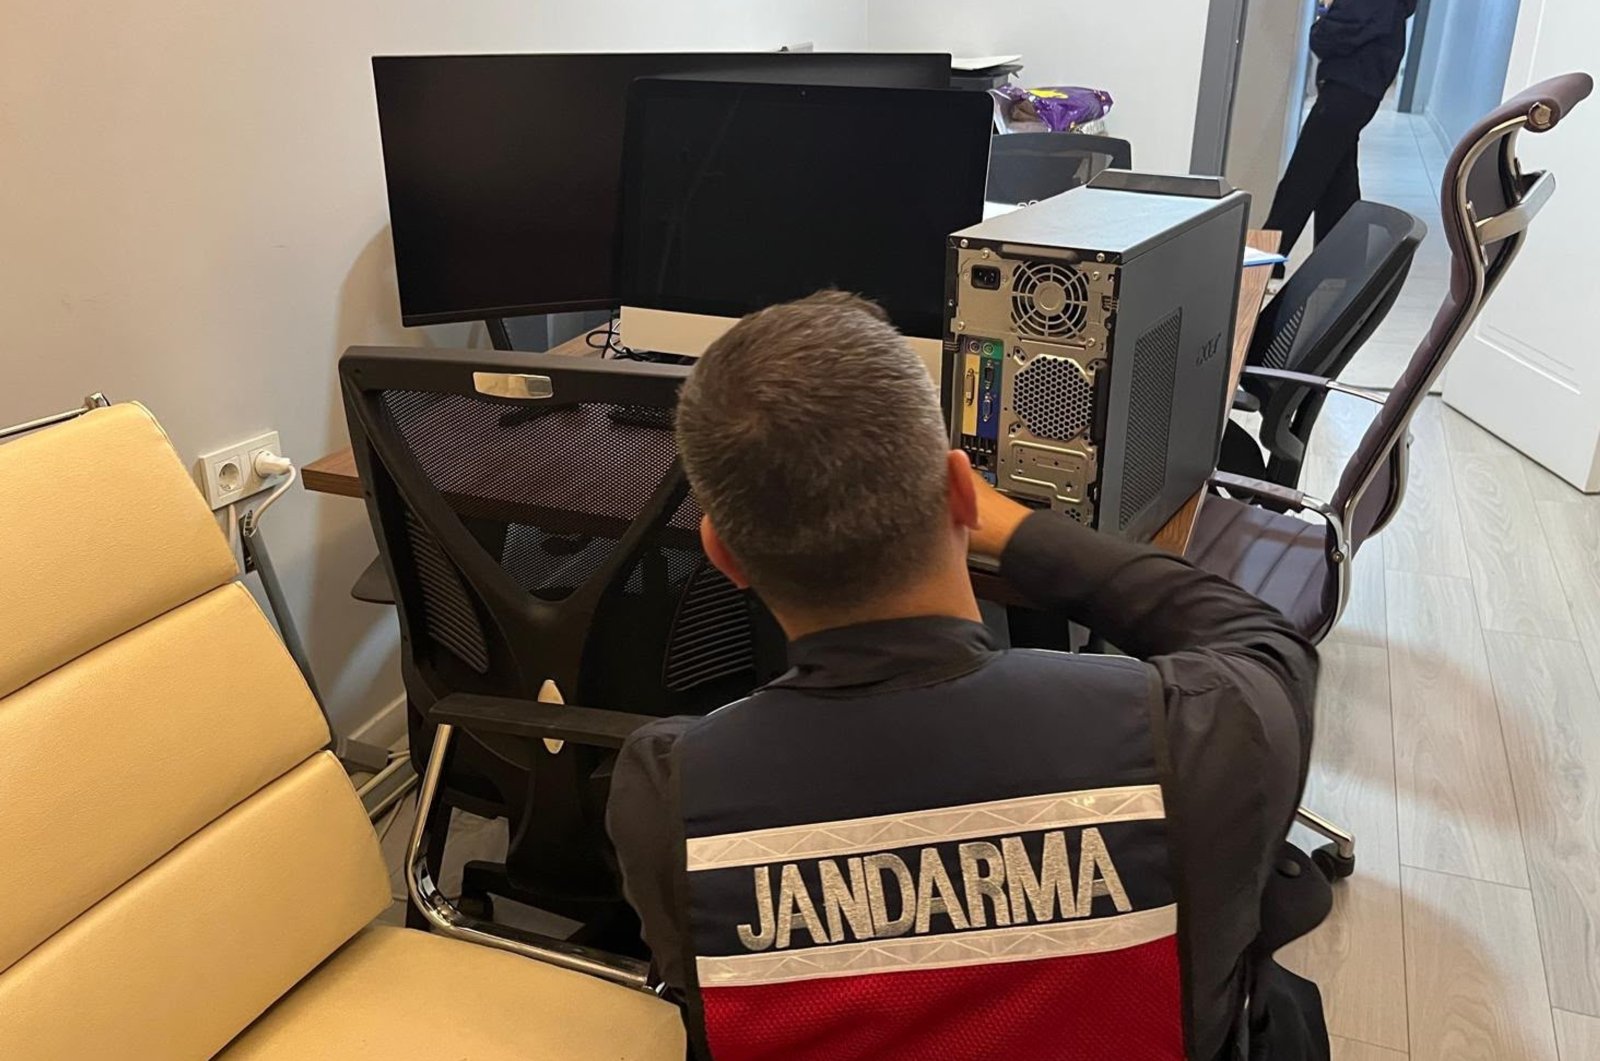
A coordinated operation by Turkey's National Intelligence Organization (MIT) led to the detention of five suspects linked to cyber espionage activities involving Aydo Yazılım, a software company in Ankara. The investigation revealed that Aydo Yazılım had integrated a query interface into union software, enabling unauthorized access to personal data of non-members. This data included identity and population information, and extensive personal records, some belonging to individuals under 18. The system was reportedly used to complete membership information for unions. During the operation, numerous digital devices were seized, and the investigation is ongoing to determine the extent of the data misuse and which unions were involved. Aydo Yazılım also provided consultancy services under Turkey's Personal Data Protection Law, raising further concerns about their practices. The investigation's findings suggest a significant breach of personal data protection protocols.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Aydo Yazılım in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab Vulnerabilities Exploited Within Hours of Disclosure On September 10, 2026, GitLab released patches for critical vulnerabilities CVE-2026-85706 and CVE-2026-87719. CVE-2026-85706, a path traversal flaw, allows unauthenticated users to read arbitrary files from GitLab servers, while CVE-2026-87719 enables credential theft via insecure deserialization. Both…