 www.pcrisk.com
Monoxide RAT: New Remote Access Trojan Threatens Windows Users
Article Content

- •Monoxide RAT allows full remote control of infected Windows systems.
- •It features capabilities like webcam access and file management.
- •No confirmed reports of active exploitation or specific IOCs are available.
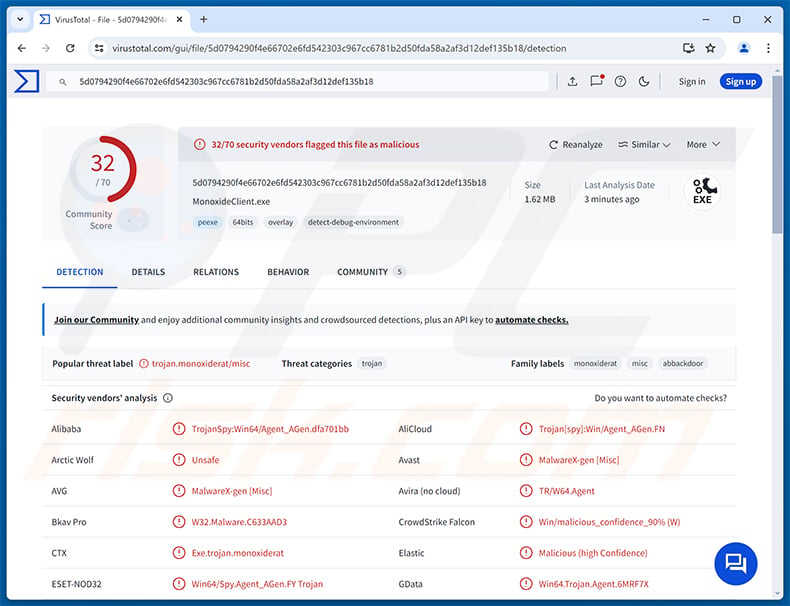
Monoxide RAT is a newly identified remote access trojan (RAT) targeting Windows systems, allowing attackers to gain full control over infected machines. It is reportedly sold or rented to cybercriminals for spying, data theft, and delivering additional malware. The malware operates silently, providing features such as remote desktop access, webcam streaming, and file management capabilities. There is currently no confirmed information on the number of infections or the identity of its developers. The threat has been detailed in a removal guide published by PCrisk on October 22, 2026, which outlines its functionalities and potential risks. As of October 26, 2026, there are no known public reports of or specific indicators of compromise (IOCs) associated with Monoxide RAT. Users are advised to remain vigilant and follow recommended removal steps if they suspect infection.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Monoxide in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What systems are affected by Monoxide RAT?
How can I remove Monoxide RAT?
Is there any active exploitation of Monoxide RAT?
Continue Reading
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…