 Helpnetsecurity
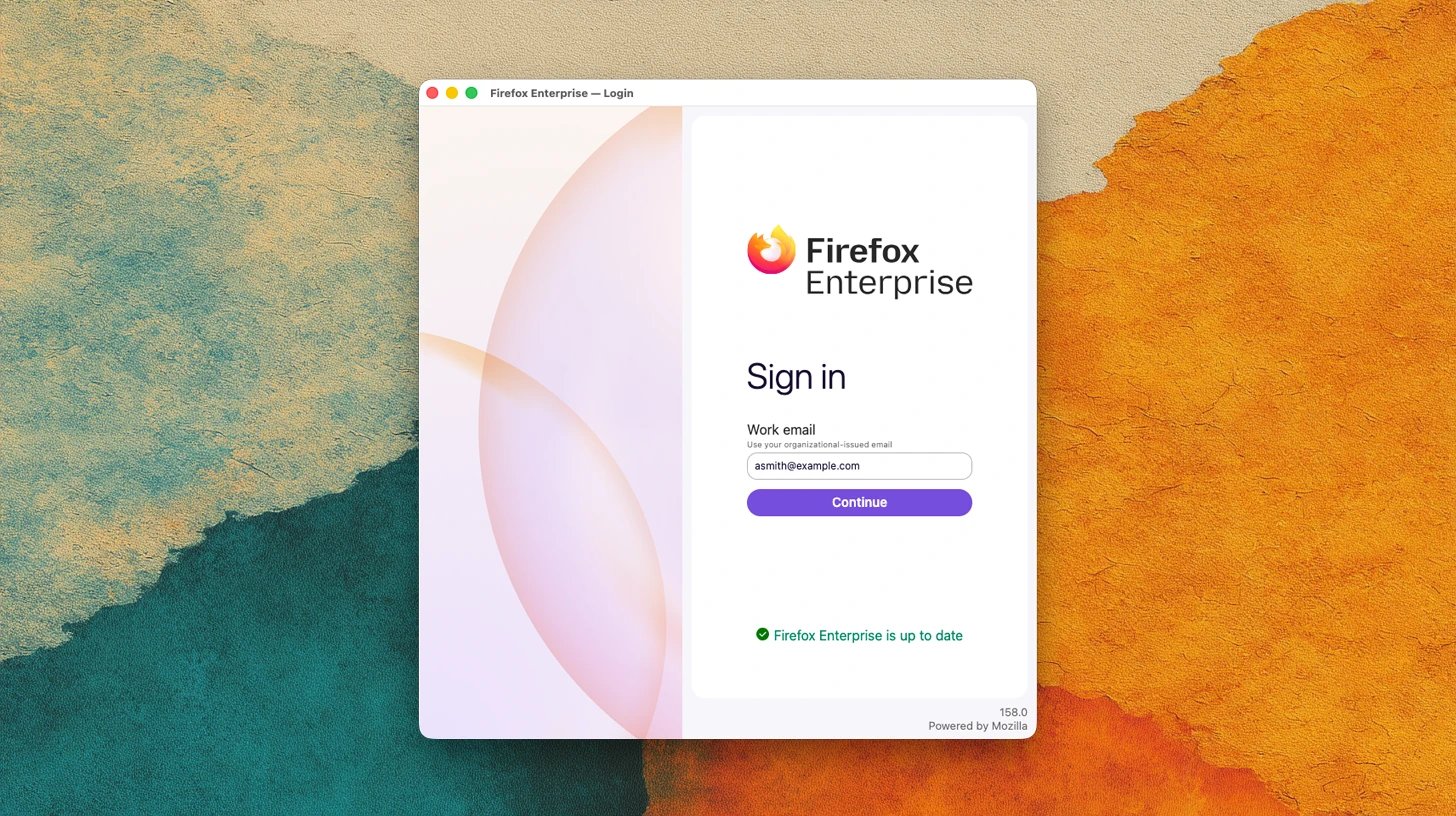
Mozilla Launches Firefox Enterprise for Enhanced Browser Security
Article Content

- •Firefox Enterprise allows organizations to manage browser policies and restrict AI tool usage.
- •The platform targets institutions with strict security and compliance requirements.
- •Mozilla emphasizes digital sovereignty by providing an alternative to dominant browser technologies.
Mozilla has launched Firefox Enterprise, a paid platform aimed at organizations with strict security needs. This platform allows IT teams to manage browser policies, restrict AI tool usage, and control data sharing within the browser. It features a management dashboard that organizations can host on their own infrastructure, enhancing data governance. Firefox Enterprise enables administrators to block or warn against actions like pasting sensitive information into unapproved AI services. The platform also includes device security checks before granting access, ensuring compliance with security requirements. Mozilla is initially focusing on markets in France, Germany, Austria, and Switzerland. The launch is part of Mozilla's strategy to provide an alternative to dominant browser technologies from Google and Apple, emphasizing digital sovereignty. Additionally, Mozilla is developing Thunderbird Enterprise to extend similar controls to email communications.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
Who can use Firefox Enterprise?
What features does Firefox Enterprise offer?
Which regions is Firefox Enterprise initially targeting?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…